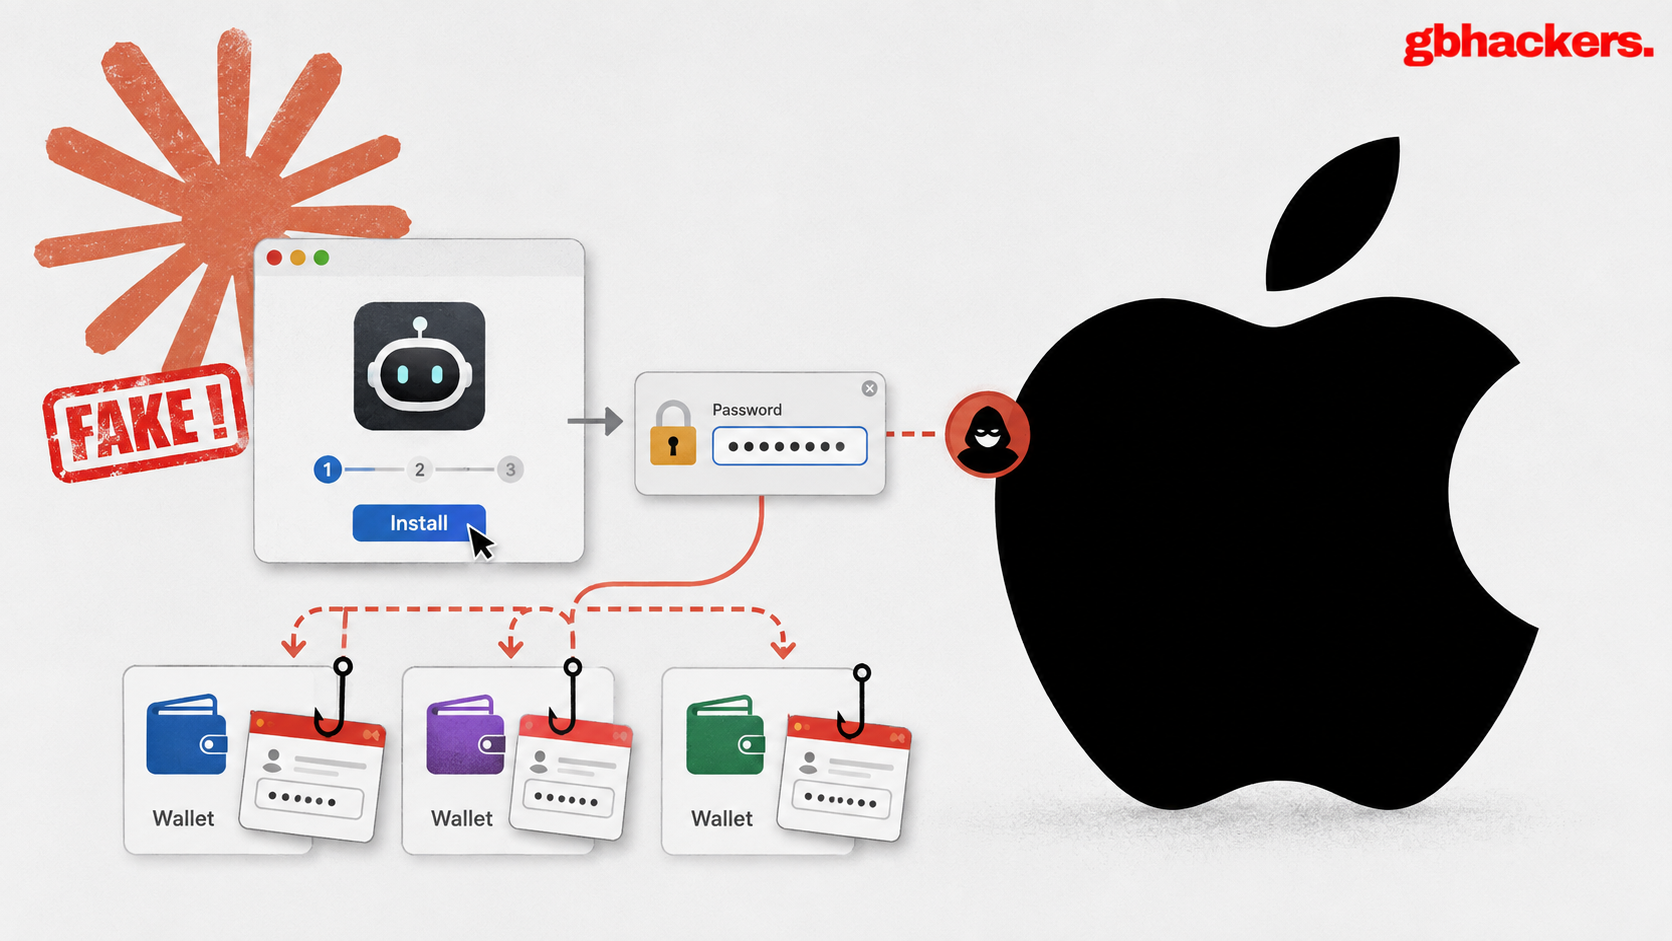

A Google-sponsored search result for Claude installation instructions is being used to deliver a sophisticated macOS stealer and remote-access trojan (RAT) named MacSync.
The campaign abuses a legitimate Claude shared-conversation page on the claude.ai domain, demonstrating how trusted AI-hosting infrastructure can be weaponized to bypass users’ normal phishing instincts.
The intrusion investigated by Huntress began when a Mac user searched for “How to Install Claude on a Mac” and clicked a paid search result.
Rather than sending the victim to an impersonation domain, the ad directed them to a public Claude Share URL.
The page was presented under the display name “Apple Support” and formatted as a plausible Claude Code installation guide.
Its central instruction was a malicious, Base64-obfuscated curl command that victims were told to paste into Terminal.
This ClickFix-style social-engineering technique moves execution outside the browser, making the victim an active participant in the compromise.
The first-stage loader is deliberately compact Huntress measured one observed sample at 1,442 bytes and unpacks a gzip-compressed payload embedded in Base64.
The loader is polymorphic and is generated per victim token, limiting the value of hash-based detection and shifting defensive focus toward behavioral telemetry such as suspicious curl, shell decoding, and zsh execution chains.

The decoded payload launches a background daemon_function that retrieves a dynamically served AppleScript payload, waits for collection to complete, exfiltrates a stolen-data archive, and removes staging artifacts.
Huntress Researchers said that, the command does not install Claude; it retrieves a small zsh loader that initiates a six-stage MacSync infection chain.
Fake Claude Steals Mac Passwords
Crucially, the AppleScript is served from attacker infrastructure and executed in memory, allowing operators to modify collection logic without updating the initial on-host loader.
The AppleScript attempts to socially engineer victims into granting macOS Transparency, Consent, and Control (TCC) permissions, including Full Disk Access.

It then prompts for the local macOS password, validates it, and targets Keychain items including Chromium “Safe Storage” material needed to decrypt browser cookies, stored credentials, and web data.
MacSync’s collection extends beyond browsers. Huntress reported theft of Keychain secrets, account passwords, Telegram sessions, SSH keys, and cloud credentials. The malware packages captured data into /tmp/osalogging.zip before exfiltration.
After credential theft, the malware installs a native Mach-O RAT in the user’s home directory.
The RAT establishes persistence through a LaunchAgent plist designed to execute at login, using a name derived from an updater already found on the host to blend in with expected software activity.

The component supports interactive shell access, command execution in the user context, file transfer, credential retrieval, and continued remote control.
Huntress also identified direct command-and-control activity over TLS-protected WebSocket traffic to 85.206.161.241:8443, alongside an obfuscated fallback delivery domain.
A separately signed helper seeks Screen Recording permission. Once the victim authorizes the TCC prompt, the helper can capture screen content to disk.
At the same time, the RAT handles collection and exfiltration, separating permission abuse from network operations.
MacSync’s most damaging feature is its final-stage wallet application manipulation. It checks for 60 wallet browser extensions, 21 desktop wallet applications, and three hardware-wallet companion applications, then copies, rewrites, and replaces selected apps with trojanized versions.
The altered applications wait until users launch software they already trust. One reconstructed Ledger-themed flow presented a fake error screen requesting the wallet recovery phrase.
Unlike passwords or browser sessions, a seed phrase cannot be rotated: once stolen, it can provide enduring control over every wallet derived from that seed.
Organizations should treat sponsored results and shared AI conversations as untrusted sources of installation guidance.
Restrict or alert on shell commands that combine curl, Base64 decoding, and immediate piping to zsh or bash; monitor osascript, unexpected TCC prompts, LaunchAgent creation, Keychain access, and modifications to wallet applications.
Users should obtain Claude Code and other software only from official vendor documentation and never paste an opaque Terminal command simply because it appears on a legitimate domain.
[Live Webinar] Join Elastic & UnderDefense to learn how small security teams can unify AI visibility and agentic response into one operating model. -> Register Now


 named MacSync.)