
Hackers are abusing fake download sites for popular tools like FinalShell and Xshell to deliver a new remote access trojan known as Kong RAT, in a highly staged and stealthy campaign that ran from at least May 2025 through March 2026.
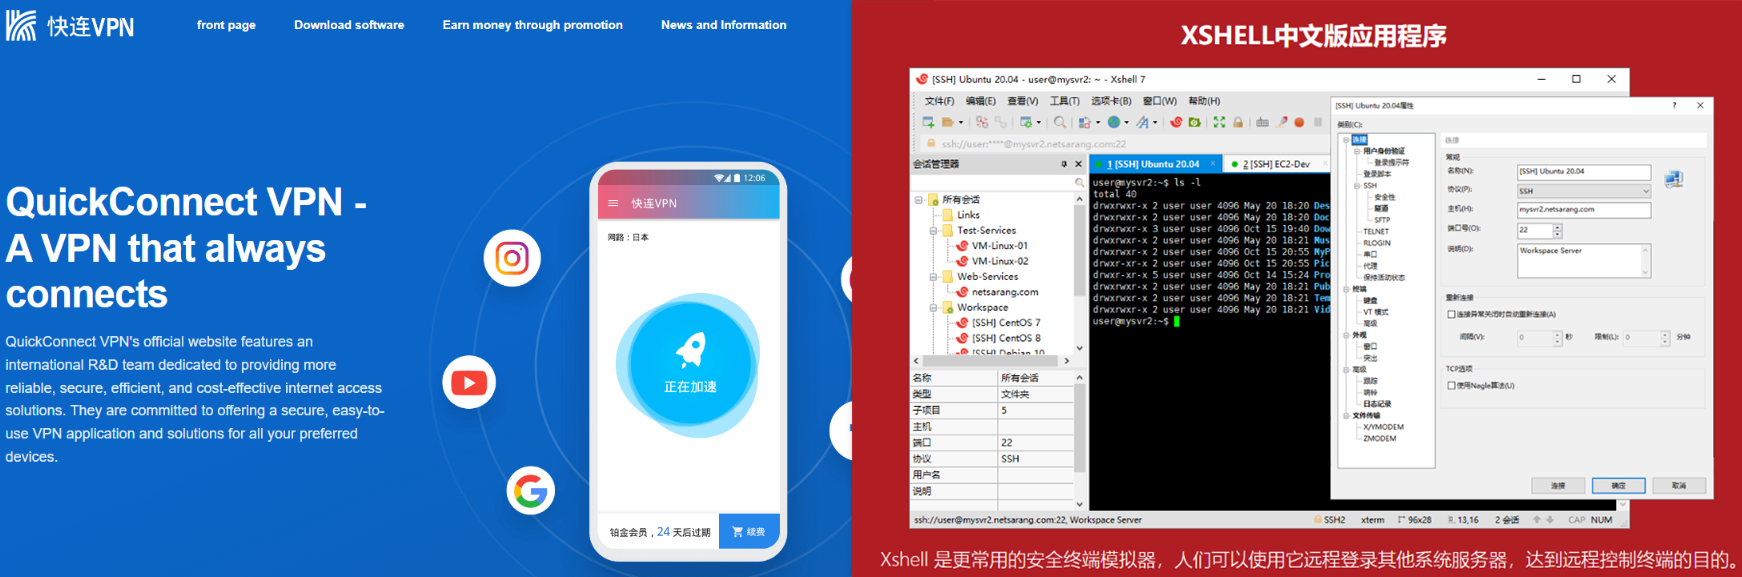
In this campaign, attackers poisoned search engine results so that Chinese‑speaking developers and IT admins looking for FinalShell, Xshell, QuickQ VPN, Clash proxy, or LeTV‑related VPNs were quietly funneled to lookalike domains that hosted trojanized installers.
These fake sites mimic real Chinese software portals so well that victims believe they are downloading trusted server management or VPN tools, while actually triggering a multi‑stage infection chain ending with Kong RAT on Windows systems.
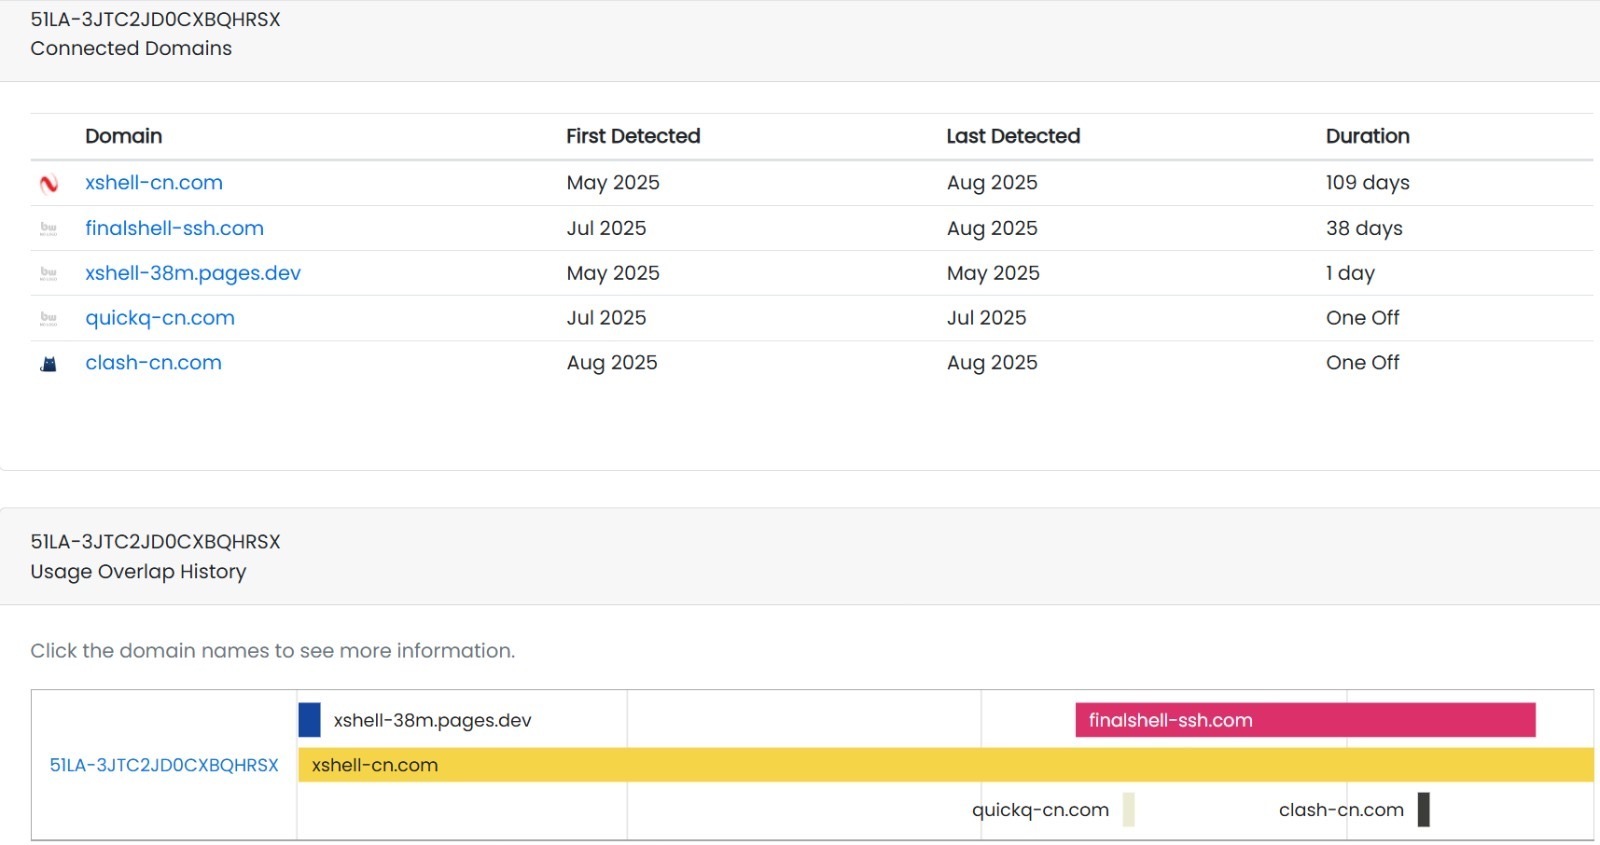
The operation relies on a cluster of spoofed domains, including xshell‑cn[.]com and finalshell‑ssh[.]com, registered with Hong Kong–based providers and all tied together by a shared analytics certificate ID 51LA‑3JTC2JD0CXBQHRSX.
In March 2026, eSentire’s Threat Response Unit detected a sophisticated multi-stage malware campaign targeting Chinese-speaking developers and IT professionals.
The fake FinalShell page at finalshell‑ssh[.]com is written entirely in Simplified Chinese, displays authentic‑looking FinalShell 4.2.4 screenshots, and offers “Windows” and “Mac” download buttons, but both links deliver the same Windows‑only malware installer finalshell‑SetupX64.exe.
Other lookalike sites, such as quickq‑cn[.]com and clash‑cn[.]com, target QuickQ VPN and Clash users, using the same infrastructure and analytics certificate to maintain a uniform delivery ecosystem.
Fake FinalShell and Xshell Sites
When a victim downloads from these spoofed sites, they receive a Setup.exe dropper compiled with .NET 10.0 NativeAOT, a deliberate choice to break common .NET reverse‑engineering tools like dnSpy and ILSpy by emitting native machine code instead of MSIL.
The embedded PDB path contains the username “52pojie,” referencing the well‑known Chinese cracking forum 52pojie[.]cn, suggesting a Chinese‑speaking developer, although this could also serve as a false flag.
On execution, the dropper checks for administrator rights, and if not elevated re‑launches itself with the runas verb to trigger a UAC prompt before downloading the next payload disguised as zj.mp4 from Alibaba Cloud Object Storage in the Hong Kong region.
Despite its .mp4 extension, zj.mp4 is actually a Windows 64‑bit DLL that is reflectively loaded in memory, and its exported function run orchestrates the next stage of the attack.
This stage constructs additional download URLs on kkwinapp.oss‑cn‑hongkong.aliyuncs.com using misleading extensions like .1×1, .d11 and .bin, then drops and hides files in the user’s LOCALAPPDATA directory with both HIDDEN and SYSTEM attributes to evade casual discovery.
For execution, the malware abuses DLL sideloading by placing a malicious rcdll.dll alongside a legitimate Microsoft‑signed binary (Setupexe.exe, actually rc.exe) so Windows loads the attacker’s DLL first when resolving dependencies.
The threat actor systematically targets popular Chinese developer and network tools including SSH clients (FinalShell, Xshell), VPN tools (QuickQ, Clash), and media platforms (LeTV).
Inside rcdll.dll, the malware defers execution using QueueUserAPC, then, if needed, silently re‑elevates privileges by combining PEB masquerading (making the process look like explorer.exe) with a CMSTPLUA COM UAC bypass that avoids any visible UAC prompts.
The shellcode is read from an oob.xml file that actually contains x64 shellcode followed by an embedded PE, copied into RWX memory and executed via EnumWindows callback, sidestepping CreateThread‑based detections commonly used by EDR products.
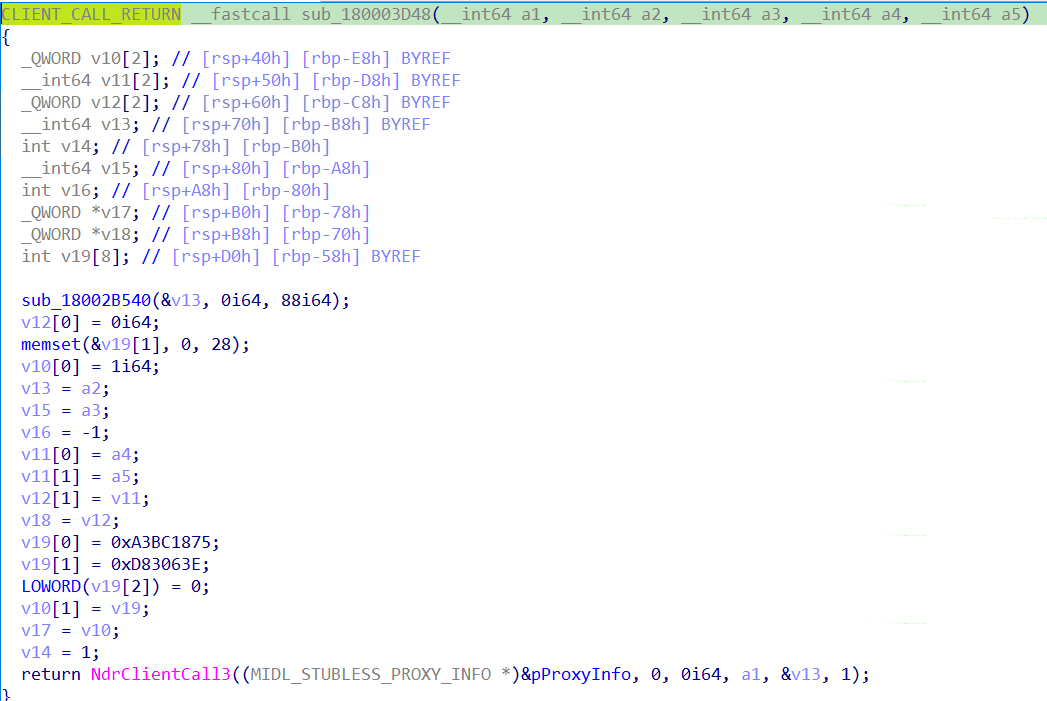
It also sets up a Windows Scheduled Task named “SimpleActivityScheduleTimer{GUID}” via direct RPC calls (NdrClientCall3), bypassing typical Task Scheduler COM interfaces and ensuring persistence with a non‑deterministic but reliably patterned task name.
The final embedded executable is Kong RAT, a 64‑bit Windows RAT that enforces single‑instance execution via a mutex, prevents system sleep using PowerSetRequest, and starts a configurable keylogger unless disabled by the KONGSKIPKEYLOGGER environment variable.
Kong RAT communicates with a C2 domain of the form x.x‑x[.]icu over TCP port 5947 using a custom “MPK1” binary protocol with LZ4 compression and a 4‑byte length prefix, supporting at least 16 command types for remote shell, file operations, reboot, self‑destruct, C2 migration, and hot‑plug DLL module loading.
It also queries WMI for installed antivirus products, abuses the LeTV CDN endpoint g3.letv[.]com/r?format=1 to collect the victim’s public IP and geographic description, and searches for Chinese messaging apps like WeChat, WeCom, QQ, as well as Telegram and WhatsApp, reinforcing its focus on Chinese‑speaking users.
Defenders should monitor for traffic to the listed fake domains and to kkwinapp.oss‑cn‑hongkong.aliyuncs.com, as well as unusual MP4, .1×1, .d11 and .bin downloads from Alibaba Cloud in Hong Kong.
Additional high‑value indicators include Scheduled Tasks starting with “SimpleActivityScheduleTimer,” the presence of Setupexe.exe and rcdll.dll in user profile paths, and C2 traffic over TCP 5947 using a custom MPK1 header, all of which strongly point to Kong RAT activity.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


