

Fake screenshot links are being used to quietly deploy a multi‑stage backdoor against Web3 customer support teams, in a campaign assessed to be linked to the Chinese financially motivated group APT‑Q‑27 (GoldenEyeDog).
The operation abuses live chat workflows, signed .NET loaders, AWS S3 dead drops, and DLL sideloading to land a memory‑resident Farfli backdoor that talks to dozens of hard‑coded command‑and‑control (C2) servers over a non‑standard port.
The attack begins in a support chat, where an attacker posing as a user shares what looks like a screenshot link, complete with a “Google”‑looking URL and a filename that resembles a photo.
On Windows systems with default settings, the executable extension is hidden, so the file appears harmless even though it is actually a .pif program.
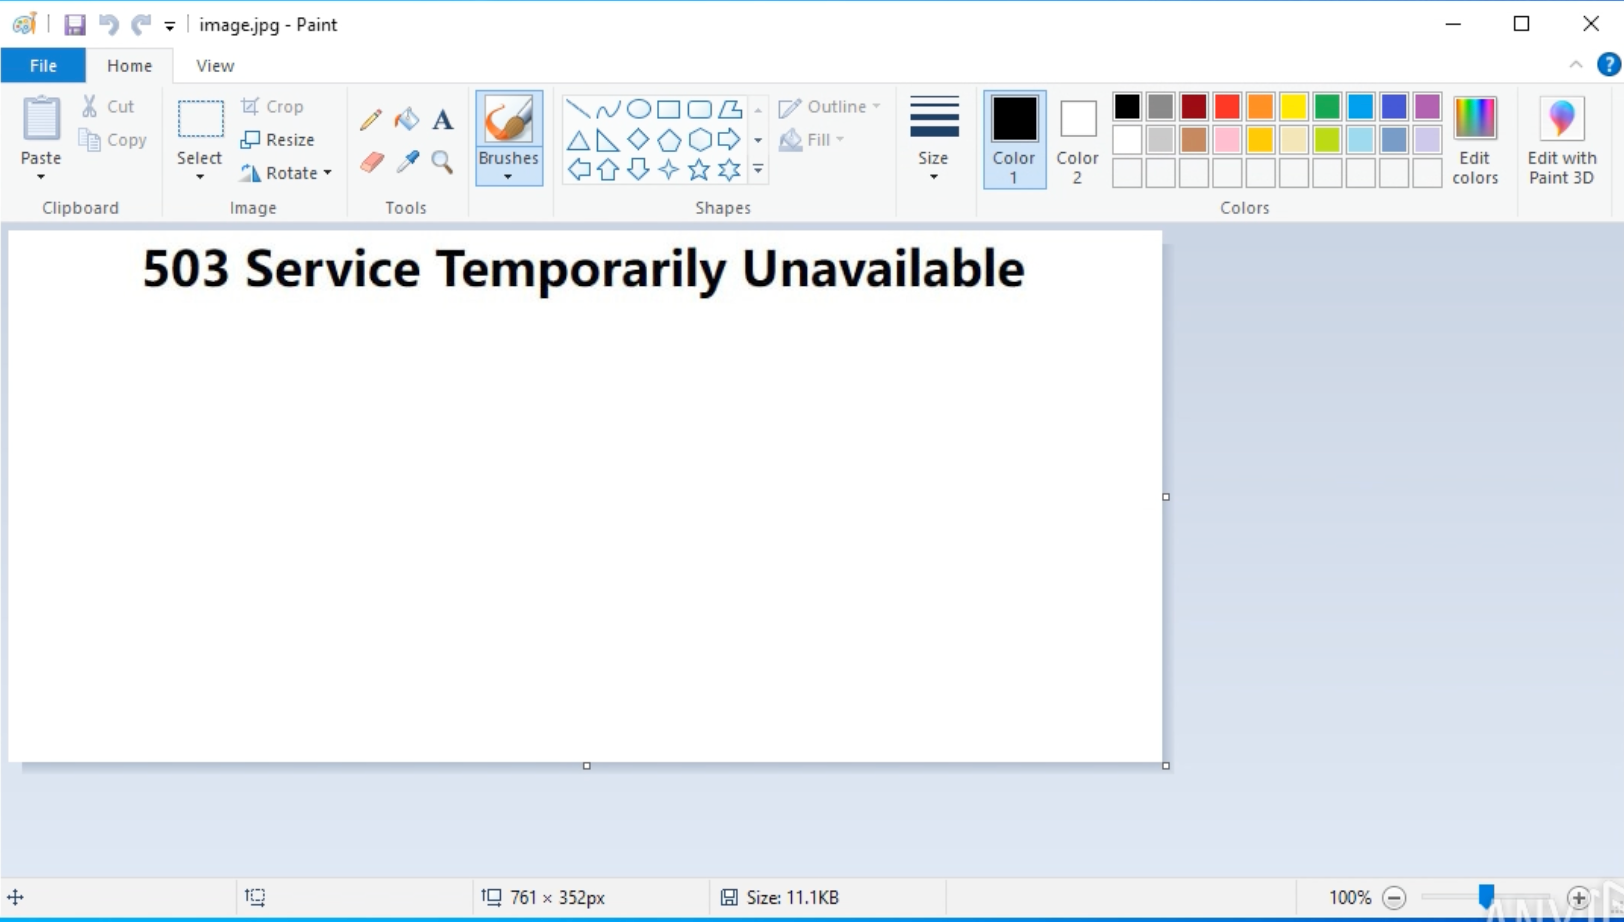
When opened, it shows a fake error image or opens in Microsoft Paint, giving the impression of a broken link while silently launching a .NET downloader in the background.
1inch and zeroShadow uncovers an active APT-Q-27 campaign targeting web3 customer support teams via live chat.
This first‑stage malware, signed with a legitimate but abused EV certificate, reaches out to an AWS S3 “dead drop” manifest (for example, y.txt or A.txt) that lists second‑stage payload URLs.
It creates a hidden staging directory under the user’s AppData that impersonates a Windows Update cache and includes a distinctive “@27” tag, then pulls down a bundle of DLLs, executables, logs, and images into that path.
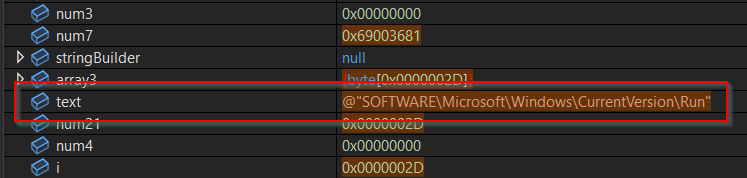
Persistence is established via a Run registry key pointing to a fake “SystemUpdats” value, ensuring the malware survives reboots without obvious user prompts.
Obfuscation, staging, and sideloading
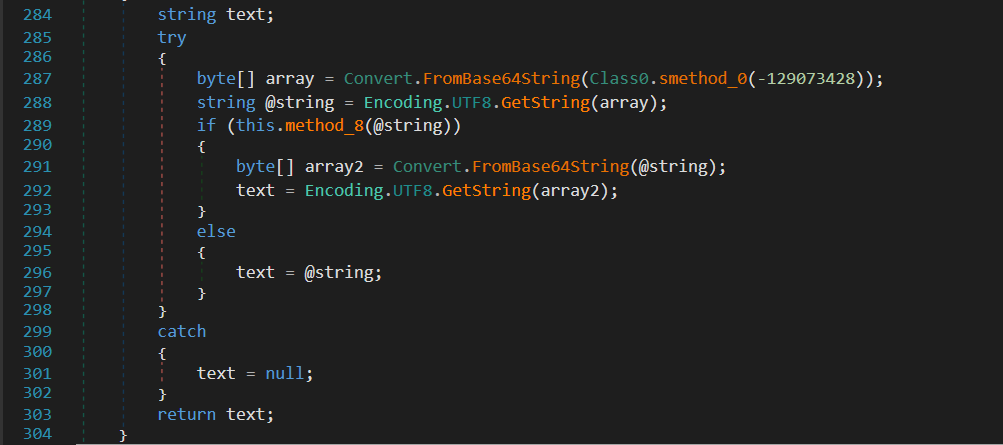
The .NET loaders (including variants such as Feedback.exe and photo2025060268jpg.exe) are heavily obfuscated, with all meaningful strings decrypted at runtime through a custom scheme and some key values hidden behind double Base64 encoding.
Anti‑debug checks, stack inspection, and junk control flow frustrate static analysis and sandboxes, while flexible manifest parsing allows operators to rotate infrastructure or encode URLs without changing the binary.
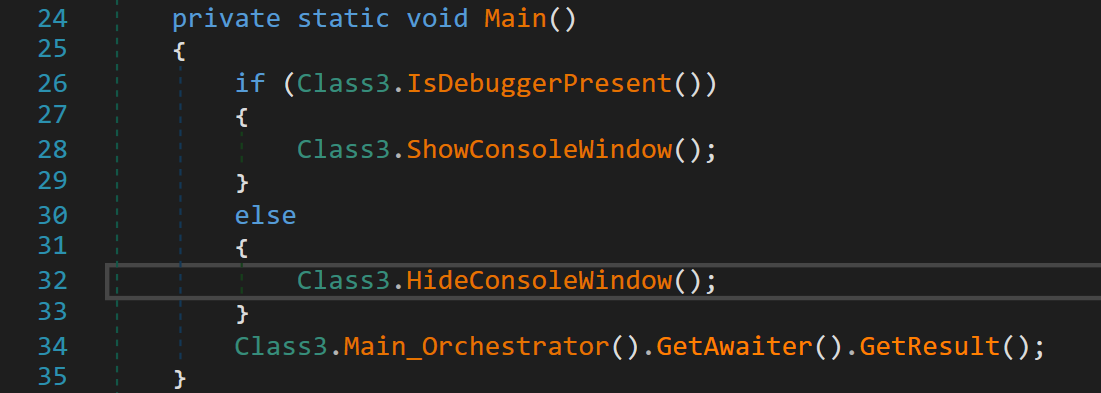
The binary calls the Win32 API IsDebuggerPresent and additionally performs a stack trace inspection, examining the call stack to determine whether execution is occurring within a debugger context.
If the S3 dead drop is unavailable, the loaders can fall back to downloading legitimate Microsoft VC++ redistributables, blending into normal software installation traffic.
Once staged, the chain abuses a legitimate YY platform binary (updat.exe) for DLL sideloading.
Because this signed executable imports vcruntime140.dll and msvcp140.dll, malicious replacements dropped into the working directory are loaded instead of the real runtime, which in turn load crashreport.dll and decrypt an encrypted log file (yyext.log) into memory.
That log actually contains shellcode which decompresses a UPX‑packed PE, ultimately unpacking a 32‑bit Farfli backdoor DLL fully in memory, leaving no standalone implant on disk.
The final Farfli stage maintains a list of 37 hard‑coded C2 IP addresses, protected by a rolling XOR string encryption scheme and contacted over TCP port 15628, a port repeatedly seen in previous reporting on this family.
The implant focuses on stealth and persistence: it checks for administrative context, tampers with User Account Control (UAC) registry keys to suppress prompts, registers itself as a Windows service under the name “Windows Eventn,” and uses watchdog loops to relaunch if killed.
The binary’s string heap is entirely empty, there are no readable strings are present in the .NET metadata, and static analysis tools that rely on the #US heap to recover string literals will find nothing of value.
Some of the infrastructure overlaps with networks and ASNs previously tied to APT‑Q‑27/GoldenEyeDog, a group known for targeting gambling and cryptocurrency ecosystems using modular backdoors such as Farfli and Silver Fox.
Attribution is not definitive, but overlaps span tooling, infrastructure, and behaviours: the @27 tag in staging paths, abuse of Chinese‑registered EV certificates, use of YY binaries for sideloading, and long‑lived C2 nodes in Asian hosting.
This campaign also marks a strategic shift for the group from SEO‑driven watering holes and fake download sites to direct engagement with front‑line staff in live support channels, exploiting the high‑trust, high‑speed nature of Web3 support workflows.
Detection and practical defenses
For defenders, several high‑fidelity host and network indicators emerge from this chain. On endpoints, monitor for creation of AppData paths mimicking Windows Update with “@27” in the folder name, registry Run entries named “SystemUpdats,” new services called “Windows Eventn,” and UAC settings (EnableLUA, ConsentPromptBehaviorAdmin, PromptOnSecureDesktop) being set to 0 in close succession.
Once the payload components are in place, the malware writes a value to HKCU\SOFTWARE\Microsoft\Windows\CurrentVersion\Run pointing to updat.exe in the staging directory.
In memory, hunting for the specific 16‑byte XOR key and the config delimiter stimiter string “|#$|” can surface active implants, while on the wire, any outbound traffic over TCP port 15628 to the documented C2 IP ranges should be blocked and investigated.
Equally important is hardening the human and platform side of support operations. Enforcing visible file extensions on Windows, sandboxing file handling for support agents, and adding guardrails around clicking or executing files received via chat can drastically reduce risk from look‑alike “screenshot” links.
For Web3 firms, where a compromised support workstation can quickly translate into drained wallets or hijacked admin sessions, treating support environments as high‑value assets complete with strict EDR coverage, least‑privilege access, and dedicated phishing training has now become a baseline control, not a luxury.
Indicators Of Compromise (IOCs)
| FILENAME | DESCRIPTION | FILEHASH (SHA256) |
|---|---|---|
| Photo2025060268jpg.exe (WindowsForApp.exe) | Loader variant, initial lure as fake image | 1a80f721ab125b88e5baf77dd2bf01be92ff5299665356621b21306a71c86672 |
| Feedback.exe | Loader variant, .NET dropper/loader | d6b96b68057e39d61ea0084885ef6541121d83c31b26b35b2f435bb7f8b59932 |
| updat.exe | Legitimate signed YY platform binary, sideloading vehicle | 393ed141aca95973d948b0becd128ac19b7140fa66f80400c15cc48c2fbfe454 |
| vcruntime140.dll | Malicious VC++ runtime, sideload stage 1 | 8e08575492175e042f093f325b07a5c14ca71e7c581474838db3d48f5aab1312 |
| msvcp140.dll | Malicious VC++ runtime, sideload stage 2 | e4c71980dbb4a1e1a86816687afdaea043b639b531135fc4516fb2429fe623fc |
| crashreport.dll | Decrypts and executes yyext.log shellcode | 2c35150e0d2da30b689d25f48e4039e35f48501afd2c486bdaf81b6df228104d |
| yyext.log | Encrypted x86 shellcode, decompresses and loads final DLL | fc3fdbfbee3e358813370b324decf317c8481a1ad841dec0e5dabffd37af1386 |
| Final stage DLL | Backdoor implant, runs in memory | c89f1c5d54c1c954b91783037898ce8b67a3057b5b43213210c34d81b10387b8 |
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


