

A previously unknown cyber sabotage framework called fast16, whose core components date back to 2005. This makes it the earliest known sabotage malware of its kind, predating the infamous Stuxnet worm by at least five years.
The fast16 framework consists of two primary components: a Lua-powered service binary called svcmgmt.exe and a kernel driver named fast16.sys.
The malware selectively targets high-precision calculation software, patching code in memory to tamper with computational results. By combining this payload with self-propagation mechanisms, the attackers aimed to produce inaccurate calculations across entire facilities.
The kernel driver fast16.sys operates as a boot-start filesystem component that intercepts and modifies executable code as it’s read from disk.
SentinelLABS has uncovered a previously undocumented cyber sabotage framework whose core components date back to 2005, tracked as fast16.
It specifically targets executables compiled with the Intel C/C++ compiler and includes a rule-driven patching engine configured with 101 distinct rules for pattern matching and code replacement.
Strategic Targets and Purpose
The malware was designed to attack ultra-expensive, high-precision computing workloads of national importance, including advanced physics, cryptographic, and nuclear research applications.
Internally, svcmgmt.exe stores three distinct payloads, including encrypted Lua bytecode that handles configuration.
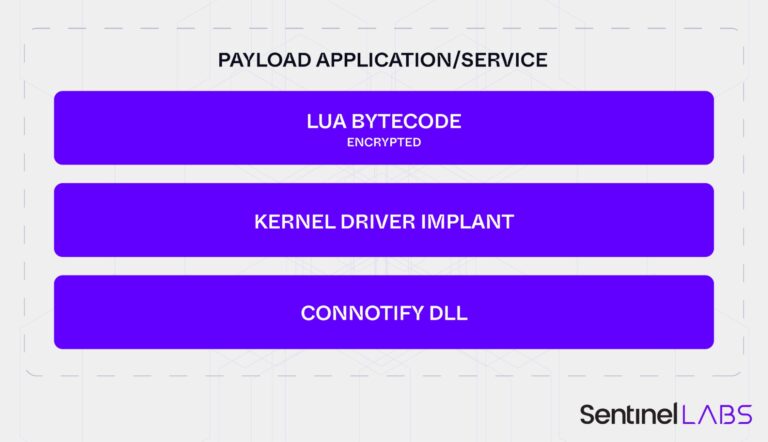
SentinelOne identified three potential target software suites: LS-DYNA 970 (used for crash testing and structural analysis), PKPM (Chinese structural engineering software), and the MOHID hydrodynamic modeling platform.
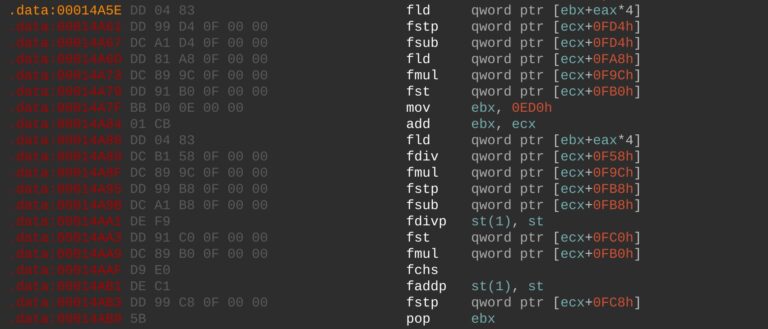
Analysis reveals that fast16 contains specialized floating-point unit instructions dedicated to corrupting precision arithmetic routines.
This moves the malware beyond typical espionage tools into the realm of strategic sabotage, as introducing systematic errors into physical-world calculations could undermine scientific research programs, degrade engineered systems, or contribute to catastrophic damage.
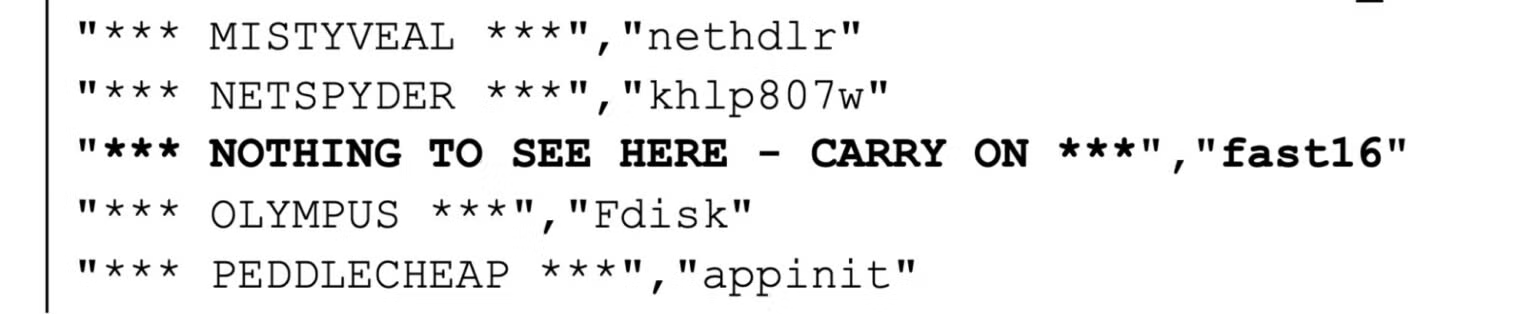
The name ‘fast16′ appears in the infamous ShadowBrokers’ leak of NSA’s ‘Territorial Dispute’ components from 2017. A deconfliction signature instructing operators states: “fast16 * Nothing to see here – carry on *”.
The malware’s presence in NSA leak materials, combined with public reporting linking LS-DYNA software to Iran’s nuclear weapons development research, suggests fast16 may have been deployed against Iran’s nuclear program years before Stuxnet.
Advanced Development Techniques
Fast16 demonstrates sophisticated engineering that was unprecedented for 2005. The malware uses an embedded Lua 5.0 virtual machine for modularity, predating similar techniques in Flame by three years.
Most patterns correspond to ordinary x86 instructions, but one stands out: a larger block of floating-point (FPU) code dedicated to precision arithmetic.
The framework includes environmental awareness capabilities, checking for the presence of security products before installation and aborting deployment in monitored environments.
For propagation, fast16 used default or weak passwords for file shares on Windows 2000 and XP systems, spreading through standard Windows service-control and file-sharing APIs rather than custom network protocols.
This wormable design allowed the malware to deploy the sabotage driver across multiple systems in a network, preventing independent verification of corrupted calculations.
The discovery forces a re-evaluation of the timeline of state-sponsored cyber sabotage operations, showing that sophisticated capabilities for undermining physical infrastructure through software existed far earlier than previously documented.
Indicators of Compromise
| Name | fast16.sys |
| MD5 | 0ff6abe0252d4f37a196a1231fae5f26 |
| SHA1 | 92e9dcaf7249110047ef121b7586c81d4b8cb4e5 |
| SHA256 | 07c69fc33271cf5a2ce03ac1fed7a3b16357aec093c5bf9ef61fbfa4348d0529 |
| Name | connotify.dll |
| MD5 | 410eddfc19de44249897986ecc8ac449 |
| SHA1 | 675cb83cec5f25ebbe8d9f90dea3d836fcb1c234 |
| SHA256 | 8fcb4d3d4df61719ee3da98241393779290e0efcd88a49e363e2a2dfbc04dae9 |
| Name | svcmgmt.exe |
| MD5 | dbe51eabebf9d4ef9581ef99844a2944 |
| SHA1 | de584703c78a60a56028f9834086facd1401b355 |
| SHA256 | 9a10e1faa86a5d39417cae44da5adf38824dfb9a16432e34df766aa1dc9e3525 |
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


