

A novel workaround exploit has been discovered by the experts at Sophos security firm, through which the hackers exploit the recently patched Microsoft Office vulnerability without using macros to Deliver Formbook malware.
This exploit allows the threat actors to execute several arbitrary codes and commands, in short, it’s an RCE (Remote Code Execution) flaw. The patched vulnerability is tracked as CVE-2021-40444 and it’s a remote code execution vulnerability.
Flaw Profile
- CVE ID: CVE-2021-40444
- Description: Microsoft MSHTML Remote Code Execution Vulnerability
- Severity: Critical
- CVSS: 8.8
- Released: Sep 7, 2021
- Last updated: Sep 23, 2021
In a Word document this vulnerability exploit a mechanism to download a Microsoft Cabinet (CAB) RAR archive loaded with a PowerShell and after that they use it to download a malicious payload.
Here’s what the cybersecurity analyst Andrew Brandt and Stephen Ormandy at SophosLabs stated:-
“The attachments represent an escalation of the attacker’s abuse of the CVE-2021-40444 bug and demonstrate that even a patch can’t always mitigate the actions of a motivated and sufficiently skilled attacker.”
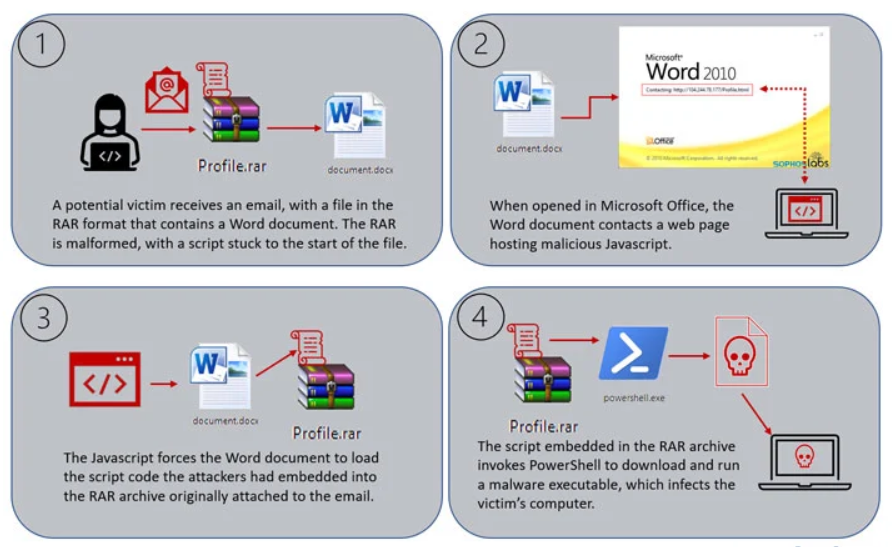
“In the initial versions of CVE-2021-40444 exploits, malicious Office document retrieved a malware payload packaged into a Microsoft Cabinet (or .CAB) file. When Microsoft’s patch closed that loophole, attackers discovered they could use a different attack chain altogether by enclosing the maldoc in a specially crafted RAR archive.”
Formbook & Its Abilities
Formbook malware is a data-harvesting malware that steals the following things from the cpmromised systems:-
- Steals credentials from browsers
- Collect screenshots
- Steals all the logging keystrokes
This malware strain has been detected recently in COVID-19-themed phishing campaigns, and their it has been uncovered that this malware also has the ability to download and execute any files from a C2 server.
Between October 24 and 25 the modified version of the exploit, that is dubbed as CAB-less 40444 lasted for 36 hours. And in this time interval, the threat actors have sent spam emails to all the potential victims with a malformed RAR archive file.
As a recommendation, the analysts have recommended users that in Internet Explorer they have to disable the installation of all ActiveX controls to mitigate this attack.
But, the most important thing that every organization should adopt is the proper cyber risk management skills and education, as this will keep organizations and their employees safe from attacks like this.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.






