

Fxmsp is a collective of Russian- and English-speaking hackers, they are primarily targeting on highly protected networks to exfiltrate sensitive details from corporate’s and government entities.
The hacking group operating since 2017 and they know for targeting corporate and government networks worldwide.
According to the new report from Advanced Intelligence LLC, the hacker group has stolen “source code related to the companies’ software development and offering to sell it, and network access, for over $300,000.”
From 2017 and 2018, the group promotes various data breaches on the dark web markets, they recently developed “credential-stealing botnet capable of infecting high-profile targets to exfiltrate sensitive usernames and passwords,” and their main goal is to focus on secured systems.
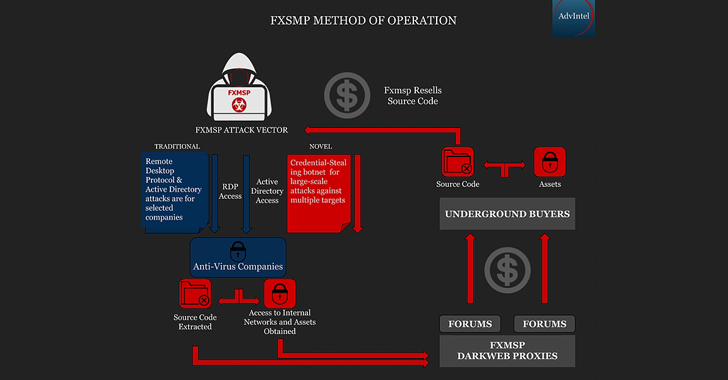
Starting this April 24, 2019, the hacking group claims they have hacked three antivirus companies and extracted sensitive source code from antivirus software, AI, and security plugins from the companies.
They also commented that they have analyzed the different companies’ software and assessed their efficiency, reads the AdvIntel report.
Based on the screenshot offered by Fxmsp, they purported to contain 30 terabytes of data, which extracted from the antivirus companies networks and not disclosing the company names.

“The folders seem to contain information about the company’s development documentation, artificial intelligence model, web security software, and antivirus software base code.”
the group offered privately to sell the source code and network access to all three companies for “over $300,000,” Yelisey Boguslavskiy said to Ars Technica.
The actor claimed that antivirus breach research had been their main project over the last six months, Advanced Intelligence researchers said, “Fxmsp is a credible hacking collective that has a history of selling verifiable corporate breaches returning them profit close to USD 1,000,000.”
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity updates also you can take the Best Cybersecurity courses online to keep your self-updated.
Also Read:
Microsoft Exchange Server Zero-day Flaw Exploit Provide Highest Admin Privilege to Hackers
Microsoft Releases Security Advisory for Privilege Escalation Vulnerability With Exchange Server







