
GoFlateLoader, a widespread Golang loader that has become a go-to delivery mechanism for multiple infostealers including Lumma, Vidar, StealC, Amatera and Remus.
GoFlateLoader’s design is intentionally unspectacular: its code implements a straightforward in-memory manual PE loader, lacking anti-debugging, anti-VM, API hashing or control-flow obfuscation.
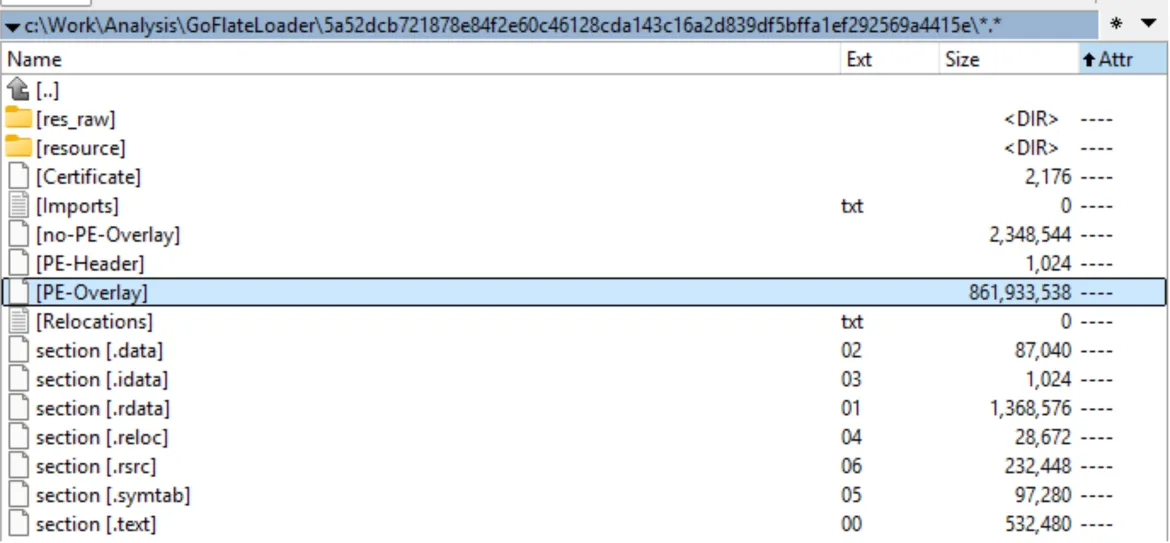
The loader’s operational stealth instead relies on an arguably low-tech but effective trick a massive PE overlay appended to the binary to inflate file size and frustrate detection and automated analysis.
Functionally, GoFlateLoader follows a compact, deterministic flow. The loader copies an encoded payload blob from its .rdata section to the stack, applies a small multi-stage byte-level decoding routine to reconstruct a valid PE, parses the decoded PE headers (image base, section table, data directories), allocates an RWX region via VirtualAlloc.
Notably, the transfer uses Go’s syscall.Syscall as a generic call gate: the loader sets the trap pointer to the payload entry point and uses hardcoded dummy arguments (1, 2, 3, 4).
That pattern syscall.Syscall with filler args is unusual and represents a detection opportunity when correlated with other indicators.
The loader also contains significant junk/decoy code that varies across builds to inflate complexity for static analysis but does not affect runtime behavior.
Gen Threat Labs has been tracking GoFlateLoader, a widespread Golang loader used to deliver multiple infostealers.
What defines GoFlateLoader is its consistent use of extremely large PE overlays samples typically measure between 700 and 950 MB. Overlays are usually filled with null bytes (occasionally random padding), producing an executable whose inflated on-disk size compresses down dramatically, so distribution via archive is economical for attackers.
GoFlateLoader Hides Infostealers
The motive is pragmatic: many antivirus and EDR solutions impose practical size limits for deep scanning or emulation to preserve performance, and automated analysis sandboxes and intelligence platforms impose hard upload caps (VirusTotal’s 650 MB limit is a likely target).
By sitting above such thresholds, GoFlateLoader aims to avoid thorough static and dynamic inspection and to provoke timeouts or drops in automated pipelines.
Gen Threat Labs links GoFlateLoader distribution to two main vectors: cracked software packages and a malicious TDS (traffic distribution system) recently analyzed by Check Point Research.
The TDS redirects victims to landing pages that serve password-protected archives; the archive password is shown separately on the page, preventing automated scanners that lack the password from extracting and analyzing the binary.
Compression reduces the on-disk impact of the overlay and the password gating increases operational safety for the actor, allowing the payload to remain encrypted until a human extracts it.
GoFlateLoader is architecture-aware, with both x86 and x86-64 builds matched to the intended infostealer payload. The loader has been observed delivering a family of prevalent information stealers: Lumma, Vidar, StealC, Amatera and Remus (among others such as SvitStealer).
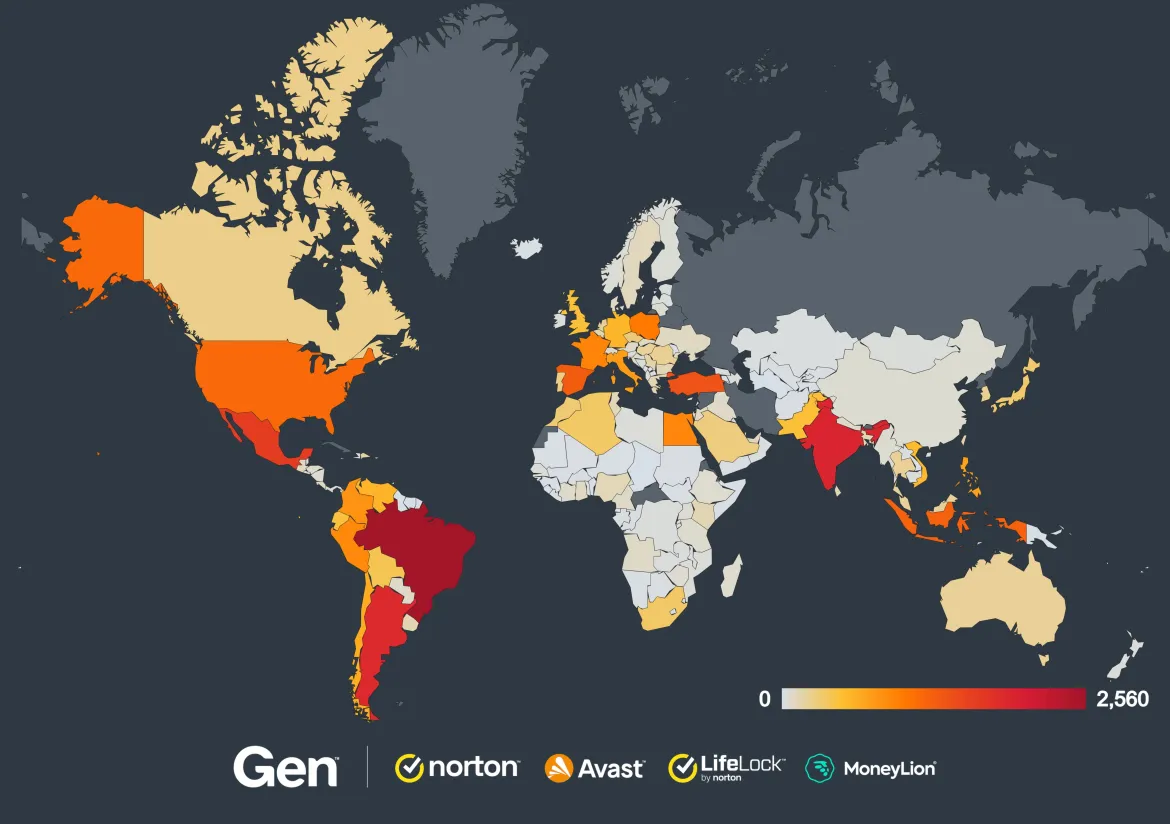
Despite its lack of sophistication, it has proven effective; since April 2026 Gen Threat Labs reports protecting over 33,000 unique users from GoFlateLoader, with notable prevalence in Brazil, India, Argentina, Mexico, Turkey and Spain.
Detection opportunities include the artifact of syscall.Syscall used as a call gate with constant dummy arguments, consistent presence of a large PE overlay, and the loader’s static patterns (decoded payload stored in .rdata, manual PE mapping sequence).
Defenders should enforce strict controls on installation of cracked software, block known TDS landing pages and archives, and ensure sandboxing/analysis pipelines can handle large compressed artifacts or implement policy to automatically extract password-protected archives when a page-provided password is present.
Indicators of Compromise (IoCs)
Note: The files listed in the IoCs that are not archives all exceed 650 MB in size and are therefore not available on VirusTotal.
b88c5744975d2abb447aecc6c090fee9f8580413f4612eecdc6ed1973e8a1739 (password-protected archive containing GoFlateLoader x64 variant loading Remus; pwd: 1234).
ed5ae7f36453c5a23e9868a5729d67e0549a11f6dea54f5f52d654a8f51d4902 (archive containing GoFlateLoader x64 variant loading Remus).
841c9297cb8a2e0ff89433d13c05bfc760eb2e98e251cb8fa785d2ad7cbac05f (archive containing GoFlateLoader x86 variant loading Amatera).
ece7c48eb411b24f26762ede83badb4a644c41d5777129381ac2541804d64fc2 (archive containing GoFlateLoader x86 variant loading Lumma).
421ce2d2f49c23bbe9f60ef3b9cd38d7eb912ce02e56a61837656210069bd9e2 (archive containing GoFlateLoader x64 variant loading Vidar).
121c2dc793b3873f75a29ec02241f94136de19c049382a50a50d0d5b99507073 (GoFlateLoader x64 variant loading StealC).
2415db5081cec9bfd14ad6da1a66169fd96f13a49010c319a73d1ed6fafd4efa (GoFlateLoader x64 variant loading Vidar).
d9917ade3b4c125a95b5d3e6343cde26145dfbf569bd7e2a843fd0c6fc8ddc28 (GoFlateLoader x64 variant loading Remus).
4cf6893756f441522b94b36f10e5de0e47aeed4743f95c51650746d1ecf97e3d (GoFlateLoader x64 variant loading SvitStealer).
8b89d6c9152d3aab97aadd515ecb69ca72654db2f25425759ba4b646853d737d (GoFlateLoader x86 variant loading Lumma).
90ce4ff9da23ac150da0a8e17930cab1e369aa349fdc1b65691b70369145664a (GoFlateLoader x86 variant loading Amatera).
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


