

Hackers are exploiting Google Cloud Storage to bypass email and web filters and deliver Remcos RAT through convincing Google Drive–themed phishing campaigns that blend social engineering with fileless, multi‑stage execution chains.
Phishing emails link to Google Cloud Storage buckets named “com-bid” or “contract-bid-0,” presenting what appears to be a standard Google Drive document access request.
Because both the sending and hosting infrastructure belong to Google, messages often pass DMARC, SPF, and DKIM checks and slide past legacy secure email gateways.
ANY.RUN researchers recently documented a phishing operation that hosts malicious HTML on storage.googleapis.com, abusing Google’s trusted cloud infrastructure to evade URL and reputation‑based filtering.
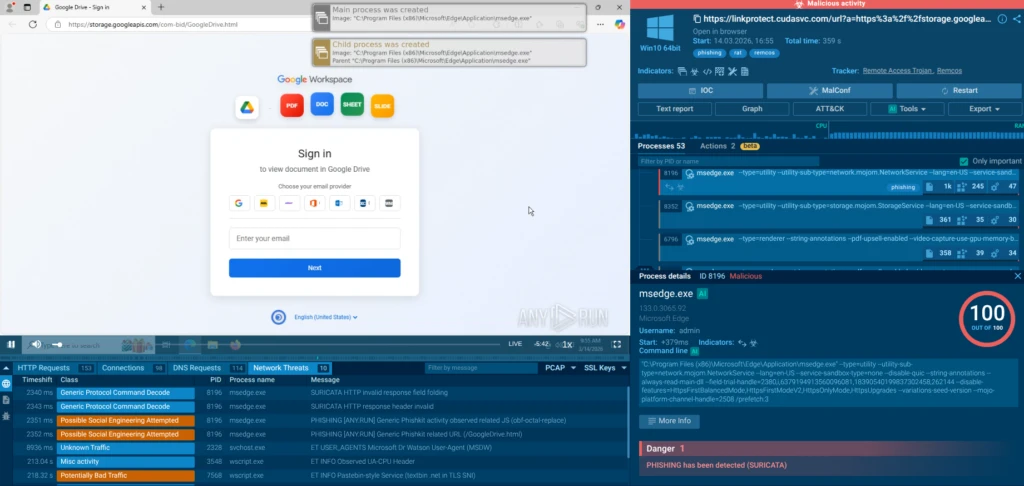
Once the victim clicks, they are taken to a Google Drive–style login page that closely mimics legitimate Google Workspace flows, complete with logos and familiar file‑type icons.
These pages harvest full account credentials, including passwords and one‑time passcodes, before moving the victim into the malware delivery phase.
Multi‑Stage, Mostly Fileless Infection Chain
After “successful” authentication, users are prompted to download a JavaScript file named Bid-Packet-INV-Document.js, presented as a business document or bid packet.
Executed under Windows Script Host, this script includes time‑based evasion to delay malicious activity and outwait automated sandboxes with short analysis windows.
The script then launches a VBS-based chain: an initial VBS downloader retrieves a second VBS stage that drops components into a folder like %APPDATA%\WindowsUpdate and configures startup persistence to survive reboots.
A PowerShell script (e.g., DYHVQ.ps1) orchestrates loading an obfuscated executable stored as a temporary .tmp file and simultaneously pulls an additional .NET loader from a text‑hosting service, executing it directly in memory via Assembly. Load to avoid writing a detectable payload to disk.
The .NET loader abuses the signed Microsoft binary RegSvcs.exe for process hollowing, starting the trusted process from %TEMP% and injecting the Remcos payload into its memory space.
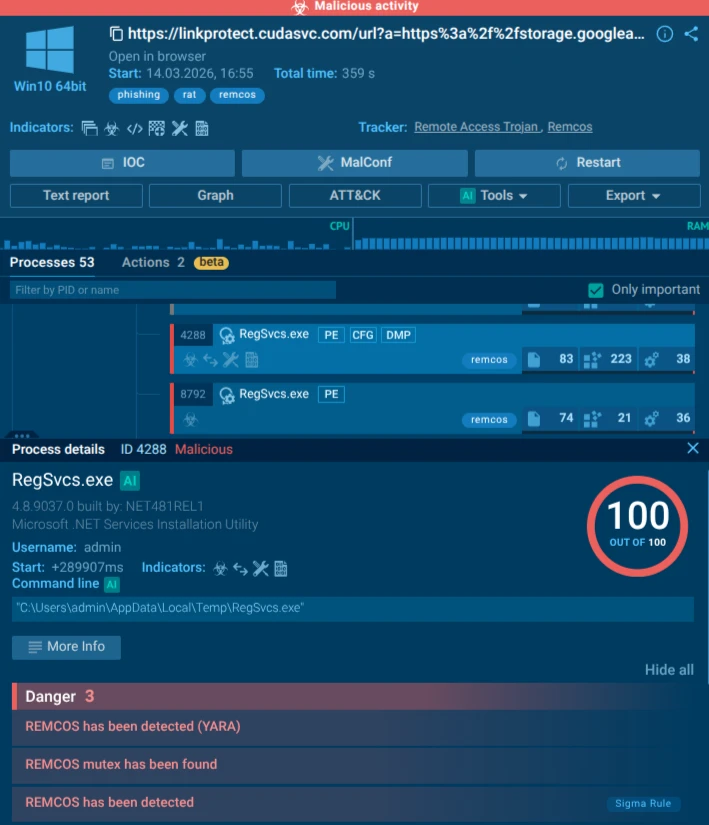
This produces a partially fileless Remcos instance whose malicious behavior runs inside a legitimate, clean‑reputation process, making static, file‑hash‑based EDR rules largely ineffective.
Once active, Remcos RAT establishes encrypted command‑and‑control communications and writes persistence entries under registry keys such as HKEY_CURRENT_USER\Software\Remcos-{ID}.
This capability turns a single compromised endpoint into a long‑term beachhead for ransomware deployment, lateral movement, and data exfiltration of sensitive documents or customer records.
Why Legacy Defenses Fail
This campaign shows how attackers “borrow” the trust of major cloud providers instead of standing up obviously malicious infrastructure.
Google Storage and a signed Microsoft binary both enjoy strong reputation scores, so filters that rely on known‑bad domains, hashes, or static indicators often see nothing suspicious.
Combined with heavy obfuscation, time‑delayed execution, and in‑memory loading, the approach breaks traditional assumptions about what malicious traffic and binaries look like.
ANY.RUN’s 2025 malware trends reporting notes that RATs and backdoors are surging in prevalence, with multi‑stage, trusted‑cloud phishing now a leading delivery vector, underscoring why early, behavior‑based detection is now a business continuity requirement rather than a purely technical goal.
To counter these attacks, defenders must analyze what actually happens after a link is clicked or a script runs tracking process trees, registry changes, and network beacons rather than trusting reputation alone.
Interactive sandboxing, such as ANY.RUN’s cloud environment, allows analysts to manually drive the full chain from phishing URL to Remcos C2 callback, defeating time‑delay and anti‑automation logic and exposing every stage of the kill chain.
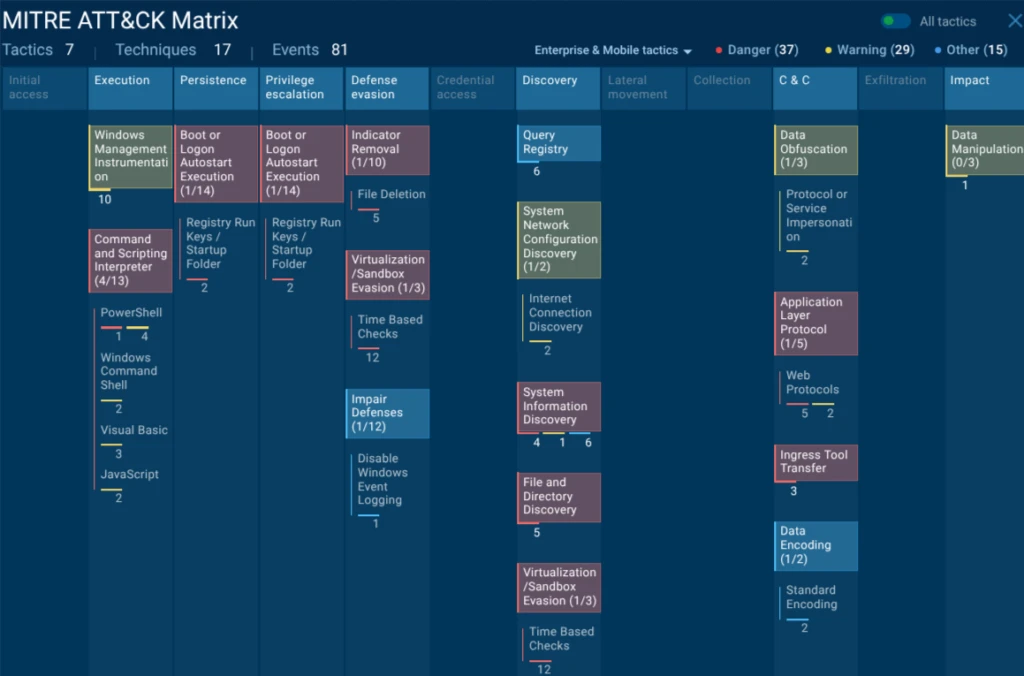
From this behavioral map, teams can derive MITRE ATT&CK‑mapped techniques, Sigma rules, and concrete IOCs that can be operationalized across SIEM, EDR, and network controls.
ANY.RUN’s Threat Intelligence Lookup and Threat Intelligence Feeds then extend this advantage by correlating indicators like C2 IPs, anomalous RegSvcs.exe behavior, and specific script signatures across a large community dataset, surfacing related Remcos activity and feeding high‑fidelity, malicious‑only indicators into SOC workflows.
In an era where “legitimate” infrastructure is routinely weaponized, such behavioral and intelligence‑driven defenses are essential to detect and contain trust‑abuse phishing before the next bid document drops a RAT into production.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.




