

A trio of newly discovered exploit frameworks has been detailed by Google’s Threat Analysis Group (TAG) in a recent publication. In the last few years, these exploit frameworks have been exploited as zero-day vulnerabilities by exploiting:
There were three separate bugs submitted to Google’s Chrome bug tracking system by someone random user while analyzing the report TAG team found frameworks for exploit kits.
TAGS is a group of Google security experts dedicated to the protection of Google users against attacks that are controlled by governments.
But, additionally, it also observes a large number of companies and organizations that provide governments with surveillance tools for the purpose of spying on the following entities:-
- Protesters
- Journalists
- Political opponents
Exploit Frameworks Used
A complete framework and source code were provided for each of the three bugs. While here we have mentioned the frameworks below:-
- Heliconia Noise: A web framework for deploying an exploit for a Chrome renderer bug followed by a sandbox escape
- Heliconia Soft: A web framework that deploys a PDF containing a Windows Defender exploit
- Files: A set of Firefox exploits for Linux and Windows.
How Frameworks are Used
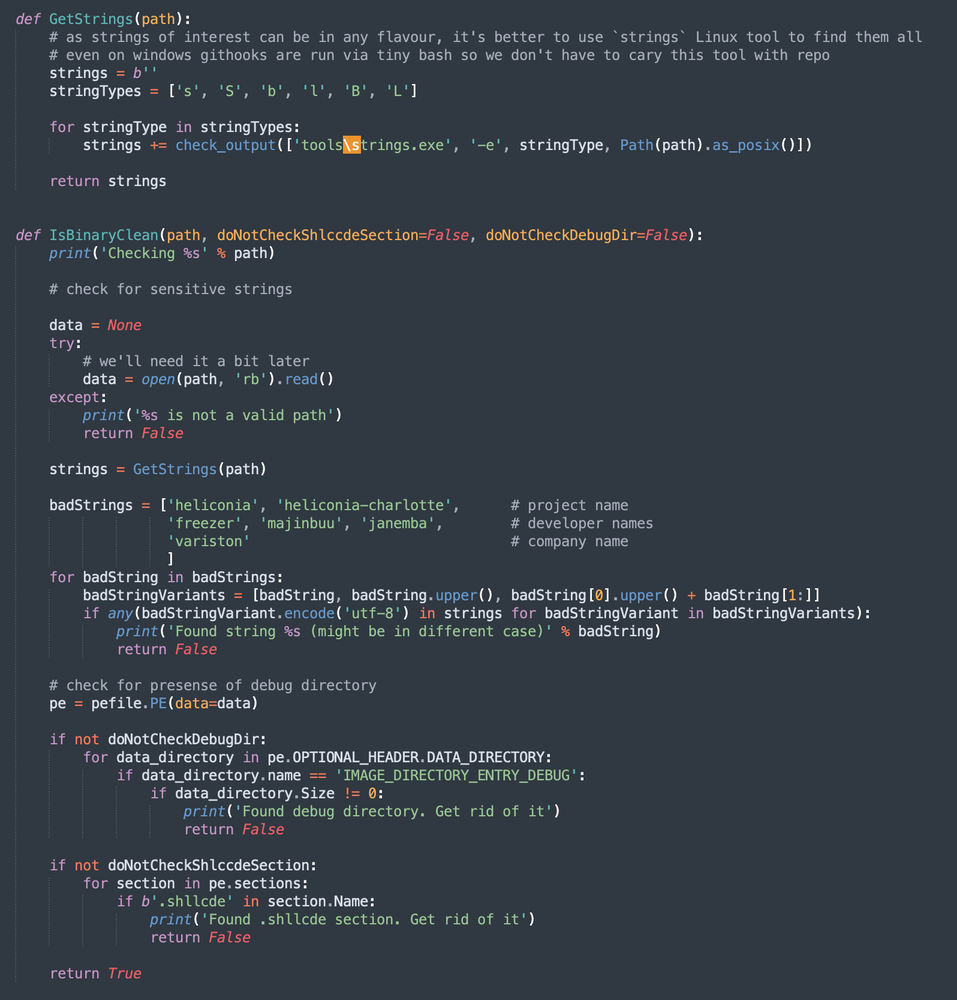
Google’s researchers discovered that as part of its investigation into the vulnerabilities and frameworks, a script was being executed against any sensitive information in order to remove it.
In addition to that, it also referenced Variston, an IT security firm in Spain that specializes in data security.
However, the references suggest that Variston may have developed the frameworks for the exploits and due to this TAG analysts also believe the same.
There is a great deal of complexity and maturity involved in all of these frameworks. These frameworks are mature enough that with no difficulty they can deliver exploits to target machines, and these abilities make TAG’s beliefs stronger.
A simple agent named ‘agent_simple’ was deployed on the compromised device as a result of the exploits for:-
- Heliconia Noise
- Heliconia Soft
Presently, there are no indications that the targeted security vulnerabilities are being exploited actively.
While it is important to note that these vulnerabilities have already been addressed in the years 2021 and early 2022 by:
- Mozilla
- Microsoft
It appears, that Google TAG suspects these flaws are being exploited in wild as zero-day exploits. For the Windows version of Firefox, there is also a sandbox escape exploit available.
Heliconia is considered one of the many commercial surveillance tools that Google’s TAG researchers described as an example of how dangerous these tools can be for many types of potential targets in many parts of the world.
A growing spyware industry poses a risk to Internet users and compromises the security of the Internet. While law enforcement agencies often use surveillance technology in detrimental ways against a wide range of groups around the world for their espionage goals.
These activities are successfully executed by these agencies due to the legality of surveillance technology under national or international laws.
Penetration Testing As a Service – Download Red Team & Blue Team Workspace






 in a recent publication. In the last few years, these exploit frameworks have been exploited as zero-day vulnerabilities by exploiting: )