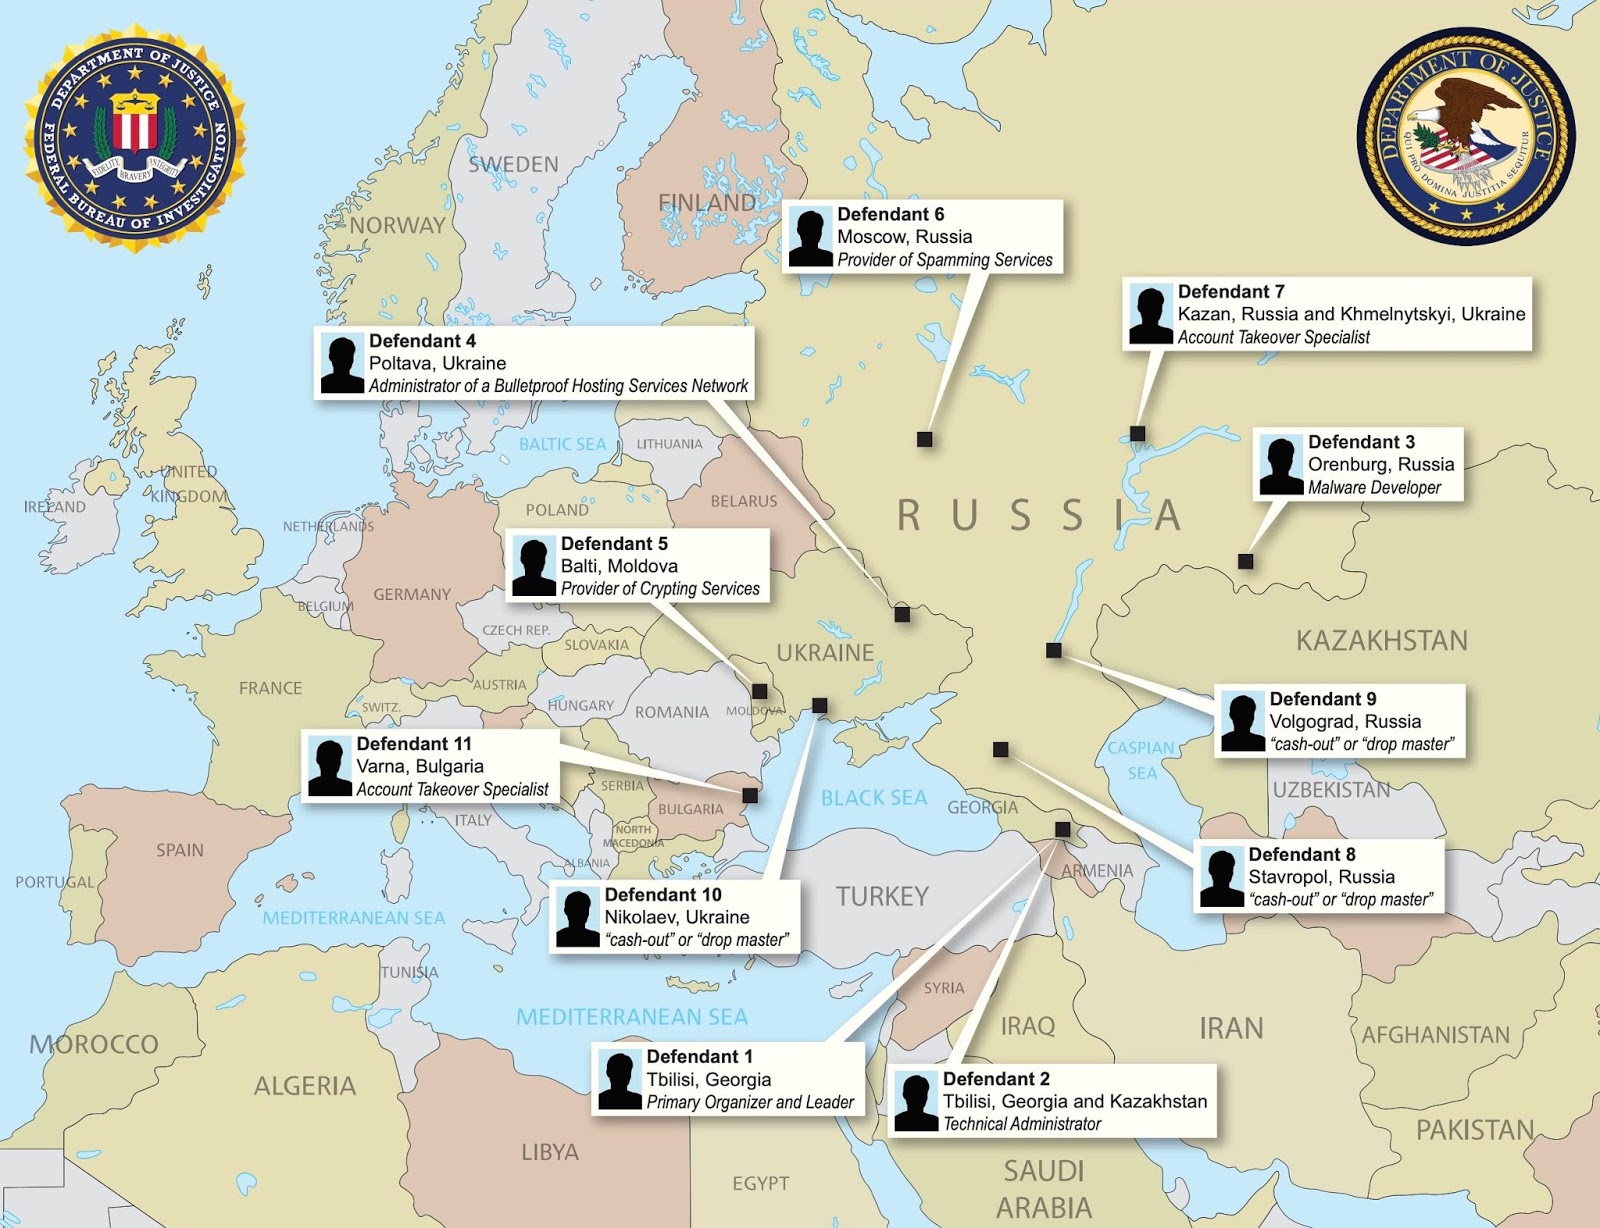
International law enforcement operation brings down a globally operated and well-organized cybercrime network behind GozNym banking malware responsible for stealing $100 million from more than 41,000 victims.
The GozNym banking malware primarily targeted financial institutions; it includes a banking trojan and trojan downloader, which also has the function of ransomware.
GozNym distributed through phishing emails, designed to have appeared from legitimate sources and includes a malicious link or attachment.
The United States charges ten members of the GozNym criminal network in a conspiracy to infect victims computer with malware to capture login credentials, using stolen credentials to gain unauthorized access and for stealing money from victims’ bank accounts.
“The International operation was highlighted by the unprecedented initiation of criminal prosecutions against members of the network in four different countries as a result of cooperation between the United States, Georgia, Ukraine, Moldova, Germany, Bulgaria, Europol, and Eurojust,” reads the press release.
GozNym cybercrime group also emphasize “cybercrime as a service,” along with services such as bulletproof hosters, money mules networks, crypters, spammers, coders, organizers, and technical support.
According to the Indictment, the defendants reside in Russia, Georgia, Ukraine, Moldova, and Bulgaria. The operation was an unprecedented international effort to share evidence and initiate criminal prosecutions against members of the same criminal network in multiple countries.
The leader of the GozNym malware network who controlled 41 000 victim computers arrested along with his technical assistant is being prosecuted in Georgia.
For hosting they used Bulletproof hosting services, provided by Avalanche, the administrator of the service is now facing prosecution in Ukraine.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity updates also you can take the Best Cybersecurity courses online to keep your self-updated.
Two Hackers of Bayrob Malware Gang Convicted for Infecting more than 400,000 Computers Worldwide
Attackers abused compromised ConnectWise Cloud Backup credentials to access Microsoft 365 customer environments, prompting ConnectWise…
Anthropic says an internal Claude research model reconstructed how the National Security Agency generated seeds…
Two WordPress Core vulnerabilities can be chained to execute remote code without authentication, according to…
A newly disclosed OpenBSD kernel exploitation chain combines a shared memory accounting flaw with a…
GhostAction attackers have expanded their GitHub credential theft campaign with a second stage that disguises…
Indian authorities have warned that SideCopy hackers are targeting Indian organizations, including academic institutions, with…