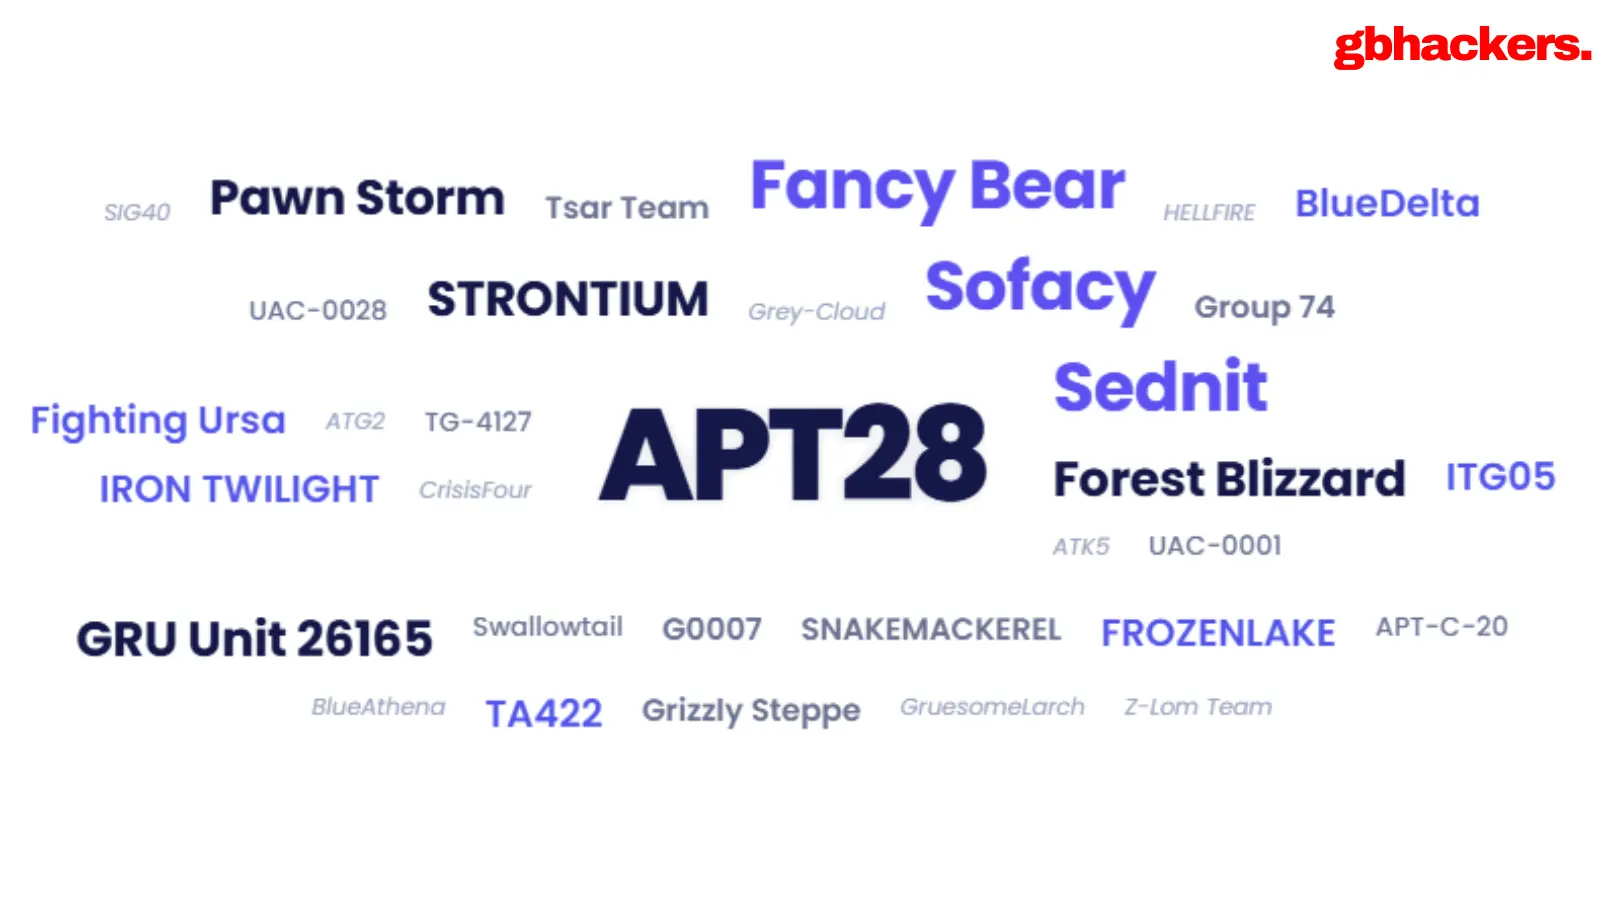

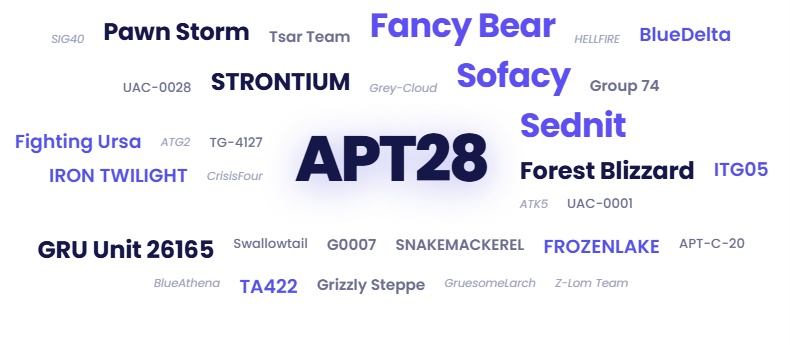
A notable operational pivot by the GRU-linked intrusion set APT28 (aka Fancy Bear, Sofacy, Forest Blizzard, Pawn Storm) that combines the MooBot botnet and compromised EdgeRouters to enable resilient cyber operations.
This shift amplifies APT28’s long-standing focus on NATO, Ukrainian and critical-infrastructure targets by moving key capabilities from traditional cloud VPS and commodity hosting into the network edge, where compromised consumer and small-office routers provide stealthy, geographically distributed platforms for credential harvesting, proxying and hosting malicious payloads.
Technical tradecraft observed across 2022–2026 shows APT28 repurposing the MooBot family originally a criminal botnet infecting Ubiquiti EdgeRouter devices as an operational substrate.
Infected EdgeRouters function as persistent footholds and service nodes: they relay harvested Net-NTLMv2 hashes captured via a weaponized Outlook zero-click chain.
Proxy authentication flows for mailbox takeover, host credential-phishing landing pages on residential IPs to evade reputation filters, and stage lightweight Python tooling to scrape webmail or perform second-factor bypass.
Sekoia’s Threat Detection & Research (TDR) team has been tracking APT28 for several years.The intrusion set, also known as Fancy Bear, Forest Blizzard, Sofacy, Pawn Storm or Sednit and publicly attributed to the GRU’s Unit 26165.
The FBI-led disruption (Operation Dying Ember) and subsequent advisories revealed hundreds of compromised EdgeRouters; however, follow-up telemetry from private vendors indicates many residual callbacks and civilian devices remained exploited, underscoring the difficulty of fully eradicating edge-based infrastructures.
Concurrently, APT28 expanded the edge concept with the FrostArmada campaign targeting MikroTik and TP-Link devices. The adversary rewrites DHCP/DNS settings on routers to point clients to attacker-controlled DNS resolvers, enabling an adversary-in-the-middle (AitM) for Microsoft 365 and similar services.
GRU-Linked APT28 Uses MooBot Botnet
This DNS hijacking funnels authentication traffic through APT28 nodes where OAuth tokens and authentication metadata may be harvested, facilitating long-lived access without deploying heavy implants on victim networks.
Lumen Black Lotus Labs and Microsoft telemetry in 2026 documented tens of thousands of unique IPs and hundreds of affected organizations, illustrating the scale achievable when adversaries weaponize widely deployed CPE devices.
This edge-centric posture provides several operational advantages. First, residential and small-business IPs blend with legitimate traffic, complicating IP-blocking and abuse-based mitigation.
Second, on-router tooling reduces forensic footprints on target hosts while enabling interception of authentication flows and lightweight credential automation (for example, scripts that read and act on mailbox notifications or IMAP configuration).
Third, the distributed topology increases resiliency against takedowns: even after law-enforcement disruption of parts of MooBot, actor-managed VPS, additional botnets, and misconfigured consumer devices continued to support operations.
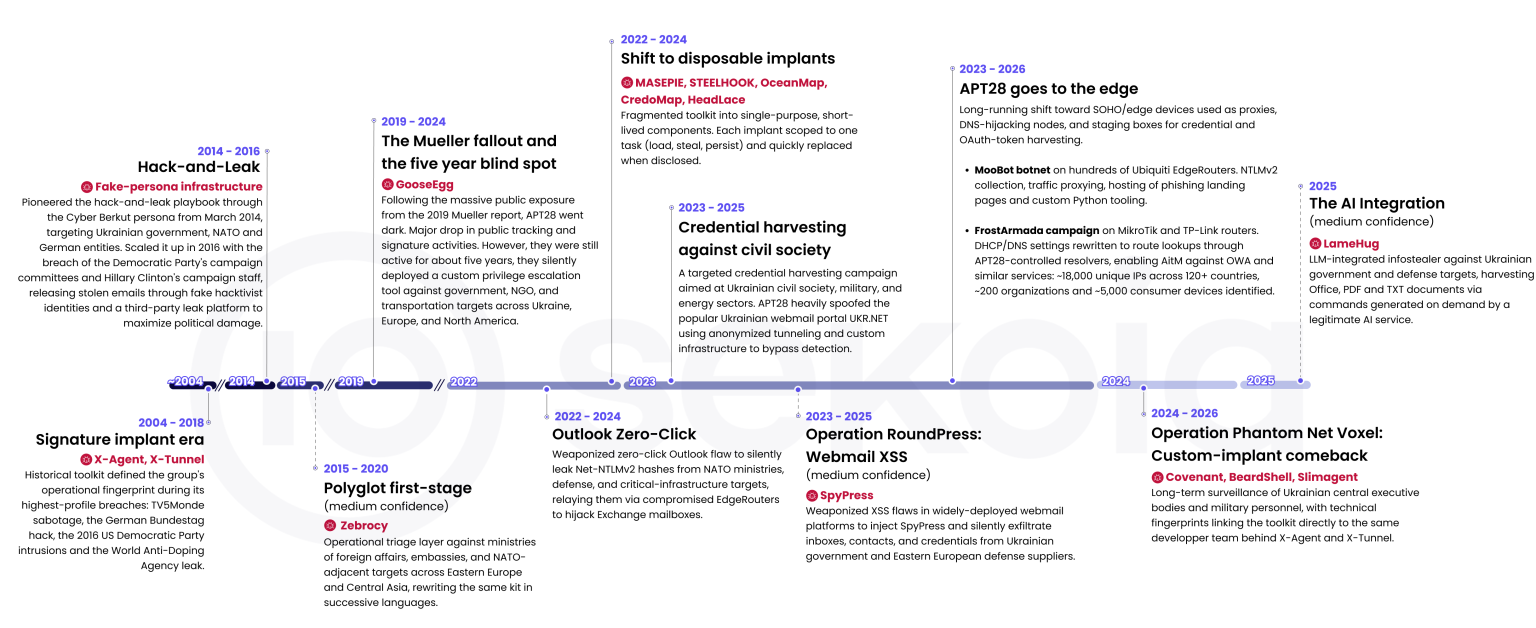
The technical lineage ties this edge activity back to APT28’s historical tradecraft. The group’s zero-click Outlook exploitation to collect Net-NTLMv2 hashes and later relay them via compromised routers mirrors earlier tactics of leveraging intermediary infrastructure (X-Tunnel) for exfiltration and pivoting.
More recent campaigns Operation Phantom Net Voxel, RoundPress, and the LameHug LLM-assisted infostealer demonstrate APT28’s dual approach of reviving robust in-house implants while operationalizing ephemeral, single-purpose components.
The EdgeRouter and FrostArmada techniques augment these capabilities by providing scalable interception and proxy layers that complement spear-phishing, server-side webmail XSS intrusions, and bespoke backdoors such as BeardShell and Slimagent.
Defensive implications are clear: network owners must secure CPE, apply vendor firmware updates, enforce strong router credentials, disable remote management where unnecessary, and monitor DNS and DHCP configuration anomalies.
Enterprise defenders should monitor for anomalous outbound SMB/NTLM authentications, unexpected DNS resolver changes, and residential IPs serving credential collection.
Coordination between vendors, national CERTs, and law enforcement remains critical past cooperation (including FBI, NSA, Microsoft and multiple CERT advisories) produced takedowns and advisories but did not fully eliminate the persistent risk.
For in-depth technical context and indicators, see Sekoia’s TDR reporting on Operation Phantom Net Voxel, the joint FBI/NSA advisory on compromised routers, Lumen Black Lotus Labs’ FrostArmada analysis.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


 that combines the MooBot botnet and compromised EdgeRouters.)