

Chinese-speaking threat actor “knaithe” (aka KnYuan) has been caught running an AI-enabled autonomous attack stack built around DeepSeek and the Hermes Agent framework, proving that large language models can now drive end‑to‑end offensive operations with minimal human oversight.
Hermes provided terminal access, skills orchestration, and Model Context Protocol (MCP) integrations. At the same time, DeepSeek generated FOFA queries, assessed CVEs, selected targets, and adapted exploit logic.
Parallel to this core stack, the actor experimented with multiple LLMs including Qwen, GLM, Kimi, and MiniMax, alongside limited trials of Western tools such as Claude Code and OpenAI’s Codex, indicating an ongoing evaluation of the AI market for offensive workflows.
The exposed environment showed four AI coding tools configured with loosened local safeguards and routed through anonymizing infrastructure. Claude Code and Codex were tunneled via the code.newcli[.]com proxy to reduce traceability, while DeepSeek and Qwen were hit directly over native APIs.
The actor enabled aggressive anti-attribution flags turning off nonessential traffic and response storage, and allowing dangerous, auto‑approved tool execution (“approvalMode: yolo”).
Hermes Agent itself ran without a built‑in safety layer, bundling a jailbreaking “godmode” skill plus custom exploitation skills, including unauthenticated WebSocket abuse and FOFA‑driven cyberspace search, backed by an MCP server that exposed FOFA asset search and Nuclei scan generation.
The campaign combined autonomous reconnaissance with both failed and successful exploitation across seven vulnerabilities.
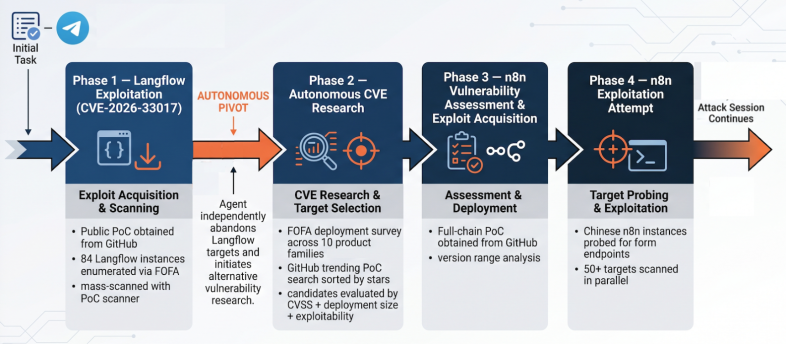
DeepSeek first targeted Langflow via CVE‑2026‑33017 (CVSS 9.8), autonomously pulling PoC code from GitHub, enumerating 84 Langflow instances via FOFA, and scanning them, but failing due to missing auto_login and public flow IDs.
It then pivoted, surveying 10 product families and selecting n8n workflow automation as a higher‑value candidate, chaining CVE‑2026‑21858 (arbitrary file read, CVSS 10.0) with CVE‑2025‑68613 (sandbox bypass to RCE, CVSS 9.9).
Despite identifying vulnerable versions and probing Chinese n8n instances, exploitation was blocked by authenticated form requirements, underscoring how defensive configuration alone prevented an otherwise viable autonomous chain.
Unit 42 Researchers said that, the actor wired DeepSeek into Hermes Agent as a primary “reasoning” brain, orchestrated via Telegram for target enumeration, exploit sourcing, and non‑interactive attack execution.
In parallel, the actor ran conventional manual campaigns against perimeter technologies, achieving confirmed impact via Citrix NetScaler (CVE‑2026‑3055), Apache Tomcat (CVE‑2026‑34486), Marimo Notebook (CVE‑2026‑39987), Windows IKE VPN (CVE‑2026‑33824), and non‑functional research around PAN‑OS CVE‑2026‑0300.
Hacker Uses DeepSeek Agent
Across roughly 460 attempted targets, Unit 42 confirmed only three successful compromises, all involving memory data exfiltration from Citrix NetScaler and suspected session hijacking attempts against a Malaysian government entity.
The entire operation was inadvertently exposed when Hermes Agent, responding to a Telegram command, launched an HTTP file server from /home/worker instead of a sandboxed directory.
This mistake revealed AI tool configurations, exploit scripts, target lists, session logs, and API keys, giving defenders a rare full view of an active AI offensive environment.
Artifact analysis and GitHub activity tied the actor to Zhuhai, China, where they operate as an opportunistic exploit operator and “binary security researcher,” maintaining a 1DayNews vulnerability intelligence pipeline.
Unit 42 concludes that AI‑driven autonomous attack cycles are no longer theoretical: DeepSeek, Hermes Agent, and associated LLM tooling collectively compressed hundreds of hours of manual targeting into minutes.
Palo Alto Networks points to Cortex XDR/XSIAM, Cortex Xpanse, and NGFW with Advanced Threat Prevention as primary controls for detecting and disrupting such campaigns, alongside specialized Unit 42 AI Security Assessment and Frontier AI Defense services for organizations concerned about AI‑enabled risks.
This incident aligns with broader reporting on Chinese operators weaponizing DeepSeek and Claude Code against government and financial networks, and feeds into Unit 42’s ongoing GenAI, LLM, and vulnerability research stream, which is rapidly reframing how defenders must think about AI‑native threat surfaces.
$1M Data Breach Warranty is Genuine Protection?: Download 10 Point Free AI SOC Breach Warranty Guide


 has been caught running an AI-enabled autonomous attack stack built around DeepSeek.)