

Multiple fraudulent Microsoft Partner Network accounts were discovered to have created harmful OAuth applications, causing breaches in organizations’ cloud environments and leading to the theft of emails. As a result, Microsoft has taken action and disabled these verified accounts.
Microsoft and Proofpoint announced a joint statement revealing that some malicious actors had managed to impersonate legitimate companies and gain verification as those companies in the MCPP.
Cybercriminals utilized these accounts to establish legitimate OAuth applications in Azure Active Directory, with the aim of tricking corporate employees in the UK and Ireland through consent phishing attacks.
Technical Analysis
The malicious OAuth applications had malicious intent, they were specifically designed to steal sensitive information from unsuspecting customers. In this case, the target was the customers’ email addresses.
These email addresses were likely collected and used for phishing or spamming purposes, or could even be sold on the dark web to other malicious actors.
The app’s excessive permissions might have opened up the possibility for unauthorized access to calendars, meeting information, and modifications to user permissions.
Cybercriminals often exploit this information for the following illicit activities:-
- Cyberespionage
- BEC attacks
- Gain deeper access to internal networks
On December 15, 2022, Proofpoint brought to light a malicious campaign, prompting Microsoft to swiftly shut down all the deceptive accounts and OAuth applications involved.
Following the discovery, the company promptly notified impacted customers through email, stating that the malicious actors leveraged the compromised consent to steal data from email accounts.
Microsoft detected that to enhance credibility, malicious actors have utilized several tactics to deceive individuals by pretending to be reputable organizations.
The presence of malicious apps registered by the threat actors with “publisher verified” status implies that through the MPN process, they successfully passed the authentication.
Proofpoint was informed by Microsoft that altering the publisher name linked to their MPN account necessitates going through the re-verification process.
Having obtained a verified publisher ID, malicious actors incorporated links in each application that direct to the site of the organization being impersonated, under the guise of “terms of service” and “policy statement”.
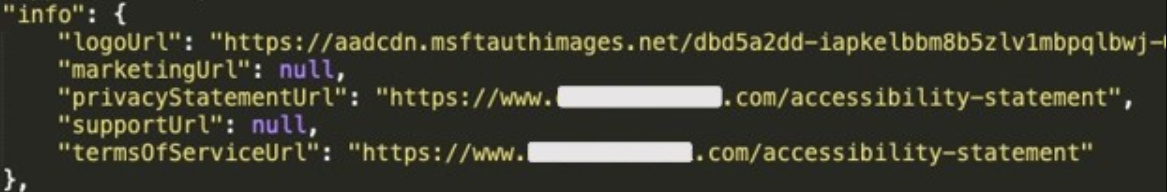
Impersonation of Popular Apps
Cybercriminals, posing as legitimate verified publishers, are exploiting the popularity of apps like Single-Sign-On (SSO) to deceive victims by utilizing:-
- Duplicated app icons
- Duplicated app names
- Reply-to URLs
The application consent screen is connected to personalized “.html” and “.htm” files which are used to spread the request for authorization.
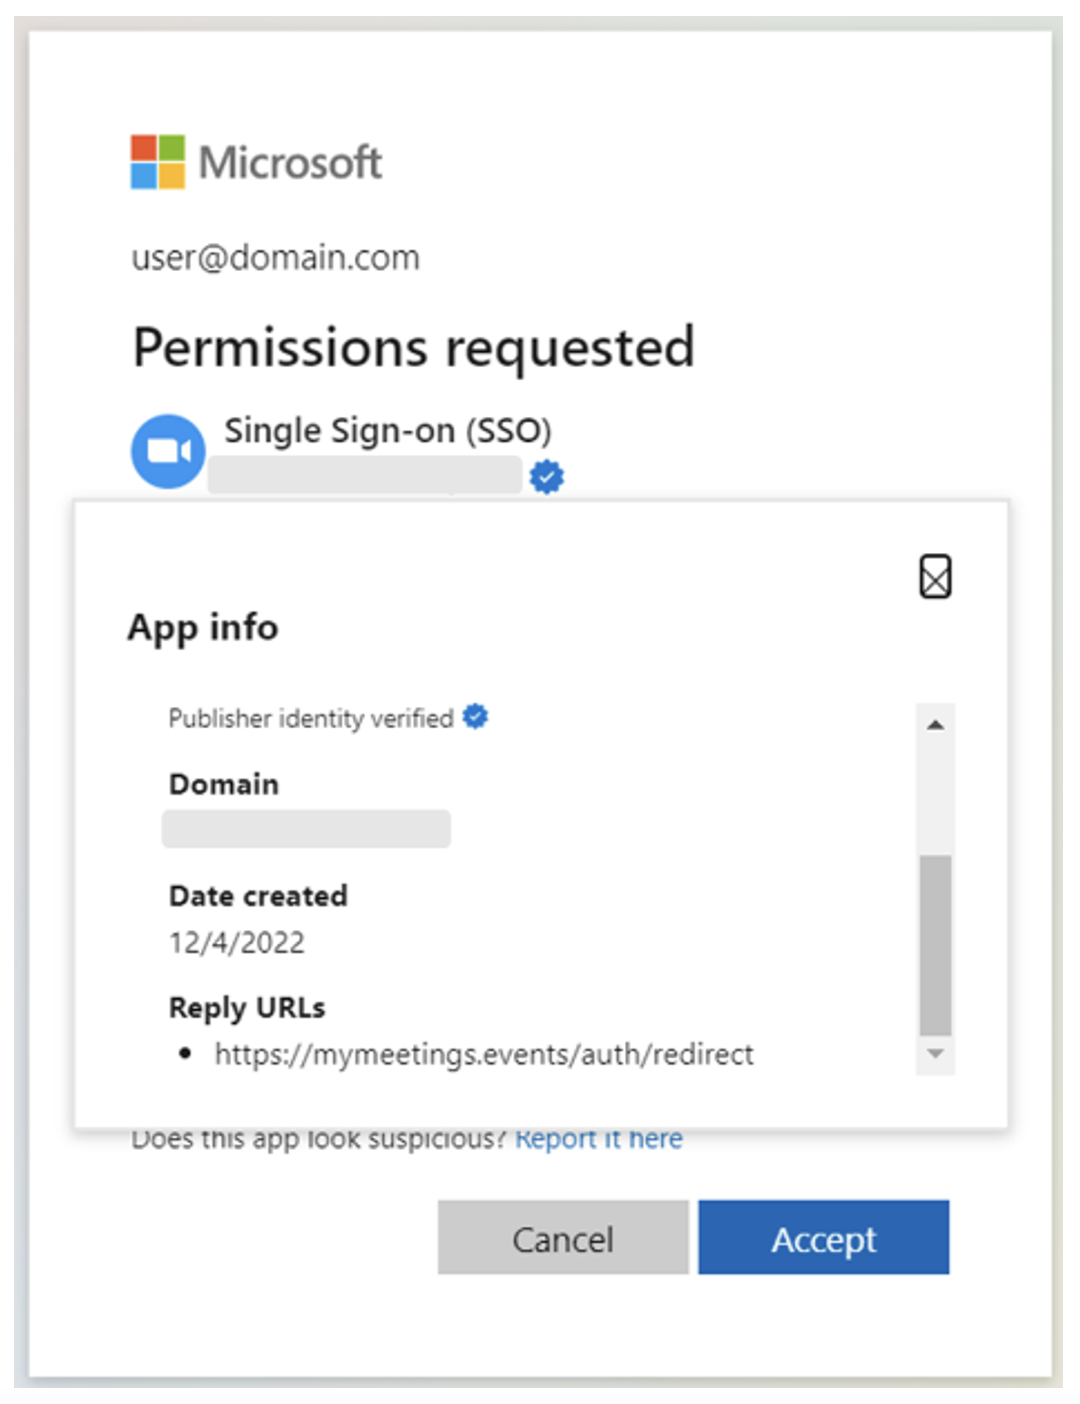
A blue check in the Azure Active Directory (Azure AD) consent prompt serves as an indicator of trustworthiness for OAuth applications created by a verified partner.
Of the three applications, two were labeled “Single Sign On (SSO)” and the third was referred to as “Meeting.” All three requested access to the following permissions:-
- User.Read
- offline_access
- profile
- openid
- Mail.Read
- MailboxSettings.Read
- Calendars.read
- Onlinemeetings.read
- Mail.send
Sadly, multiple organizations have suffered from attacks, with Proofpoint discovering evidence of affected users. The malicious campaign took place between December 6, 2022 and December 27, 2022, when it was finally brought to a halt by Microsoft.
During this period, the attackers used various malicious applications to carry out their attacks, but Microsoft was able to detect and disable all of them, effectively stopping the campaign.
The use of fake OAuth applications to target Microsoft’s cloud services is not a new phenomenon. In fact, this has been a recurring issue, with malicious actors frequently exploiting the trust associated with these apps to gain access to sensitive information and carry out their attacks.
This highlights the importance of being cautious when granting access to third-party apps and verifying their authenticity, as well as the need for Microsoft to continually improve its security measures to protect its users and prevent these types of attacks from happening.
Network Security Checklist – Download Free E-Book


