

Across a wide variety of organizations around the world, container adoption has shown signs of becoming mainstream over the last few years.
Since container orchestration projects like Kubernetes and other tools available in the cloud have been developed in recent years, a wave of transformations has occurred in how organizations operate.
The application of microservices-based architectures rather than monolithic architectures is a feature that has become increasingly popular in the development of distributed systems.
As a consequence of these changes, however, there has also been an increase in the attack surface, which is a problem. Specifically through security misconfigurations and vulnerabilities introduced during deployment that lead to security threats and compromises.
Because of this, hackers are launching attacks on Linux environments by exploiting native Linux tools.
Attacks Using Legitimate Tools
There is typically a standard exploitation chain that is followed by an attacker when attacking a Linux-based system. The first step in gaining access to an environment is for an attacker to exploit a vulnerability.
According to the Trend Micro report, in order to gain access to further areas of the compromised system, an attacker may follow different paths:-
- The current environment of the organization is described by enumerating its context.
- Data exfiltration from an environment that contains sensitive information.
- Disabling the application and causing a denial-of-service attack.
- Downloading miners and mining cryptocurrency.
- Experimenting with other techniques, such as:-
- Privilege Escalation
- Lateral Movement
- Persistence
- Credential Access
Threat actors use various tools that come bundled with Linux distributions to accomplish this goal. Here below we have mentioned the tools that are abused:-
- curl
- wget
- chmod
- chattr
- ssh
- base64
- chroot
- crontab
- ps
- pkill
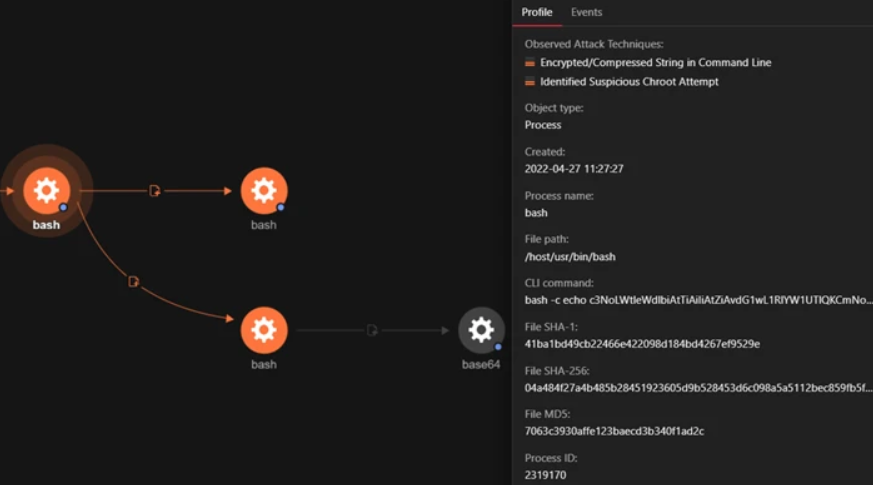
Decoding strings encoded in base64 format is done with the base64 tool, which is a Linux utility. In order to avoid detection, attackers often use base64 encoding to obfuscate their payloads and commands.
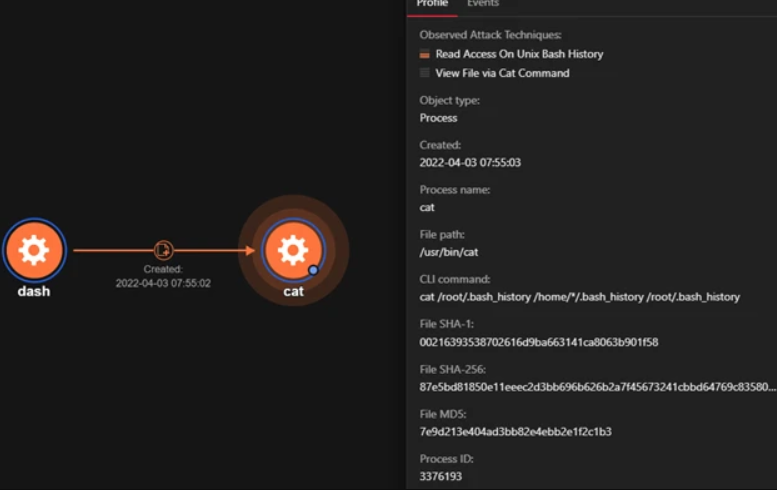
Users’ bash shell commands are logged in their .bash history file, which is located in their home directory. An attacker chose to make use of the Visual One workbench, chroot, and base64 utilities to execute malicious code.
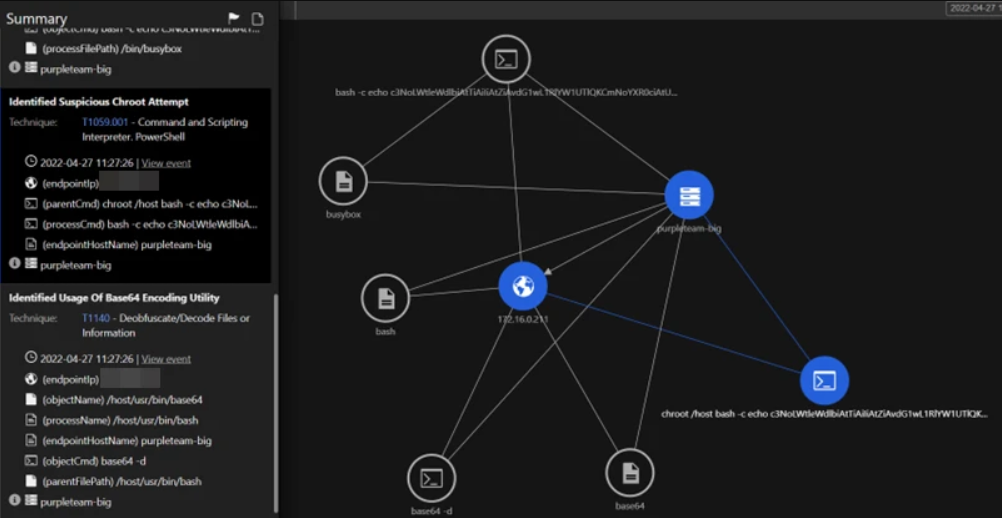
The chroot tool is used to change the root to the directory supplied (in this case, /host), where the underlying host’s file system is mounted within the container.
Recommendations
There is no doubt that attackers are using tools and utilities that are inherent to an OS, so defenders will have to think about what controls they want to have in place during the different phases of the attack so that they can stay ahead of the attackers.
Here below we have mentioned all the recommendations to mitigate such threats:-
- Make sure to use distroless images.
- Cloud One Workload Security – Application Control.
- Make sure that unrecognized software is blocked until explicit permission has been given.
- Until explicitly blocked, allow unrecognized software to run on your system.
Download Free SWG – Secure Web Filtering – E-book







