

The cybersecurity research team at FireEye has recently detected back to back three vulnerability in Sonicwall’s email security software.
In a regular analysis, the experts have again detected that a threat group, UNC2447, is financially very motivated is continuously exploiting SonicWall VPN zero-day (CVE-2021-20016) vulnerability.
According to the report from FireEye, this vulnerability is prior to a currently available patch and is continuously deploying the sophisticated ransomware.
The experts, after detecting the ransomware they named it as FiveHands and pronounced that this is quite similar to the malware that is designated as HelloKitty.
Surreptitious HelloKitty
However, the attack in which the threat actors have implemented FiveHands was initially detected in October 2020. As we said above that FiveHands is very similar to the HelloKitty malware.
HelloKitty was discovered as it has attacked video game development studio CD Projekt Red, it has encrypted the game system.
Once the encryption is done, the threat actors have stolen the source code for Cyberpunk 2077, Gwent, Witcher 3, and not only this, but they also attacked an unreleased version of Witcher 3.
The attack rate of HelloKitty decreased as the use of the FiveHands attack increased. Rather than similar feature and functionality, both of them were also linked by Mandiant.
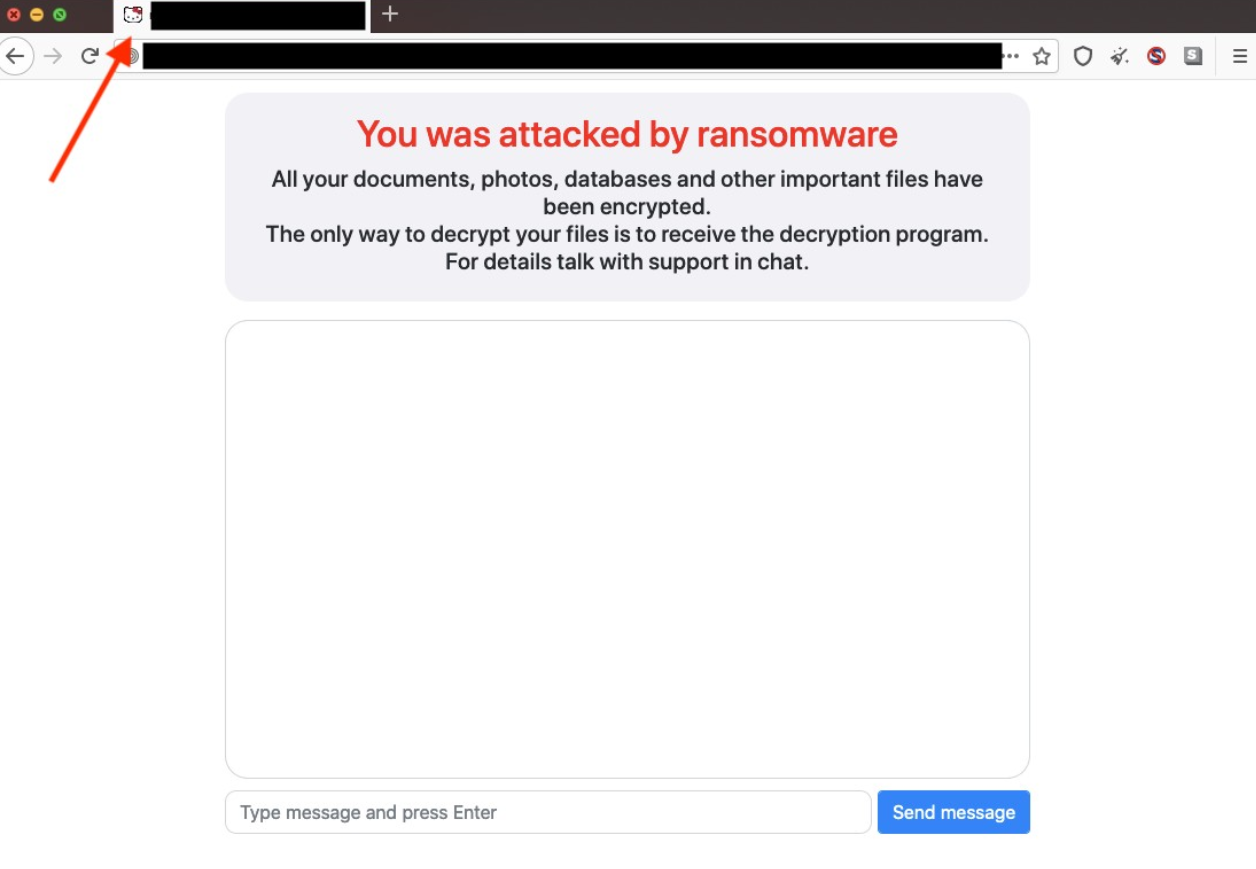
The specialists came to know about the link after a month of observing the FiveHands ransomware Tor chat using a HelloKitty favicon.
UNC2447 affiliates also deployed “Ragnar Locker”
The threat actors keep an eye upon their victims through the FiveHands ransomware; after that, the hackers violently applied pressure upon the victims with media attention threats.
The threat actors also offer victim data for sale on hacker forums, and according to the cybersecurity researchers, the UNC2447 associates have observed many sources so that they can easily implement Ragnar Locker ransomware activity.
However, the similarities of HelloKitty and FiveHands, are quite visible, but ransomware may be utilized by different groups via underground affiliate programs.
Unlike, HelloKitty, FiveHands has improved ad worked on its predecessors by utilizing a new, memory-only dropper. Later, the threat actors have applied encryption to a larger array of file types.
Moreover, the zero-day has again being exploited by some other group named UNC2682 to backdoor systems. But, still, this group has used BEHINDER web shells to move safely through the victims’ networks and quickly gain access to the emails and all other files.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity, and hacking news updates.







