

A growing cyber threat involving Dropbox has emerged, and it’s raising concerns across the cybersecurity landscape.
In the initial two weeks of September, a staggering 5,440 of these attacks were detected, highlighting the alarming scale of this threat.
Utilizing Dropbox for Deceptive Attacks
Hackers are leveraging Dropbox to create fake login pages, ultimately leading unsuspecting victims to credential-harvesting websites.
This tactic represents a new iteration of Business Email Compromise (BEC) attacks, which we’ll refer to as BEC 3.0.
BEC 3.0 attacks involve the use of legitimate platforms like Dropbox to send and host phishing materials.
The legitimacy of these platforms makes it incredibly challenging for email security services to detect and for end-users to recognize the threats.
Expanding Attack Surface
These attacks are on the rise, and hackers are employing various productivity sites, including Google, Dropbox, QuickBooks, PayPal, and more, as their battlegrounds.
This innovation in phishing tactics has proven highly effective and is rapidly gaining popularity among cybercriminals.
Attack Overview
In this particular attack, hackers use Dropbox documents to host websites designed for credential harvesting. Here are the key details:
Vector: Email
Type: BEC 3.0
mTechniques: Social Engineering, Credential Harvesting
mTarget: Any end-user
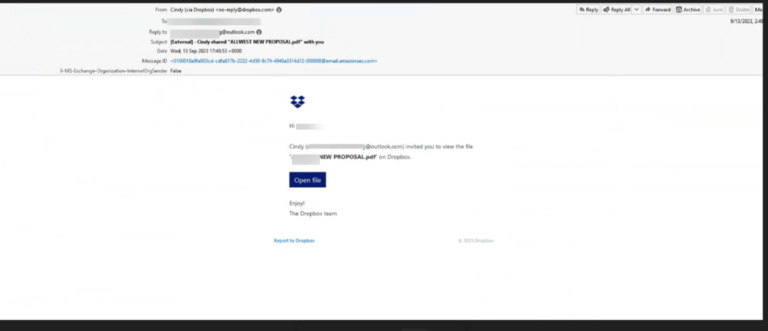
The attack begins with an email seemingly from Dropbox, informing the recipient that there’s a document to view. This email appears entirely standard and would not immediately raise suspicion.
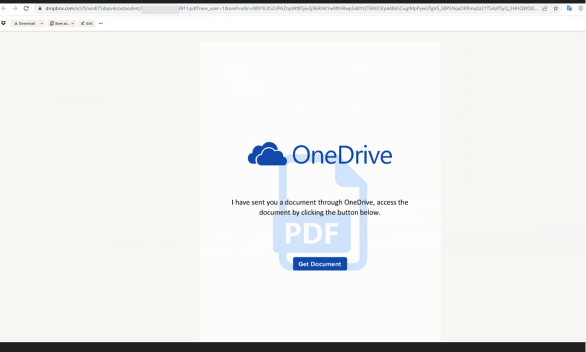
Upon clicking the email, the user is directed to a Dropbox page. Although the content mimics a OneDrive login page, the URL clearly indicates it’s hosted on Dropbox.
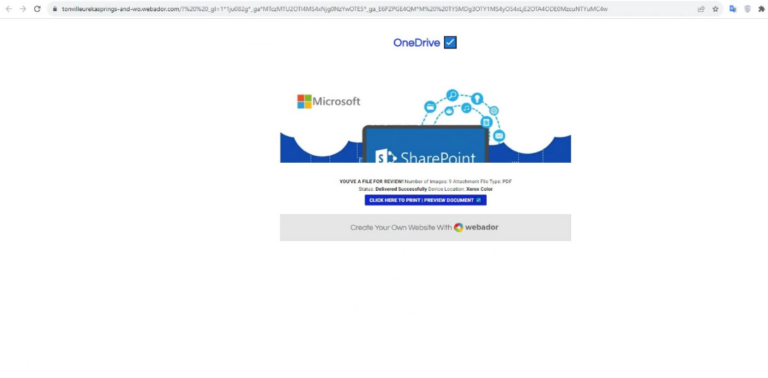
Clicking “Get Document” redirects the user to the final page, which is the credential harvesting page. This page, hosted outside of Dropbox, is where threat actors aim to steal user credentials.
The evolution of Business Email Compromise attacks is notable. It began with simple “gift card” scams and impersonation of domains and partners.
However, it has now reached BEC 3.0, where attacks are executed through legitimate services, making them exceptionally challenging to detect.
These attacks are immensely difficult to stop and identify, both for security services and end-users.
Traditional indicators of phishing, like unusual language or spoofed domains, no longer apply when the attacks originate from legitimate services.
Education and Vigilance
To combat these threats, educating end-users is crucial. Individuals should question the authenticity of emails and consider whether they expect to receive a document from the sender. Hovering over URLs to inspect their destination can also help.
The Role of Technology
Security professionals can take the following steps to guard against these attacks:
1. Adopt AI-powered technology capable of analyzing and identifying numerous phishing indicators.
2. Implement comprehensive security solutions with document and file scanning capabilities.
3. Deploy robust URL protection systems for thorough scans and emulation of webpages to enhance security.
Check Point researchers have taken proactive steps by reaching out to Dropbox to inform them of this campaign.
Protect yourself from vulnerabilities using Patch Manager Plus to quickly patch over 850 third-party applications. Take advantage of the free trial to ensure 100% security.


