

Hackers are tricking users with fake Windows 11 installers loaded with Vidar info stealer spreading through newly registered phishing domains.
The cybersecurity analysts at Zscale security firm have detected that the malicious ISO files were included on the spoofed websites to enable the downloading and installation of the Vidar info-stealer malware on the target computers.
Throat-controlling social media channels, such as Telegram and Mastodon, are used to deploy the C2 configuration of Vidar malware.
Newly registered phishing domains
On 20 April, some of the fake domain names have been registered and here they are mentioned below:-
- ms-win11[.]com
- win11-serv[.]com
- win11install[.]com
- ms-teams-app[.]net
In addition to attacks against YouTubers, Vidar malware has been used previously by the threat actors to swindle VPN users before.
Vidar malware
Vidar malware is an infamous info stealer that can steal information from users and spy on what they do. While malware such as Vidar is primarily designed for the purpose of stealing sensitive information from its victims.
Fallout exploit kits are usually the source of distribution of Vidar. Here below we have mentioned the types of data stolen by Vidar:-
- OS information
- Online accounts credentials
- Browser history
- Financial info
- Banking data
- Cryptocurrency wallet login credentials
Distribution of Vidar info stealer
Apart from fake Windows 11 installers, the threat actors behind Vidar also spreading this malware through malicious variants of legitimate software like:-
- Adobe Photoshop
- Microsoft Teams
In order to avoid detection by security solutions, the ISO that contains the executable is unusually large in size (over 300MB).
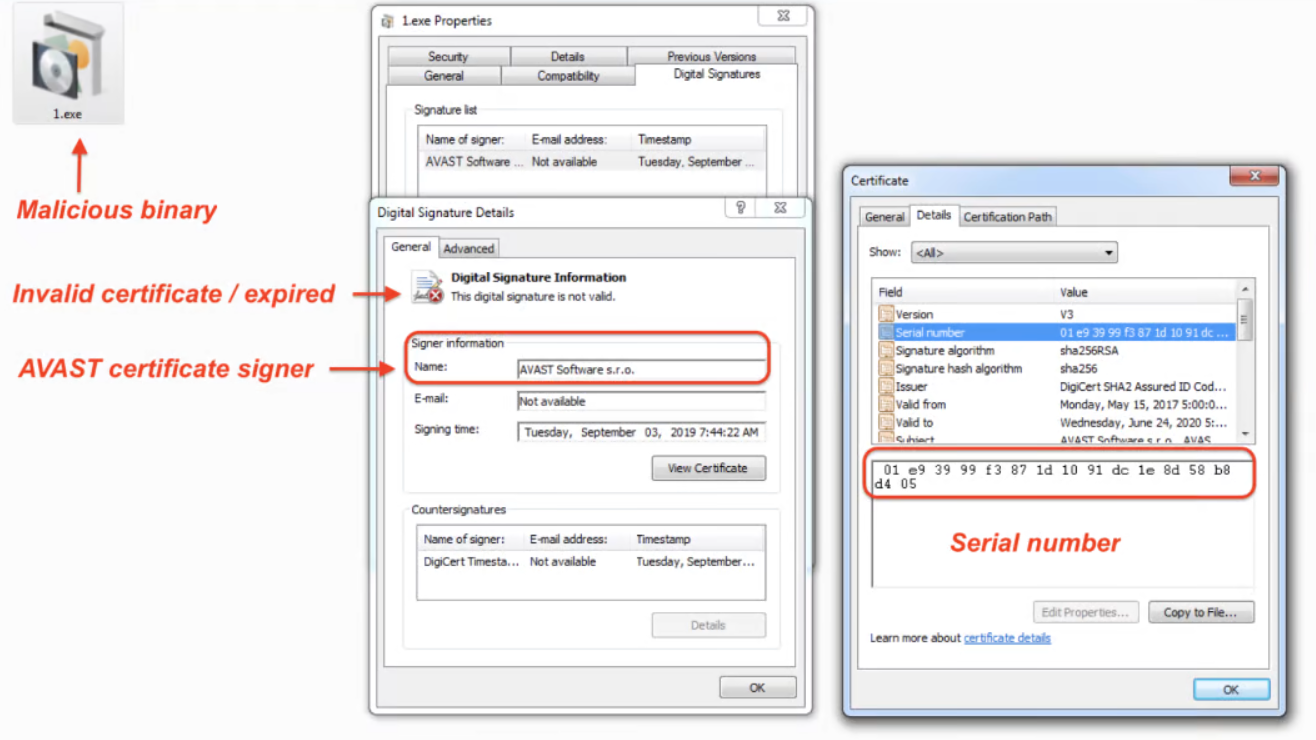
Here, Avast’s expired certificate is used by the hackers to sign the file, and it is likely that the certificate was stolen following the company’s October 2019 security breach.
To steal essential and sensitive data from the compromised systems, Vidar establishes a connection to a C2 server, and then it requests legitimate DLL files from the C2 server.
Here below we have mentioned the DLL files that are requested:-
- sqlite3.dll
- vcruntime140.dll
In addition to this abuse, the threat actor has also abused Mastodon and Telegram to store the C2 IP address in the description fields of vulnerable communities and accounts.
Recommendation
Here below we have mentioned a few recommendations offered by the security experts:-
- Do not download any file or installer file from unknown sources.
- Always be cautious before downloading any unknown attachments.
- Avoiding using crack
- Always use a robust Antivirus tool.
- Do not download any crack for the paid version.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.







