

SafetyDetectives’ cybersecurity researchers came across a dark web marketplace that claims to provide consumers with access to Telegram’s internal server for the price of $20,000.
The seller claims that the price is non-negotiable and includes uninterrupted access to Telegram servers through staff members of the company.
This indicates that the seller and a company insider have some sort of arrangement over giving access to its internal servers. The vendor is making this offer to customers all over the world.
A well-liked app and instant messaging service is Telegram. By enabling end-to-end encrypted voice, video, and chat, Telegram, which was founded by Pavel and Nikolai Durov, places a high priority on security. Telegram has over 700 million active users each month.
The Dark Web Store Selling Data
The SafetyDetectives research claims that access to the market is not possible via the surface web (or clear web).
It provides counterfeit electronics, money, drugs, illegal software, stolen databases, cracking tools, counterfeit weapons, and carding data dumps.
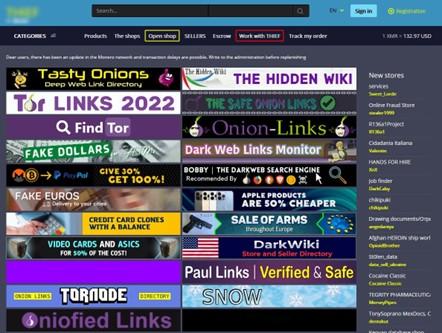
The market also provides buyers with a “buyer’s protection” option to keep money in escrow, according to SafetyDetectives researchers.
According to the seller’s ad, which was posted on November 16th, 2022, and is still active, they provide access to the Telegram server for about six months. The advertisement reads:
“Accessing telegram servers. I have access to the Telegram servers through my employees. I can get any information for you!
Expensive!
$20,000!
Do not write if you are financially unable to pay!
Hacking telegram is not possible! All information is taken from servers!
Timing 2-4 days!”
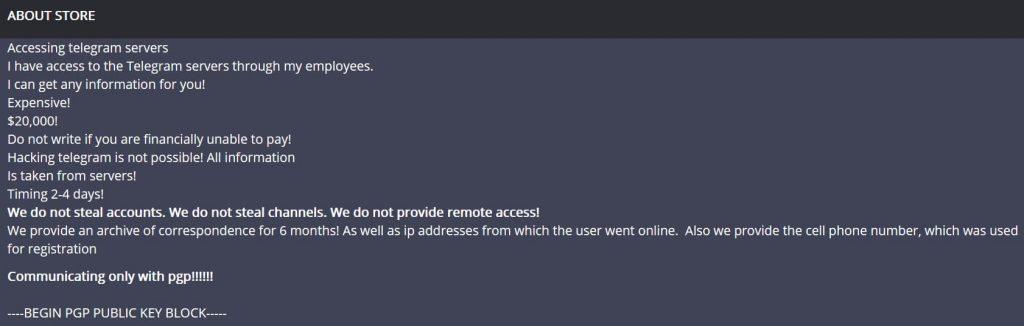
Also, the listing, according to the seller, is unrelated to channel or account theft, and remote access is not available.
With the exception of registered telephone numbers and IP addresses belonging to active customers, the vendor will provide an “archive of correspondence for six months.”
Researchers mention that it is difficult to determine whether this sales offer is legitimate. Dark Web markets are riddled with fraud and frauds.
If these assertions are true, a person with access to internal systems could steal sensitive user information and exfiltrate log data. Additionally, it could damage Telegram’s reputation as a safe chat platform.
“A potential breach of this manner would also undermine the company’s privacy USP (i.e. Telegram’s reputation as a secure messaging app)”, concludes SafetyDetectives researchers.
Network Security Checklist – Download Free E-Book







