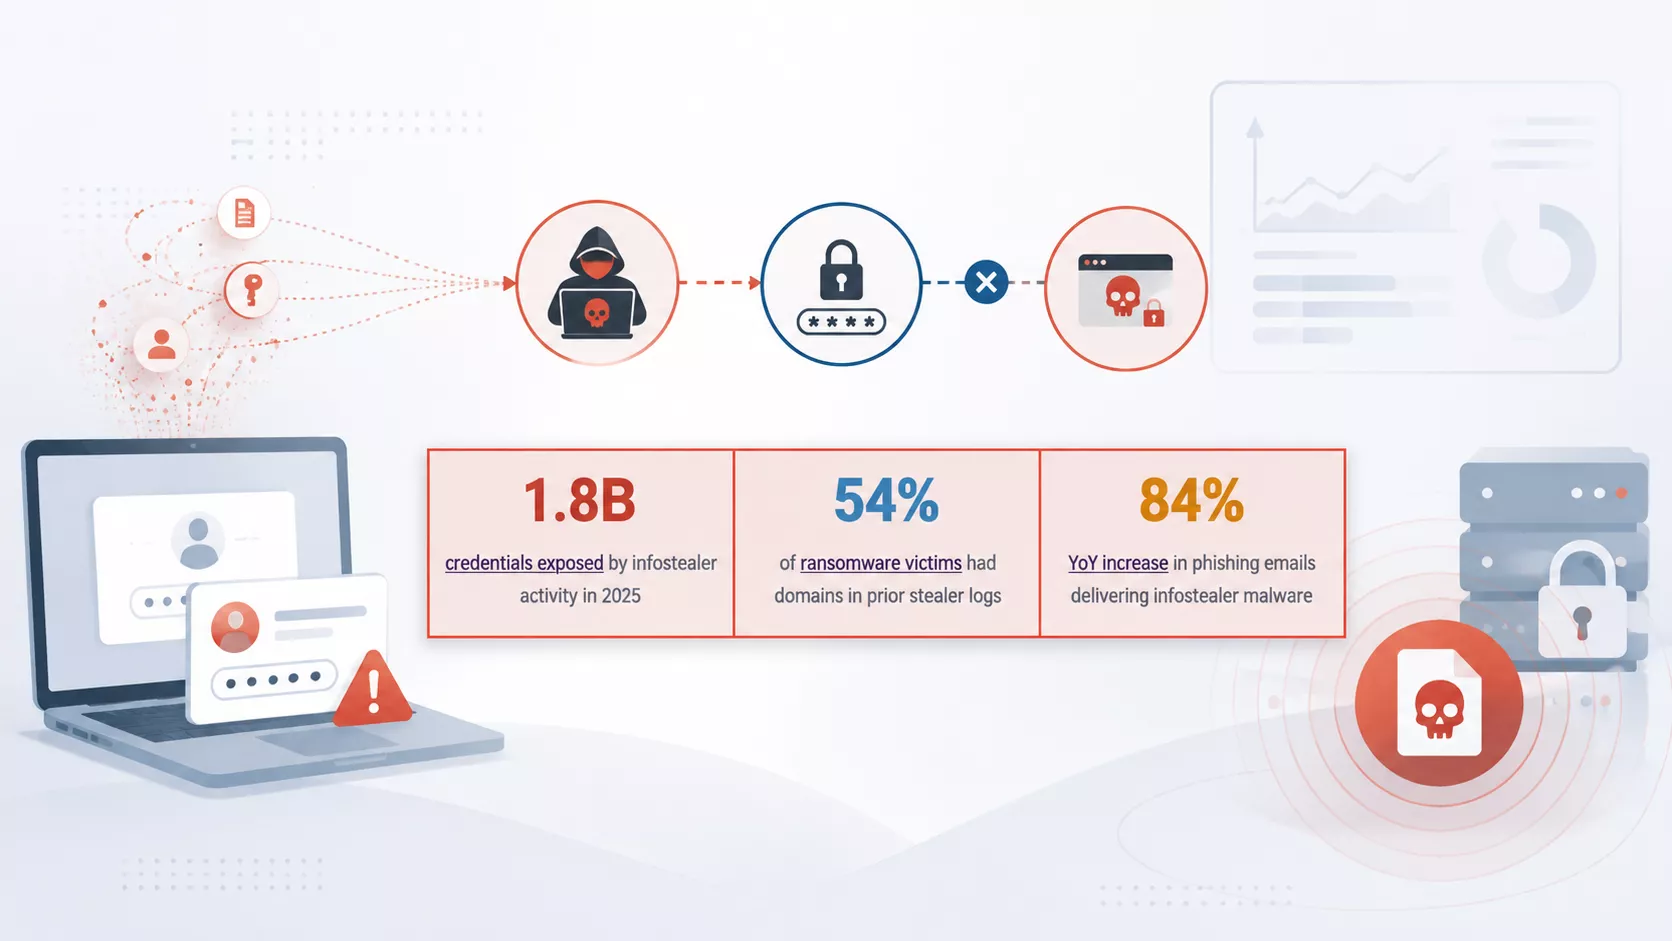

Infostealer malware has now become the invisible thread linking petty credential theft to full-blown ransomware campaigns. Attackers no longer bother forcing their way through firewalls when infostealers have already unlocked the front door for them.
Documented by DarkOwl, a stealer log archive generated by infostealer malware that silently harvests browser-saved passwords, session cookies, cryptocurrency wallet data, and system fingerprints from an infected device without the victim noticing.
Unlike ransomware, which announces itself with encrypted files and ransom notes, infostealers operate quietly, allowing the same compromised machine to keep functioning normally while data is continuously exfiltrated to attacker-controlled servers.
Hackers Use Stealer Logs to Bypass MFA
These logs are then aggregated and resold by initial access brokers, who act as intermediaries supplying compromised credentials directly to ransomware affiliates.

The most operationally dangerous element inside a stealer log is not the password; it is the active session cookie. When a user completes MFA on a website, the browser stores a token confirming the device already authenticated, and that token often remains valid until explicit logout or expiration.
An attacker who imports a stolen session cookie into their own browser inherits the authenticated state entirely, accessing the account with no password and no new MFA challenge triggered.
DarkOwl describes this as session hijacking, one of at least six distinct techniques alongside push bombing, adversary-in-the-middle phishing, and SIM swapping that attackers now use to defeat multi-factor authentication.
Because stolen tokens work only while the session remains valid, shorter session lifetimes and monitoring for tokens appearing on criminal markets are among the few effective countermeasures against this attack path.
Verizon’s 2025 Data Breach Investigations Report found that 88 percent of web-application breaches involved stolen credentials, many originating from infostealer logs that are reused in credential-stuffing campaigns against corporate SSO portals and cloud services.
Initial access brokers specifically filter massive log collections for corporate VPN credentials, SSO tokens, and domain administrator access, then resell qualifying logs at a premium to ransomware affiliates who log directly into target networks and bypass perimeter defenses entirely.

This pipeline has been formalized through “Underground Clouds of Logs,” massive searchable databases where criminals look up victims by country, company domain, or specific application, dramatically shortening the time between infection and exploitation.
In June 2026 alone, a consolidated collection of accumulated stealer logs containing 124 million unique passwords was documented circulating across underground channels, illustrating the sheer scale at which this data now moves.
DarkOwl notes that distribution channels for these logs, including Telegram groups functioning as an alternative to traditional dark web forums, have made stolen credentials and cookies easier than ever for less-skilled buyers to acquire in bulk.
Because stolen credentials and cookies remain valid and tradeable indefinitely unless explicitly revoked, organizations face a persistent, compounding risk long after the original infection occurred.
Remediation guidance from incident responders emphasizes that revoking access and terminating active sessions must happen before password resets, since a reset password does little to stop an attacker who already holds a live session token.
As MFA adoption becomes near-universal, stolen session cookies, not stolen passwords, have become the primary currency enabling ransomware affiliates to walk through the front door of enterprise networks undetected.
ALERT: 20+ government sites delivered malware to businesses and citizens. See full attack research to check your own exposure.


