

In a new attack wave, MooBot, a variant of Mirai botnet malware, has been detected recently by the cybersecurity experts at Palo Alto Network’s Unit 42.
At the beginning of last month, a new wave of attacks began to appear. This new wave of attacks targeted mostly vulnerable D-Link routers as part of this malicious campaign.
As a result of an analysis carried out by Fortinet analysts in December 2021, the Mirai variant, MooBot was discovered. It has been reported that the malware has updated the scope of its targeting now.
In fact, botnets are likely to seek out untapped puddles of vulnerable devices that they can use as bait in order to entrap their victims.
Flaws Targeted in D-Link Devices
There are several vulnerabilities in D-Link devices but among them, MooBot targeted the four critical ones, and here they are mentioned below:-
- CVE-2015-2051: D-Link HNAP SOAPAction Header Command Execution Vulnerability (CVSS Version 2.0: 10.0 High)
- CVE-2018-6530: D-Link SOAP Interface Remote Code Execution Vulnerability (CVSS Version 3.0: 9.8 Critical)
- CVE-2022-26258: D-Link Remote Command Execution Vulnerability (CVSS Version 3.0: 9.8 Critical)
- CVE-2022-28958: D-Link Remote Command Execution Vulnerability (CVSS Version 3.0: 9.8 Critical)
The vulnerabilities could be exploited remotely by attackers to execute code on the host 159.203.15[.]179 and download MooBot downloader from the host.

There have been security updates released by the vendor to mitigate the impact of the flaws. However, not all of the updates have been applied by all users.
Technical Analysis
There is a low attack complexity associated with the flaws which are exploited by the operators of MooBot. A malicious binary is retrieved by using arbitrary commands when RCE is gained on the targets.
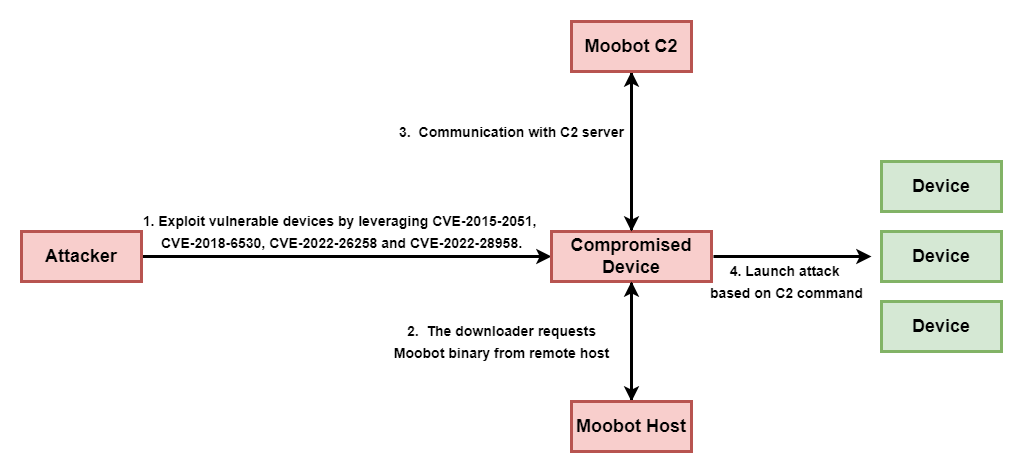
On the C2 that is under the control of the threat actors, all the newly captured routers are recorded. Once the malware has decoded the configuration file’s hardcoded address, this calculation is carried out.
The addresses for C2 in Unit 42’s report are different from those in Fortinet’s report, which is a significant difference to pay attention to. An indication that the infrastructure of the threat actor has been refreshed.
A compromised D-Link device may cause users to notice a number of symptoms like:-
- Internet speed drop issues
- Unresponsiveness
- Router overheating
- Uncertain DNS configuration changes
Recommendations
In order to avoid this problem, cybersecurity researchers have urged users to update patches and software whenever possible. It is recommended that you follow the following recommendations if you believe that you may have already been compromised:-
- It is recommended that you reset your router.
- The password for your admin account needs to be changed.
- Make sure you have the latest security updates installed.
Download Free SWG – Secure Web Filtering – E-book







