
Attackers are leaning harder on legitimate, preinstalled, or widely used system tools to deliver and operate notorious malware families, creating a stealthy, high-velocity threat that outpaces many traditional defenses.
The operational logic for attackers is straightforward. Native utilities such as PowerShell, Windows Management Instrumentation (WMI), certutil, mshta, and JavaScript execution contexts already enjoy elevated privileges and unimpeded access to system resources.
When abused, they allow adversaries to drop loaders that fetch second-stage payloads, execute fileless code in memory, and blend with legitimate administrative activity.
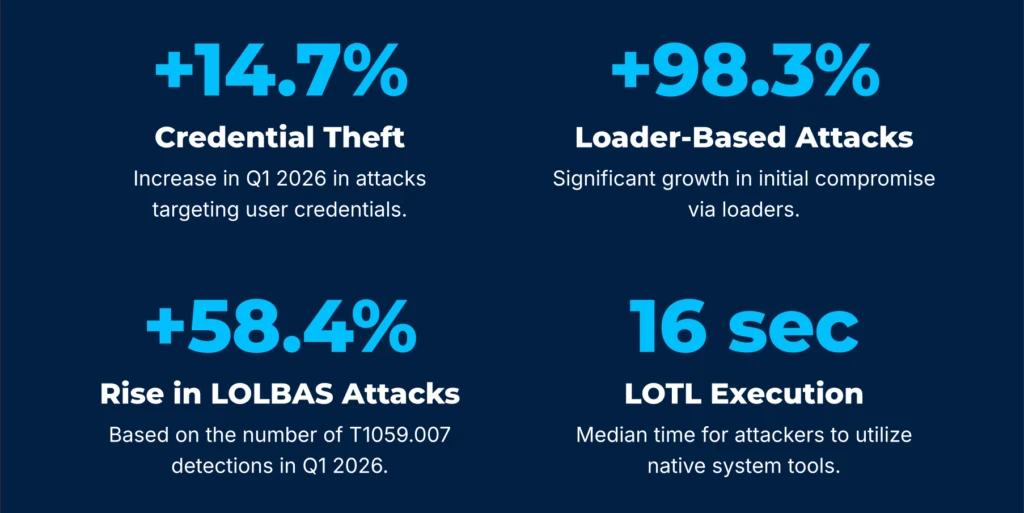
The result is faster initial compromise and harder-to-detect persistence: the report cites median times as low as 21 seconds to establish persistence and 16 seconds to Living-off-the-Land execution.
In practice, that gives defenders an extremely narrow window to detect and interrupt an intrusion before an attacker achieves a durable foothold.
ANY.RUN said in a report shared with GBhackers, Q1 2026 Cyber Risk report 2,101,483 malware and phishing investigations in shows a clear shift: Loader-based attacks almost doubled, credential theft rose 14.7%, and low-noise Living-off-the-Land (LOLBAS/LOTL) techniques climbed 58.4%.
Loader-based campaigns are particularly illustrative. Attackers increasingly use lightweight loaders to perform early-stage compromise, then pivot to well-known ransomware, remote-access trojans (RATs), or info-stealers once credentials or privileged access are obtained.
ANY.RUN’s telemetry shows a near doubling in loader activity in Q1 2026, driving an uptick in subsequent credential theft and lateral movement.
Hackers Weaponize Trusted Tools
Credential harvesting remains a top objective because valid credentials permit low-noise lateral escalation and obfuscation of attribution.
The blended use of stolen credentials with trusted tool abuse creates scenarios where behavior-based monitoring and anomaly detection are essential, since static signature-based controls frequently miss abuse of legitimate binaries.
Detection and response challenges multiply because trusted tools often generate benign-looking telemetry.
Security teams must therefore tune detection to identify subtle deviations: atypical command-line arguments, unusual parent-child process relationships, suspicious network destinations tied to temporary loader infrastructure, or sudden use of scripting interpreters by nonadmin users.
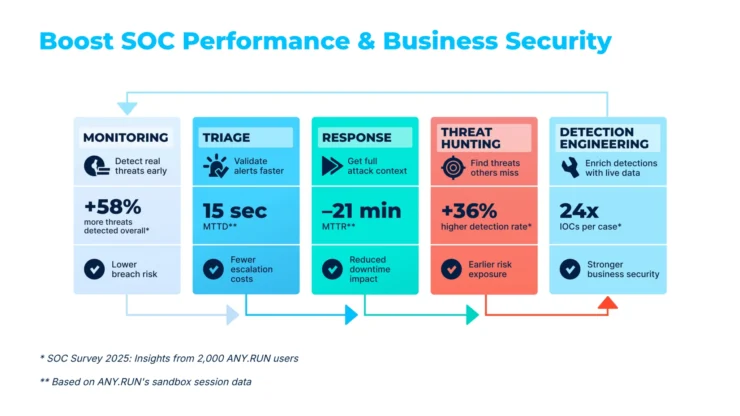
ANY.RUN recommends coupling behavioral baselines with rapid sandboxing and threat intelligence to validate whether observed activity truly indicates a threat.
Their Q1 2026 Cyber Risk report argues that enterprise-scale malware analysis and fast threat validation materially shorten investigation time and reduce business impact; organizations using sandbox and TI capabilities can confirm exposure to credential theft, C2 traffic, or fileless execution faster.
Practical steps include applying application control to restrict risky tool invocation, enforcing least privilege, hardening endpoints against script execution, integrating deception or canary credentials to detect illicit authentication, and funneling suspicious activities into automated analysis platforms.
ANY.RUN’s report provides deeper technical observations and seven key trends with actionable recommendations for Q2 2026; security leaders are encouraged to review the full findings to align SOC priorities with evolving attacker behavior.
For defenders facing this new normal, speed and contextual certainty are the differentiators.
The weaponization of trusted tools won’t stop adversaries will keep refining how they hide in plain sight so organizations must shift from relying on signatures to building detection, response, and intelligence workflows that surface the smallest indicators of compromise and act on them immediately.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


