

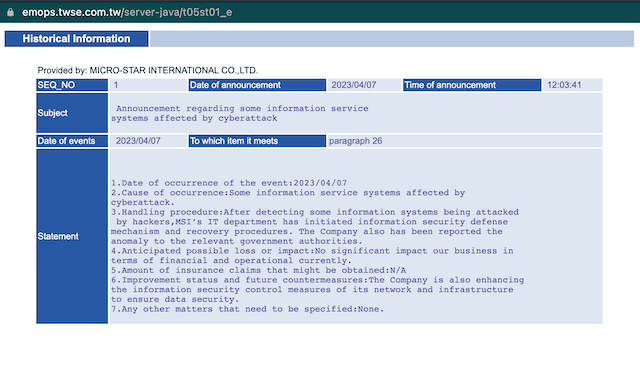
A cyberattack was recently launched on some of the information systems of the multinational Taiwanese technology company Micro-Star International (MSI) Co., Ltd.
According to MSI’s statement, the incident was swiftly reported to law enforcement authorities, and recovery efforts have begun.
“Upon detecting network anomalies, the information department promptly activated relevant defense mechanisms and carried out recovery measures, and reported the incident to government law enforcement agencies and cybersecurity units,” MSI explains.
With annual sales of $6.5 billion, MSI is a major manufacturer of motherboards, graphics cards, desktops, laptops, servers, industrial systems, PC peripherals, and infotainment products.
Money Message Ransomware Gang Claims MSI Breach and Demands $4 Million Ransom
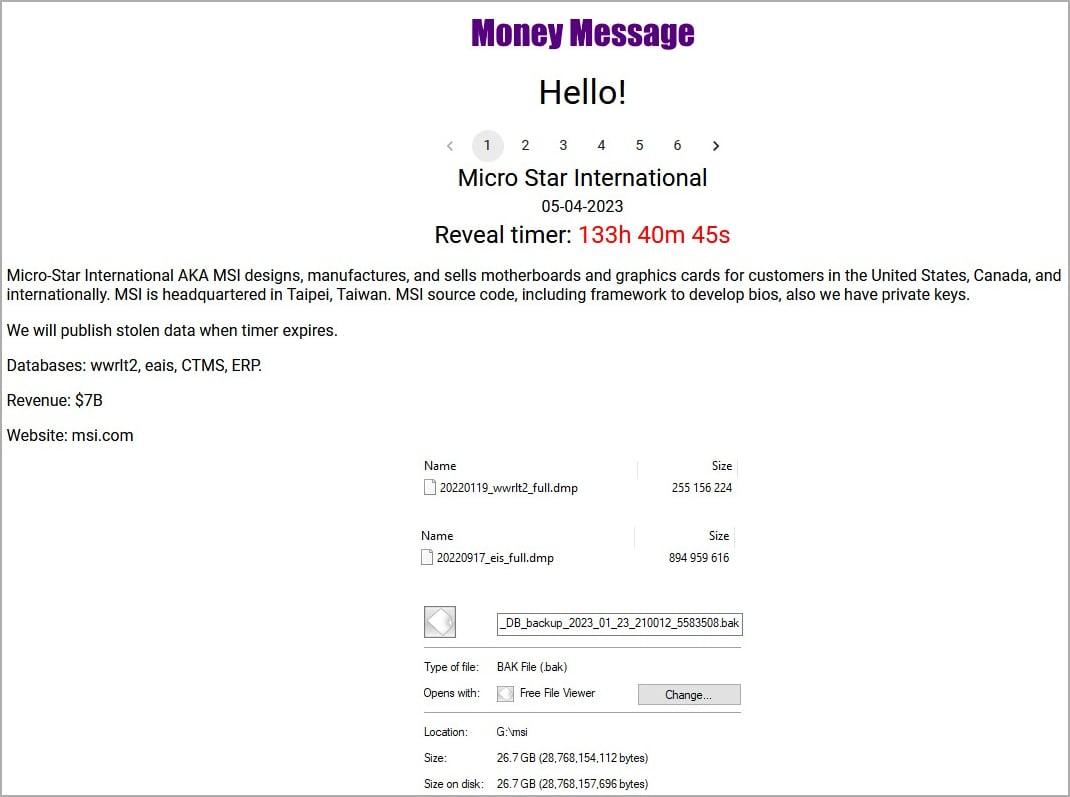
The company was added to the list of victims of the “Money Message ransomware” group this week. The group claims to have stolen the company’s CTMS and ERP databases and files holding source code, BIOS firmware, and private keys.
According to cybersecurity experts, the group only started operating this week. If MSI doesn’t comply with its demands for a ransom payment, Money Message now threatens to expose all of these supposedly stolen documents in around five days.
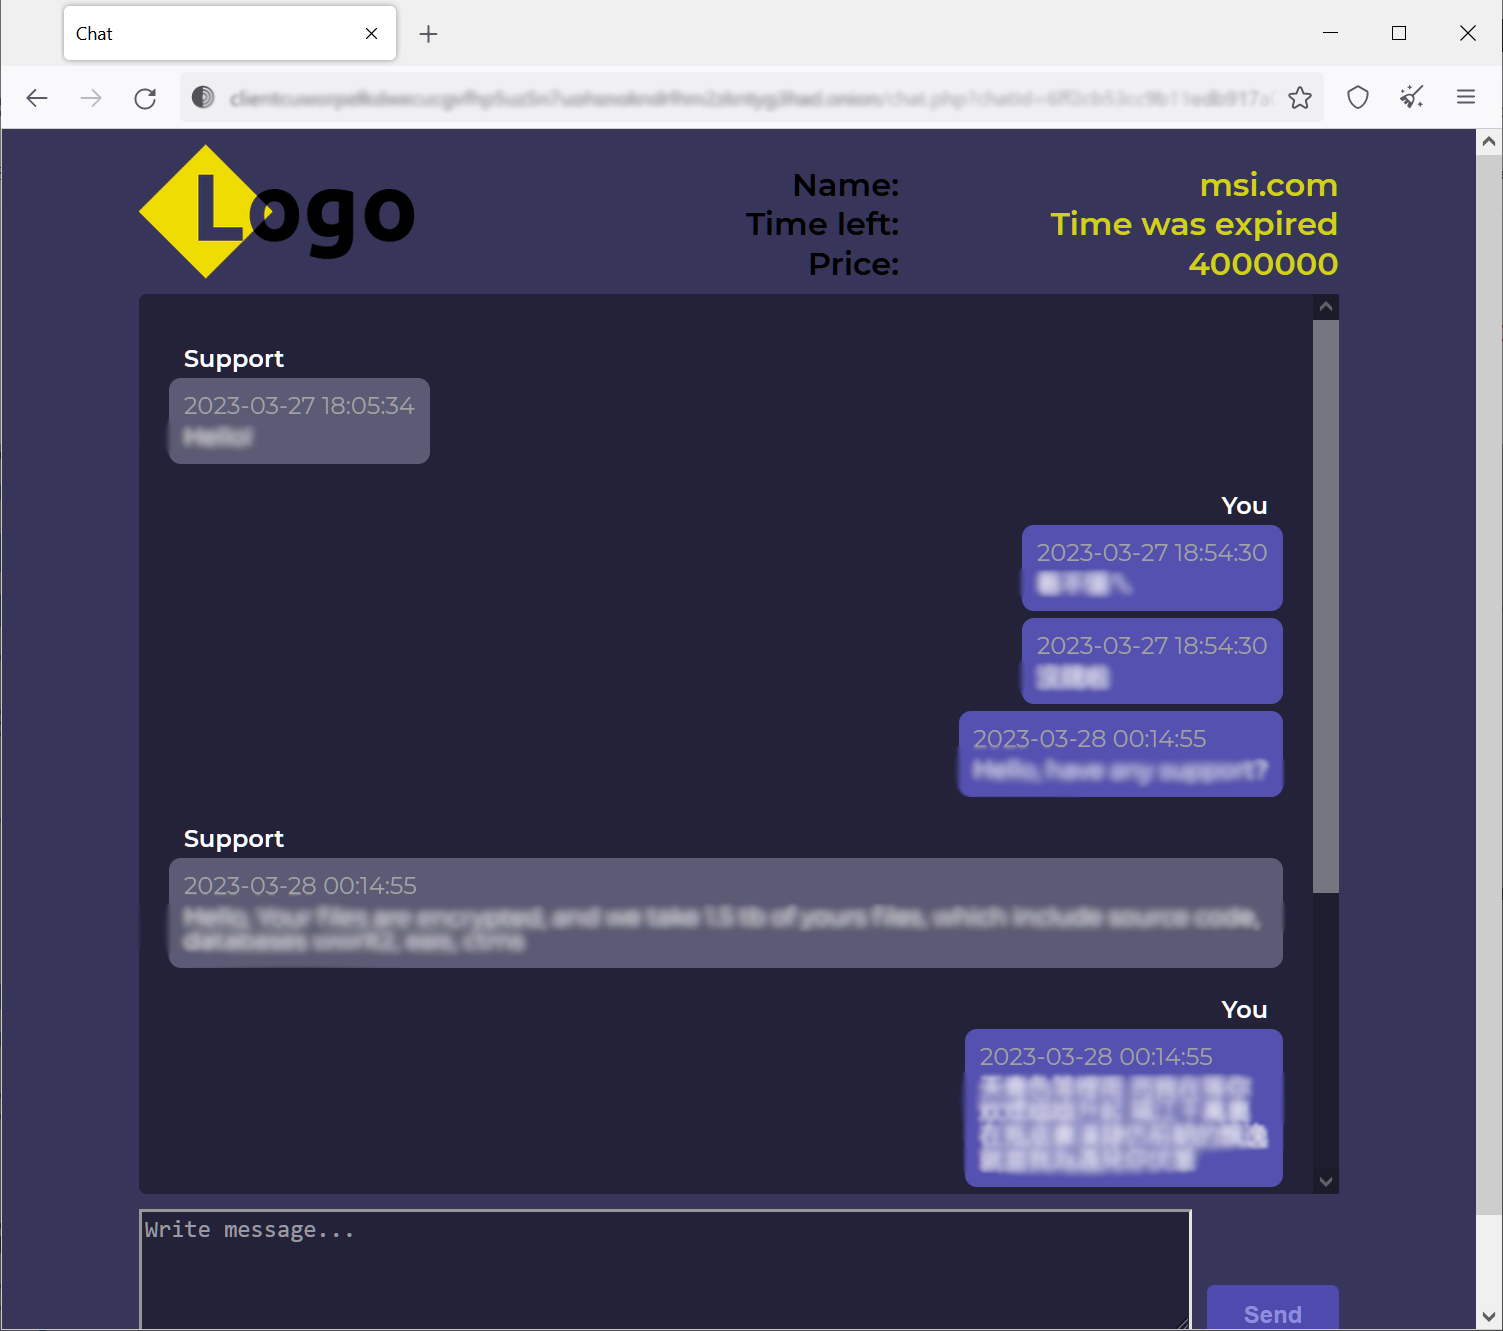
Notably, the threat actors allegedly demanded a $4,000,000 ransom in discussions viewed by BleepingComputer at the time, claiming to have stolen 1.5TB of data from MSI’s systems, including source code and databases.
In a communication with an MSI agent, a Money Message operator claimed, “Say your manager, that we have MSI source code, including framework to develop bios; also we have private keys able to sign in any custom module of those BIOS and install it on PC with this bios.
According to the company, there hasn’t been a significant impact on financial business as the damaged systems have progressively resumed normal operations.
“MSI urges users to obtain firmware/BIOS updates only from its official website, and not to use files from sources other than the official website”, the company said.
Struggling to Apply The Security Patch in Your System? – Try All-in-One Patch Manager Plus







 Co., Ltd.)