

The security researchers from Palo Alto Networks Unit 42 observed HelloXD ransomware targeting multiple windows and linux systems.
Daniel Bunce and Doel Santos, Researchers from Palo Alto Networks Unit 42 said in a recent blog, “Unlike other ransomware groups, this ransomware family doesn’t have an active leak site; instead, it prefers to direct the impacted victim to negotiations through TOX chat and onion-based messenger instances.”
The researchers noticed that one of the samples deployed MicroBackdoor, which is an open-source backdoor allowing an attacker to browse the file system, upload and download files, execute commands, and remove itself from the system.
Analysis of the MicroBackdoor
Unit 42 noted the configuration and found an embedded IP address, belonging to a threat actor, which the researchers guess is potentially the developer: x4k, also called L4ckyguy, unKn0wn, unk0w, _unkn0wn, and x4kme. They noticed x4k in several hacking and non-hacking forums.
The Malicious Activities of the Threat Actor
- Cobalt Strike Beacon deployment.
- Selling proof-of-concept (POC) exploits.
- Crypter services.
- Developing custom Kali Linux distros.
- Hosting and distributing malware.
- Deployment of malicious infrastructure.
Researchers detected HelloXD and x4k activity with the Cortex XDR and Next-Generation Firewalls (including cloud-delivered security subscriptions such as WildFire).
What is HelloXD Malware?
HelloXD surfaced in the wild on November 30, 2021, and is based off leaked code from Babuk, which was published on a Russian-language cybercrime forum in September 2021.
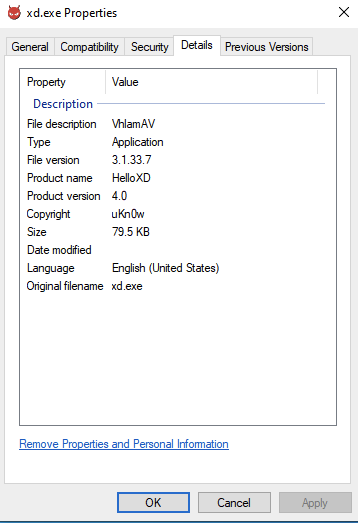
Reports say this ransomware family uses a modified ClamAV logo in their executables. ClamAV is an open-source antivirus engine used to detect malware.
In the samples analyzed, the ransomware note was modified, where the ransom note only linked to a TOX ID (the first image), while a later observed sample links to an onion domain as well as a TOX ID, different from the one in the first version, (the second image).
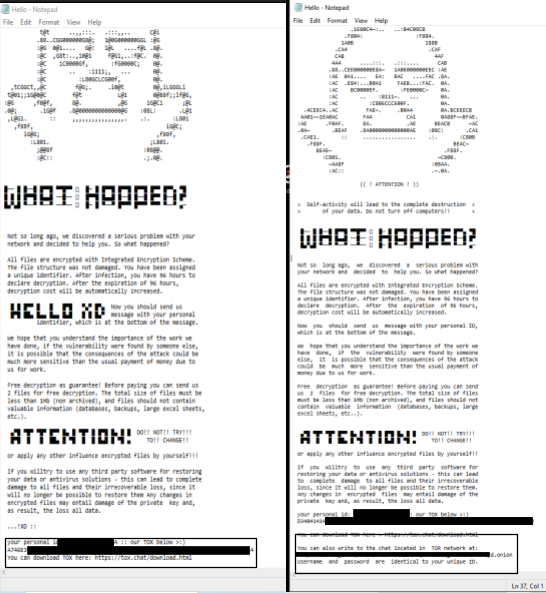
Also, the ransomware creates an ID for the victim which is sent to the threat actor to identify the victim and provide a decryptor. Researchers say the ransom note also commands victims to download Tox (peer-to-peer instant messaging protocol) and provides a Tox Chat ID to reach the threat actor.
During the analysis of both variants, “We noted that the more recent variants changed the background to a ghost – a theme we’ve noticed in this threat actor’s work since our earliest observations of it”.
According to the researchers, “The x4k has a very solid online presence, which has enabled us to uncover much of his activity in these last two years. This threat actor has done little to hide malicious activity and is probably going to continue this behavior.”
Therefore, the research team from Palo Alto Networks analyzed HelloXD, a ransomware family at its beginning stage. They say the ransomware is probably developed by a threat actor called x4k. Also, this threat actor, x4k is currently developing into the ransomware business to capitalize on some of the gains other ransomware groups are making, they concluded.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.







