

In an attempt to identify and track down six Russian GRU hackers who are members of the notorious Sandworm hacking group, the U.S. government is offering a reward of up to $10 million.
The U.S. government stated:-
“We are offering this bounty as part of the Department of State’s Rewards for Justice program as part of our commitment to pursuing justice.”
As part of this bounty program, informants are rewarded for information that helps identify or locate foreign government actors who may pose threats to the United States.
There are a number of threat actors that are specifically targeting critical infrastructure in the United States in order to carry out malicious cyber operations.
$10 Million Reward
For information leading to the identification or location of threat actors operating in the global computer network, Rewards for Justice is offering a reward of up to 10 million dollars.
They are mainly targeting the threat actors who perform the following tasks and come under the following bodies:-
- Direction or comes under the control of a foreign government.
- Participates in malicious activities against U.S. critical infrastructure in violation of the CFAA (Computer Fraud and Abuse Act).
It should be noted that the CFAA is violated in certain instances by malicious cyber attacks on the critical infrastructure of the US. Ransomware attacks are a form of extortion, and transmitting extortion threats as part of the attack is a violation of the statute.
However, the US Department of State has recently declared that they are searching for information about six Russian officers from the Main Intelligence Directorate of the GRU.
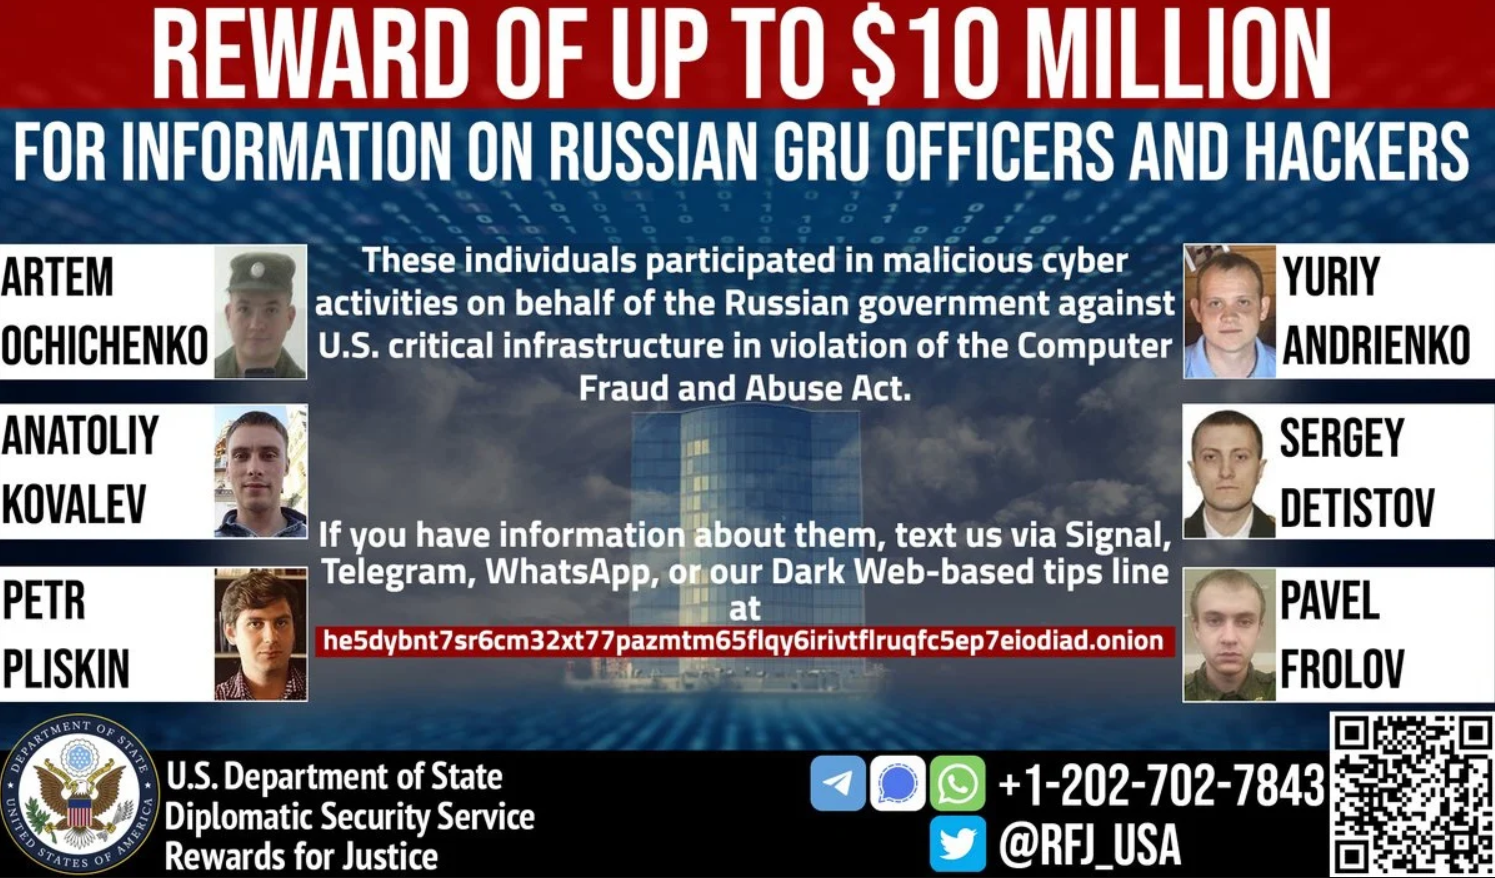
While all the above mentioned six individuals were indicted by the Department of Justice in 2020 as part of the Sandworm group, a Russian hacking group that is also known as:-
- Team
- Telebots
- Voodoo Bear
- Iron Viking
Furthermore, the Rewards of Justice is also seeking information about threats posed by other entities like:-
- REvil ransomware
- DarkSide ransomware
- North Korean cybercrime threat actors
- Nation-state hackers targeting U.S. businesses and critical infrastructure sectors.
A Tor website has also been set up by the Rewards of Justice, and here it is:-
- Hhe5dybnt7sr6cm32xt77pazmtm65flqy6irivtflruqfc5ep7eiodiad.onion
And the above-mentioned website could be used to submit tips about these threat actors anonymously.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.







