

A threat actor known as IntelBroker has taken to a prominent dark web forum to claim a significant data breach at Hewlett Packard Enterprise (HPE).
The alleged breach reportedly includes a vast array of sensitive information, raising concerns about the security of HPE’s data infrastructure and the potential implications for its customers and partners.
Details of the Alleged Breach
According to the claims made by IntelBroker, the breach encompasses a variety of critical data types.
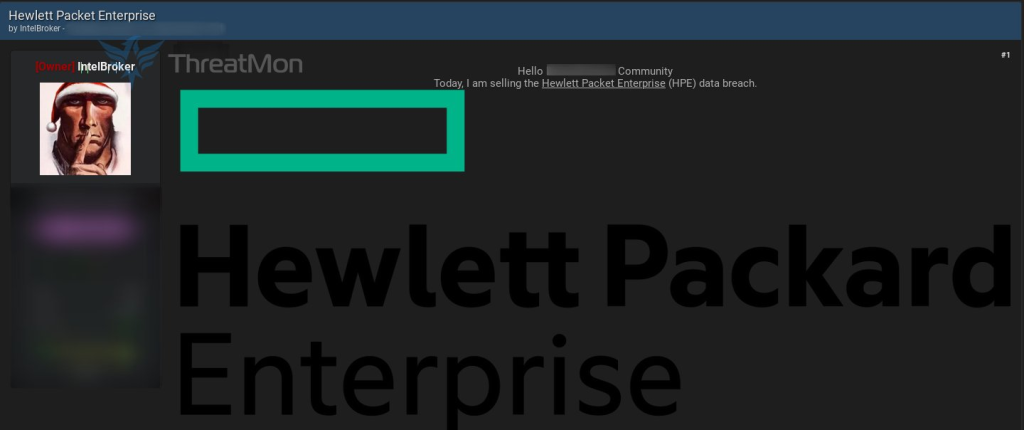
The hacker asserts that they have gained access to private GitHub repositories, which could contain proprietary code and development assets vital for HPE’s operations.
Furthermore, the breach includes Docker builds, SAP Hybris configurations, and essential cryptographic certificates—both public and private keys.
Investigate Real-World Malicious Links & Phishing Attacks With Threat Intelligence Lookup - Try for Free
Notably, the threat actor has also mentioned that product source code for key HPE technologies, such as Zerto and iLO, has been compromised.
In a particularly concerning revelation, IntelBroker alleges the exposure of legacy user personally identifiable information (PII) related to deliveries and access credentials for WePay and self-hosted GitHub accounts.
This data could pose serious risks not only to HPE but also to its customers, as PII can be exploited for identity theft and fraud.
If confirmed, this breach could have far-reaching consequences for HPE, both from a reputational and financial perspective.
The exposure of source code and sensitive PII might lead to long-lasting impacts on customer trust, potentially affecting future business engagements.
Additionally, HPE may face regulatory scrutiny, especially given the stringent data protection laws that govern the handling of personal information.
Cybersecurity experts are closely monitoring the situation and warn organizations to enhance their security measures in light of this incident.
The disclosure of such critical data could embolden other threat actors to exploit similar vulnerabilities within corporate environments.
As of now, HPE has not publicly addressed the claims made by IntelBroker. Industry analysts are urging the company to respond promptly to mitigate potential damage and reassure stakeholders.
A thorough investigation into the claims is essential to ascertain the veracity of the breach and to take necessary countermeasures.
In an increasingly interconnected digital landscape, the incident serves as a sobering reminder for organizations to continuously assess their cybersecurity postures and be vigilant against the evolving tactics of cybercriminals.
The potential fallout from the alleged breach of HPE’s data underscores the critical need for robust security protocols and incident response plans.
Integrating Application Security into Your CI/CD Workflows Using Jenkins & Jira -> Free Webinar







.)