

RaaS (Ransomware-as-a-service) is actively strengthening the ransomware attacks, but understanding their operations is restricted by illegality.
That’s why ransomware attacks have surged in scale and complexity over the past decade, driven by RaaS models like Conti (formerly Ryuk).
However, the Conti RaaS (Ransomware-as-a-service) operator’s recent chat leak provides valuable insights into their inner workings.
The following cybersecurity researchers from their respective universities recently analyzed the leaked internal discussions of a large Ransomware-as-a-Service model, Conti ransomware with ML (Machine Learning):-
- Estelle Ruellan (University of Montreal)
- Masarah Paquet-Clouston (University of Montreal)
- Sebastian Garcia (Czech Technical University)
Ransomware devastates enterprises by locking devices or encrypting files for extortion, making it a significant IT threat studied for prevention and detection.
Over the past decade, ransomware has transformed. Initially, small-scale attacks were common, but now, attackers compromise advanced systems for higher profits through varied extortion tactics.
Internal Discussions Conti Ransomware
The research used chat files from TheParmak GitHub, offering open-source access to Conti chats translated into English via Google and DeepL.
These logs span from June 21, 2020, to March 2, 2022, totaling 168,711 chats involving 346 actors, with each log including the following data in JSON format:-
- Date
- Sender
- Receiver
- Message
To identify Conti members’ discussion topics, researchers employed Latent Dirichlet Allocation (LDA), a topic modeling method commonly used in NLP to extract latent topics from document corpora, offering explicit document representations and applying them across fields like:-
- Cybersecurity
- Medicine
- Political science
Security analysts applied Natural Language Processing (NLP) to cleanse the chats, a subfield of AI teaching machines to understand and extract meaning from human language using algorithms and grammatical rules.
Types of topics covered are as follows:-
- Business topic
- Technical topic
- Internal tasking topic
- Management topic
- Malware topics
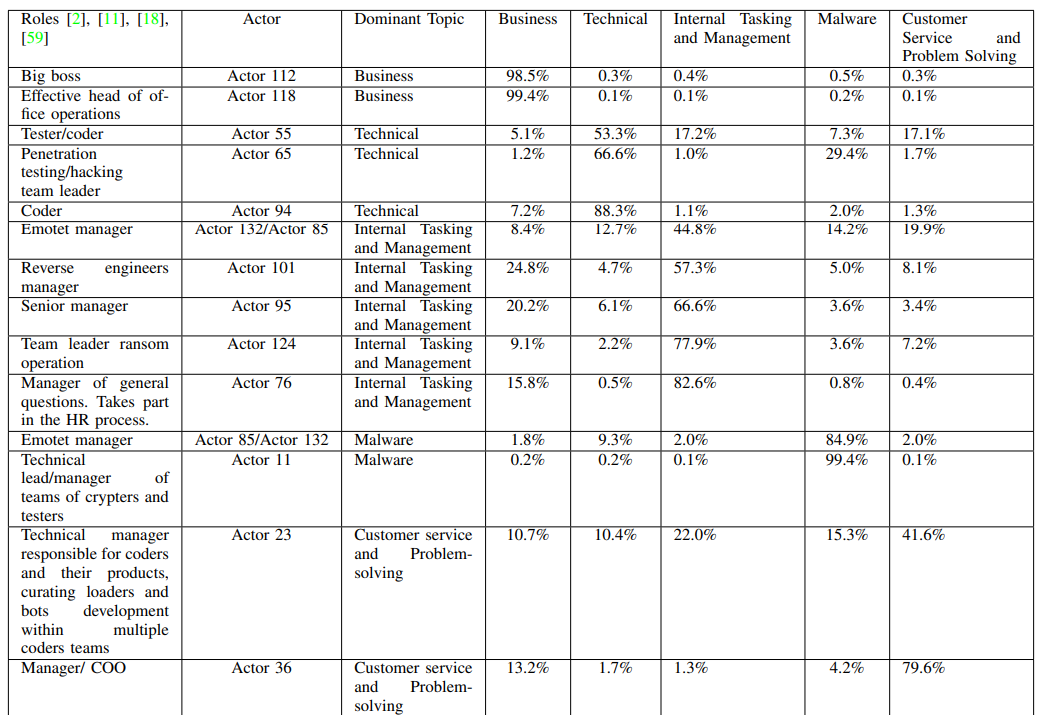
The Conti RaaS operator, a major player, might be an exception in its organization. The structure of RaaS operators could relate to their size, scope, success, and geographical locations.
Besides this, future research should explore other cybercrime organizations for structural insights.
Using Conti chat leaks, the experts employed machine learning analysis that reveals cybercrime organizations mirror businesses with diverse discussions, confirming the significance of non-tech talks and managerial styles.
Keep informed about the latest Cyber Security News by following us on Google News, Linkedin, Twitter, and Facebook.


 is actively strengthening the ransomware attacks, but understanding their operations is restricted by illegality. )