

Despite extensive scrutiny and public reporting, commercial surveillance vendors continue to operate with alarming sophistication.
Intellexa, a prominent mercenary spyware provider known for its “Predator” surveillance tool, has adapted to evade international sanctions and restrictions, establishing itself as one of the most prolific exploiters of zero-day vulnerabilities targeting mobile devices.
Recent analysis from Google’s Threat Intelligence Group (GTIG), complemented by research from Recorded Future and Amnesty International, reveals that Intellexa not only persists but thrives in exploiting critical security flaws across multiple platforms.
The company has demonstrated a remarkable ability to procure, develop, and deploy zero-day exploits with unprecedented efficiency.
Since 2021, Intellexa has been attributed to 15 unique zero-day vulnerabilities, accounting for a substantial portion of the critical flaws identified by Google’s Threat Analysis Group during this period.
These exploits span Remote Code Execution (RCE), Sandbox Escape (SBX), and Local Privilege Escalation (LPE) vulnerabilities across iOS, Android, Chrome, and ARM Mali architectures.
Notably, evidence suggests that Intellexa increasingly purchases exploit chain components from external entities rather than developing them entirely in-house, indicating a sophisticated supply chain within the surveillance industry.
Bypassing iOS Security Protections
One particularly sophisticated iOS exploit chain, internally referred to as “smack” by Intellexa, showcases the technical complexity of their operations.
The framework can parse in-memory Mach-O binaries to resolve custom symbols and can ultimately manually map and execute Mach-O binaries directly from memory.
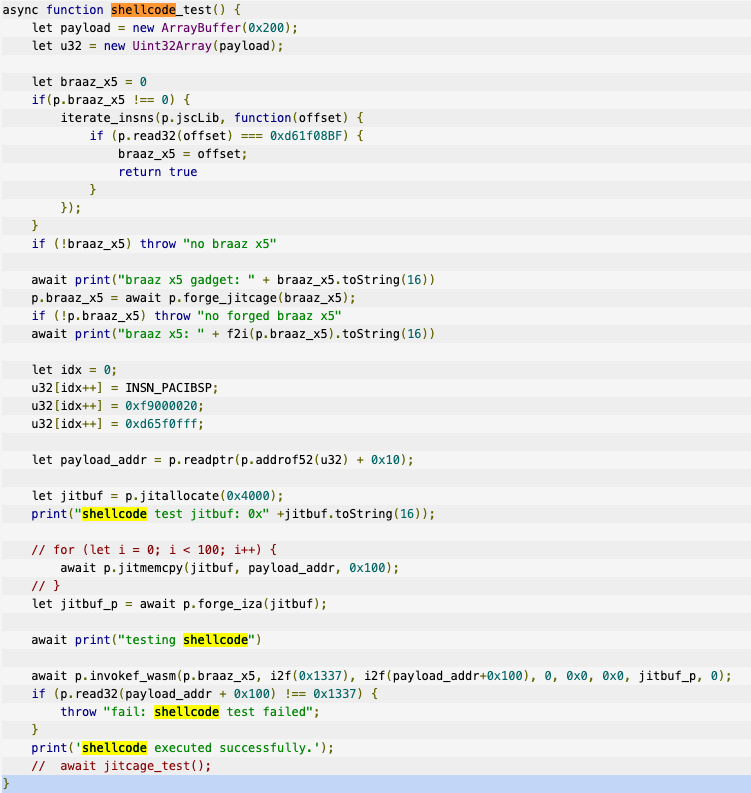
his multi-stage attack chain begins with CVE-2023-41993, a Safari RCE vulnerability that enables arbitrary memory access through a framework called JSKit.
Security researchers believe Intellexa acquired this iOS RCE exploit from an external source, as the identical JSKit framework has appeared in campaigns by Russian government-backed attackers and other surveillance vendors since 2021.

The framework’s modularity, support for diverse iOS versions, and robust engineering suggest its developer maintains an extensive arsenal of iOS exploits debug strings recovered from the attack indicate Intellexa possessed at least seven variants of iOS exploits.
Subsequent stages of the exploit chain escalate privileges by exploiting kernel vulnerabilities CVE-2023-41991 and CVE-2023-41992, ultimately enabling system-level code execution.
The final stage, designated PREYHUNTER, deploys spyware modules including “helper” and “watcher” components.
The watcher module implements intrusion detection capabilities, monitoring for indicators of device compromise such as developer mode activation, debugger attachment, suspicious applications, and security software installation.
Upon detection, it terminates the exploitation process a safeguard suggesting operators first verify target authenticity before deploying the full Predator spyware suite.
The helper module establishes persistence through Unix sockets and implements reconnaissance capabilities, including VOIP call recording, keystroke logging, and camera access.
Google’s analysis indicates these capabilities serve as screening mechanisms for operators to confirm successful infection before deploying more resource-intensive surveillance functionality.
Protecting Devices from Future Attacks
Beyond zero-day exploitation, Intellexa has expanded delivery mechanisms to include malicious advertisements on third-party platforms for targeted user fingerprinting and redirection to exploit servers.
This advertising-based delivery approach represents an escalation in operational sophistication and has prompted platforms to shut down accounts associated with Intellexa’s intermediary companies.
In response to these threats, Google has issued government-backed attack warnings to several hundred targeted accounts across Pakistan, Kazakhstan, Angola, Egypt, Uzbekistan, Saudi Arabia, and Tajikistan since 2023.
The company has also added identified Intellexa infrastructure to Safe Browsing protections and continues participating in international frameworks, including the Pall Mall Process, aimed at establishing norms limiting commercial spyware proliferation.
The persistence of Intellexa’s operations despite US sanctions underscores the urgent need for strengthened international coordination and enforcement mechanisms to curtail the mercenary surveillance industry’s expansion.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.





