
Iran-linked operators have mounted a broad espionage operation against multiple Omani ministries, abusing exposed webshells, SQL escalation scripts, and a poorly secured C2 server to steal judicial and identity data at scale.
Attacker’s own open directory strongly suggests a Ministry of Intelligence and Security (MOIS) nexus compromised a mailbox , but there are not enough unique artifacts for firm group-level attribution.
An exposed RouterHosting VPS at 172.86.76[.]127 in the UAE hosted the entire toolkit for an active intrusion into Oman’s government networks, including webshells, Python exploit scripts, C2 code, logs, and exfiltrated data.
The primary victim was the Ministry of Justice and Legal Affairs (MJLA), but recovered files show activity against at least 11 government entities, from the Royal Oman Police to the Tax Authority and civil aviation portals.
This campaign follows earlier MOIS-linked abuse of an Omani MFA mailbox in Paris for global spear-phishing, indicating Oman remains a recurring access point and target for Iran-aligned espionage.
Key findings from the exposed server include a custom ASP.NET webshell on mersaltest.mjla.gov[.]om, SQL Server escalation tooling, and evidence of large-scale data theft, including more than 26,000 DotNetNuke user records and Windows registry hives.
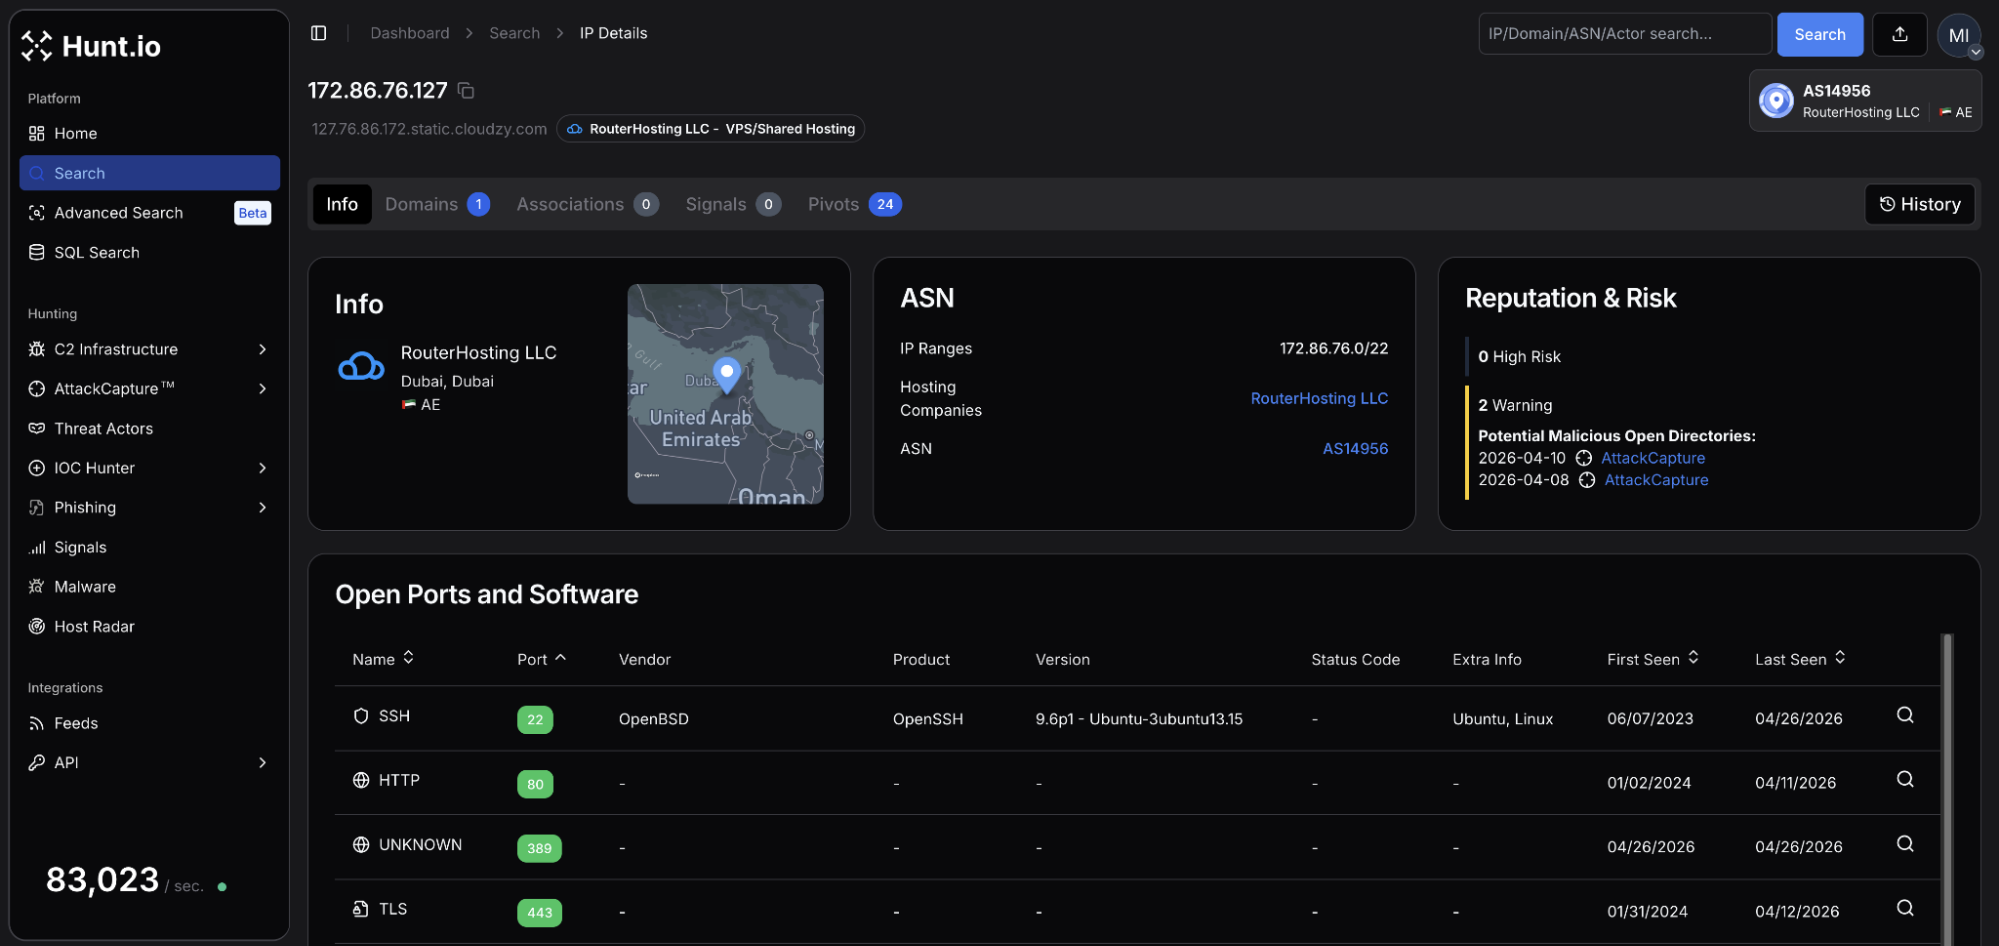
A README on the VPS labels it “VPS C2 – 172.86.76[.]127,” implying this node is part of a wider but still unmapped infrastructure set.
Iran Hackers Target Oman Ministries
AttackCapture scans first flagged an open directory on port 8000 on April 8, 2026, showing early-stage reconnaissance and exploitation attempts against multiple gov[.]om services.
Targets included the Royal Oman Police eVisa portal, Royal Fleet of Oman and Tax Authority Exchange servers (via ProxyShell), and a State Audit Institution training platform hit with brute-force attempts.
| Target | Organization | Observed Activity |
|---|---|---|
| evisa.rop.gov[.]om | Royal Oman Police eVisa portal | Password brute force attempts |
| mail.rfo.gov[.]om | Royal Fleet of Oman – VIP air transport | ProxyShell exploitation (CVE-2021-34473/34523/31207) |
| email.taxoman.gov[.]om | Tax Authority of Oman | ProxyShell exploitation (CVE-2021-34473/34523/31207) |
| sailms.gov[.]om | Training platform for the State Audit Institution (SAI) of Oman | Password brute force attempts |
A dedicated proxyshell_01.sh script focused on vulnerable Exchange endpoints, while a separate evisa_cookies.txt file indicates successful credential-based access to the eVisa portal despite no confirmed ProxyShell compromise.
By April 10, a second directory on port 8002 revealed a matured operator workspace with 211 files and 17 subdirectories, including payloads for Chisel tunneling and a scripts/gov[.]om folder containing tailored Python tooling for individual ministries.
Two key webshells underpin this activity: hc2.aspx, recovered directly from the C2 server, and health_check_t.aspx, hardcoded across MJLA-focused scripts and deployed under DotNetNuke’s /Portals/0/ path for command execution.
The operator leveraged the webshell to run PowerShell and SQL commands for credential access, lateral movement, and bulk data extraction.
They enumerated DotNetNuke schemas and targeted aspnet_Membership entries to identify superusers, dumping hashes for offline cracking while pivoting toward a “MOLADB” database.
Queries against the eGov_Person table show a clear focus on national ID records, including citizen names (Arabic and English), birthdates, nationality, and other high-value identity attributes.
C2 logs from April 10, 2026, document a systematic sequence of commands: host profiling, network discovery, database mapping, then export of judicial case data, session attachments, committee decisions, and expert certifications.
In one session, the attacker exfiltrated 26,596 MJLA DotNetNuke user records, capturing staff email addresses and credential data alongside Windows SAM and SYSTEM registry hives staged under C:\Windows\Temp before exfiltration.
Data Theft Campaign
The 172.86.76[.]127 VPS hosted a Python HTTP C2 stack and a PowerShell beacon (new_beacon.ps1) polling every 30 seconds for JSON-formatted tasking over port 8001, with results returned in base64-encoded chunks.
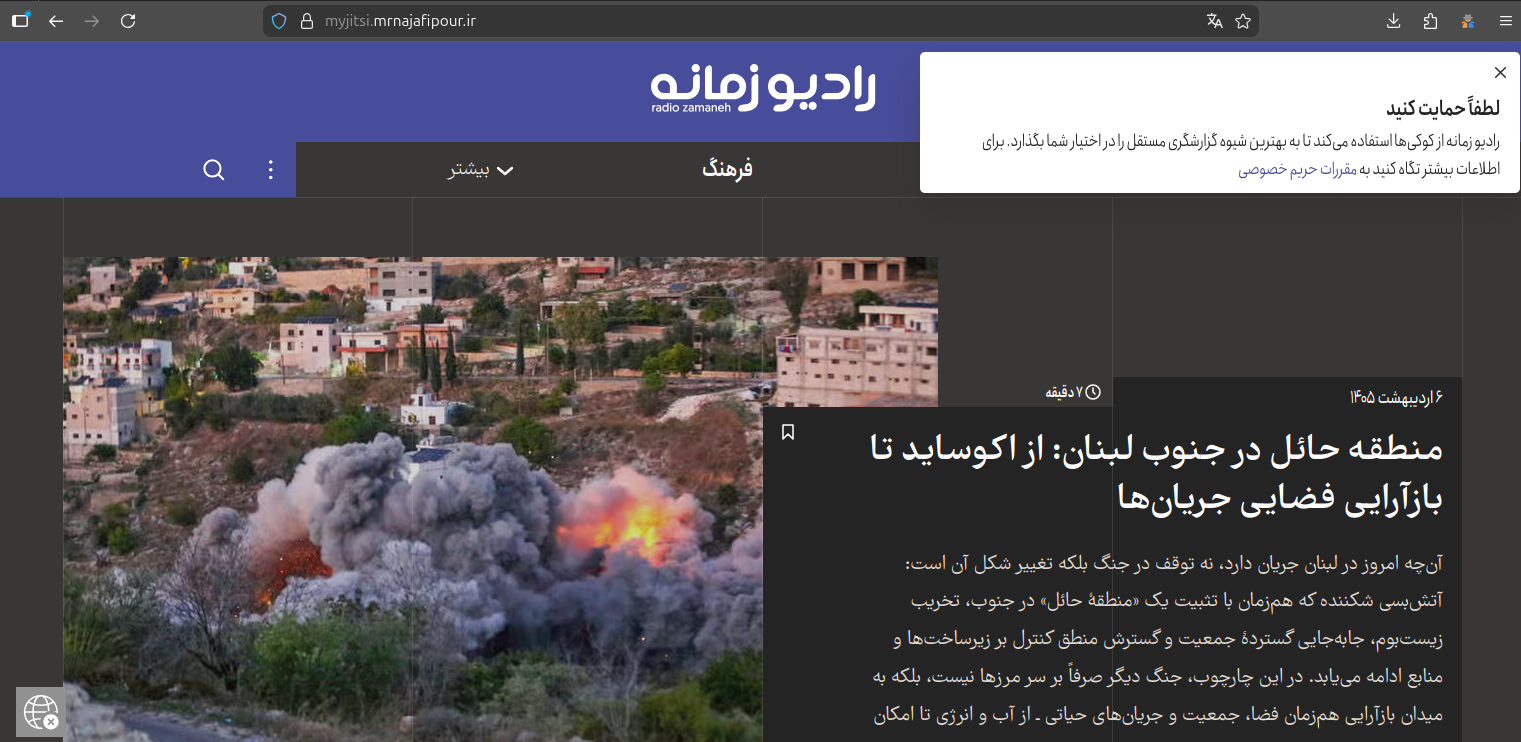
Newly identified server is a replica of Radio Zamaneh, an Amsterdam-based Persian-language media organization serving those in Iran and beyond seeking alternative journalism.
Listener ports covered SSH, multiple reverse shells, Chisel, registry exfiltration, and SOCKS5 tunneling, while a catch-all POST handler logged all inbound traffic, mixing beacon activity with external scanner noise.
Infrastructure pivoting from dubai-10.vaermb[.]com exposed a broader “dubai-#” cluster on the same RouterHosting ASN, plus a linked Swiss IP hosting cloned Iranian diaspora media and Psiphon-themed content, all consistent with Iranian state-aligned information operations and regional espionage tradecraft.
The operators attempted persistence via a scheduled task named MicrosoftEdgeUpdate, which Defender blocked, and experimented with turning off antivirus and evolving privilege escalation scripts using GodPotato and reflective loading.
While no single artifact conclusively ties this campaign to a known APT, the TTPs, targets, and infrastructure all sit firmly within the Iranian state-nexus space.
Indicators of Compromise
| Type | Indicator | Resolving Domain(s) | Hosting |
|---|---|---|---|
| IP | 172.86.76[.]101 | dubai-1.vaermb[.]com regorixa[.]com | RouterHosting LLC, UAE |
| IP | 172.86.76[.]94 | dubai-2.vaermb[.]com | RouterHosting LLC, UAE |
| IP | 172.86.76[.]108 | dubai-3.vaermb[.]com myjitsi.exceptionnotfound[.]ir | RouterHosting LLC, UAE |
| IP | 172.86.76[.]112 | dubai-4.vaermb[.]com s5.sideliner[.]ir | RouterHosting LLC, UAE |
| IP | 172.86.76[.]120 | dubai-5.vaermb[.]com | RouterHosting LLC, UAE |
| IP | 172.86.76[.]121 | dubai-6.vaermb[.]com | RouterHosting LLC, UAE |
| IP | 172.86.76[.]124 | dubai-7.vaermb[.]com suanefllix[.]com brnettlix[.]com brttfrixx[.]com realprimefix[.]com identificara[.]com | RouterHosting LLC, UAE |
| IP | 172.86.76[.]129 | dubai-8.vaermb[.]com | RouterHosting LLC, UAE |
| IP | 172.86.76[.]130 | dubai-9.vaermb[.]com | RouterHosting LLC, UAE |
| IP | 45.59.114[.]60 | shop.exceptionnotfound[.]ir price.exceptionnotfound[.]ir myjitsi.mrnajafipour[.]ir | RouterHosting LLC, CH |
| IP | 104.21.27[.]95 172.67.142[.]35 | tools.exceptionnotfound[.]ir | Cloudflare |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


