

The cybersecurity experts at Mandiant security have recently uncovered custom Android malware that was developed specifically to spy on Android devices. While this custom malware was actively used by APT42, an Iranian state-sponsored hacking group.
Here the Iranian government interests are specifically targeted by APT42’s cyberespionage activities. It was seven years ago that APT42 began to show signs of activity. This activity was centered on lengthy spear-phishing campaigns.
The following entities were targeted by those lengthy spear-phishing campaigns:-
- Government officials
- Policymakers
- Journalists
- Academics
- Iranian dissidents
Hackers are on the lookout for account credentials in order to steal them. Moreover, many of the instances involve the deployment of a custom Android malware strain as well.
APT42 Operations
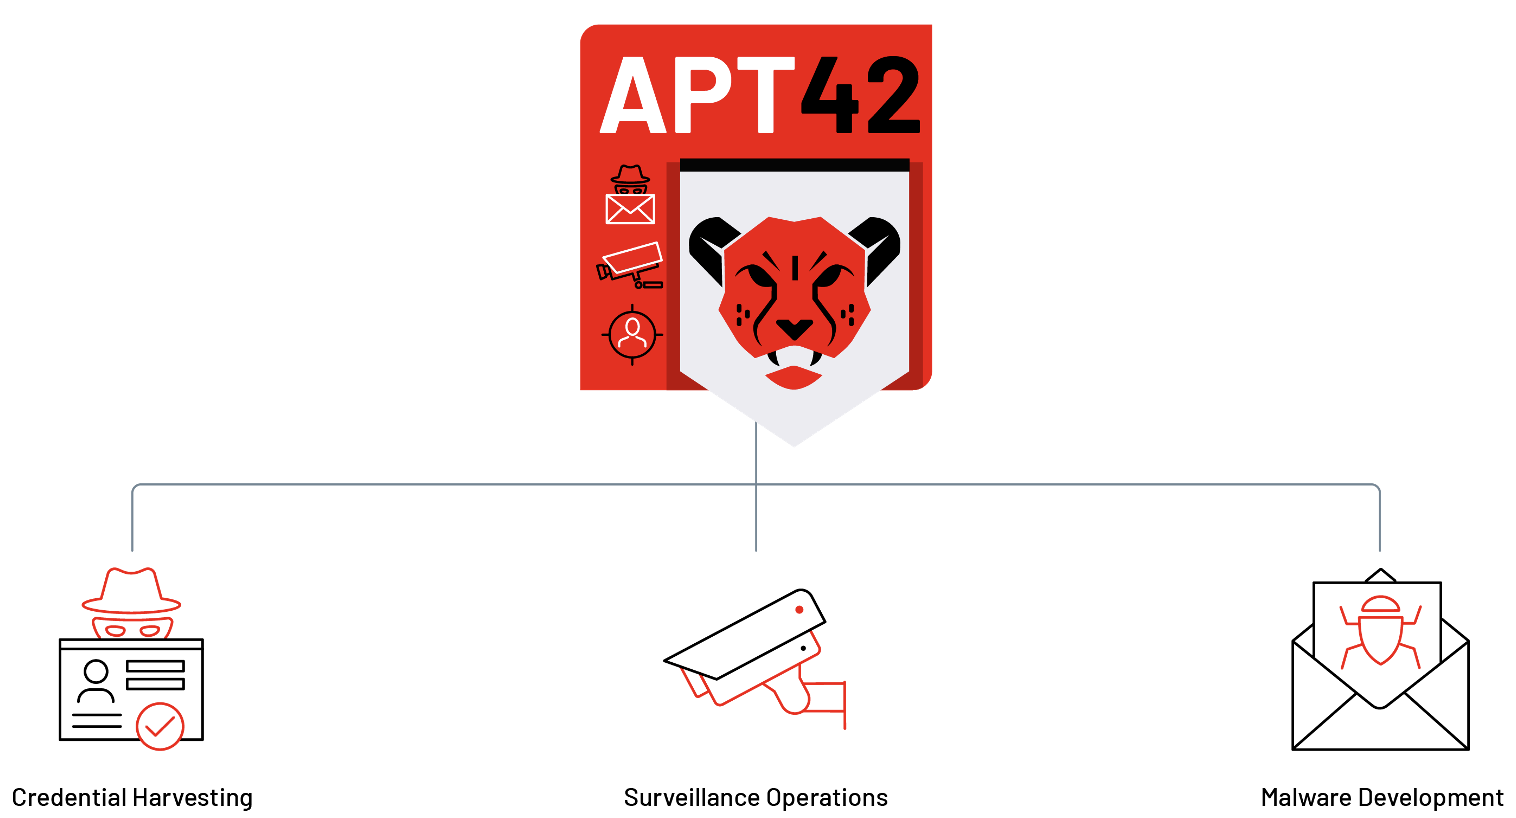
Operational activities under APT42 can broadly be categorized into three segments, and here they are mentioned below:-
- Credential harvesting
- Surveillance operations
- Malware deployment
Targets
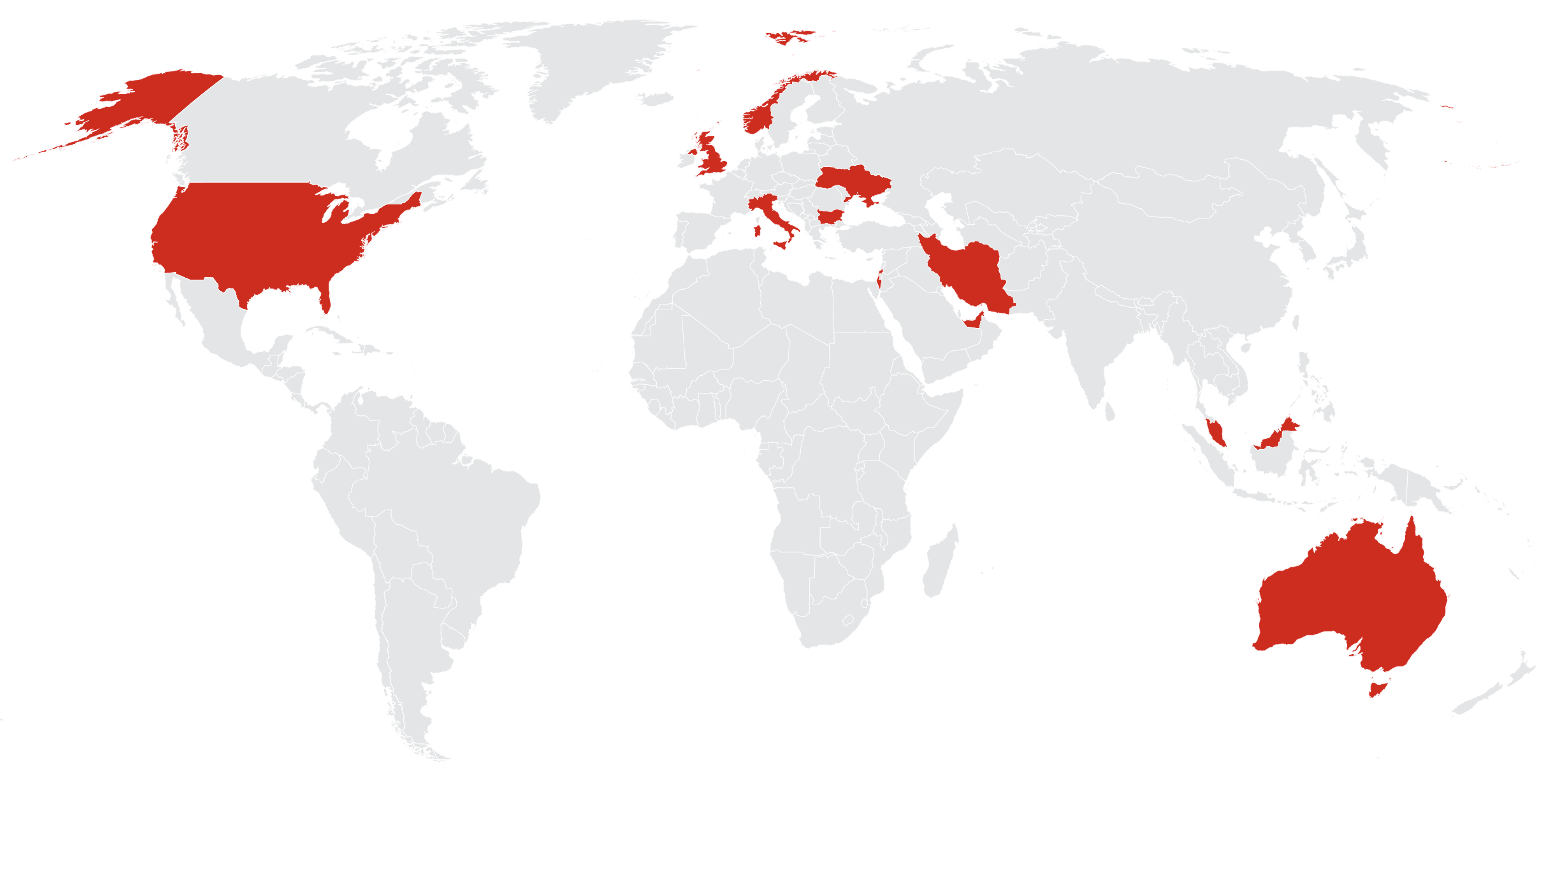
Since 2015, in 14 different countries, there have been at least 30 missions carried out by the operators of APT42. As a result of security mistakes, they have been tracked by security experts. But, the fact is that it’s only a small portion of what was revealed.
As a result of the group’s (APT42) consistent approach, the following entities have been targeted:-
- Western think tanks
- Researchers
- Journalists
- Current Western government officials
- Former Iranian government officials
- Iranian diaspora abroad
Here below we have mentioned all the industries targeted:-
- Civil society and non-profits
- Education
- Government
- Healthcare
- Legal and professional services
- Manufacturing
- Media and entertainment
- Pharmaceuticals
In order to match changing intelligence-collection interests, the group changed its targets for several times. The hacker’s primary objective was almost always to harvest credentials by redirecting their victims to phishing pages.
A shortened link is usually sent by them, or a PDF attachment containing a button that leads to a page where you can harvest the victims’ credentials.
Links Between APT42 and Ransomware
There is an association between the TTPs of APT42 and APT42’s use of BitLocker in ransomware activities. While this was reported by Microsoft in November 2021.
A further point made by Mandiant is that the clusters of intrusion activity commonly associated with APT42 and UNC2448 can be found to be related.
UNC2448 is an Iranian-based threat actor that is well known for scanning extensively for vulnerabilities as part of its activities. However, apart from this, the technical overlap between APT42 and UNC2448 has not been observed by Mandiant at this time.
According to Mandiant report, both APT42 and APT35 appear to be handles belonging to the IRGC (Islamic Revolutionary Guard Corps), with a moderate level of confidence.
It is noteworthy that the United States has designated this organization as a terrorist organization or group.







