

A series of targeted intrusions against cryptocurrency organizations, attributing the activity to a newly identified threat actor tracked as JINX-0164.
The campaign combines advanced social engineering, custom macOS malware, and deep access into development and CI/CD environments, enabling attackers to pivot from individual developer endpoints to critical software distribution systems.
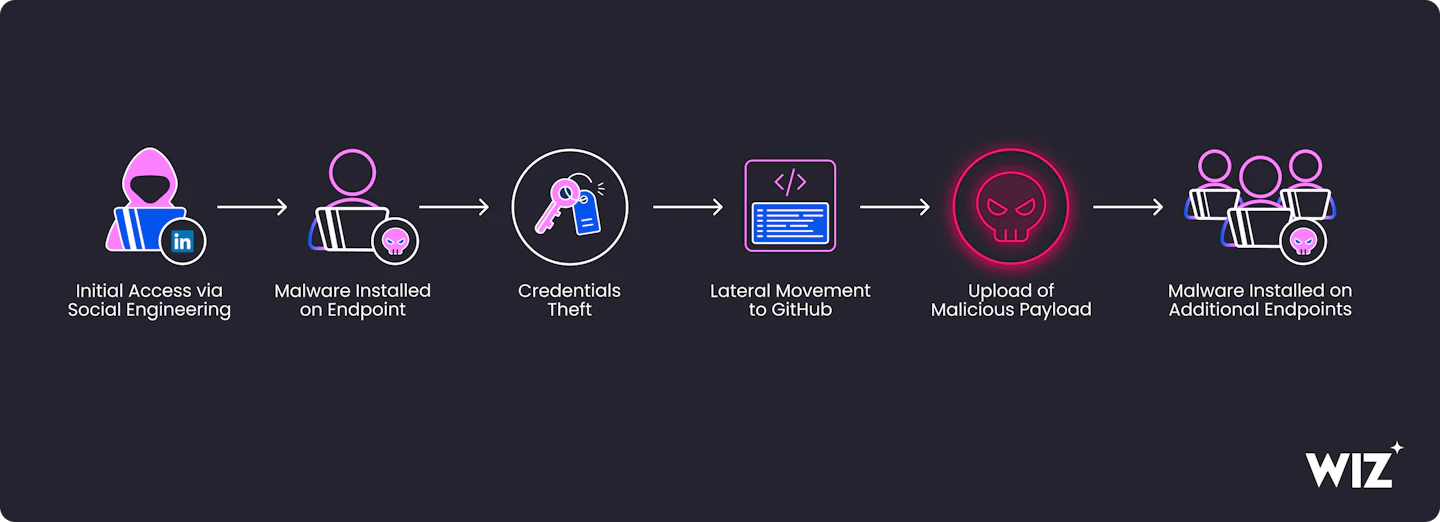
The group primarily targets developers using recruitment-themed lures, often impersonating legitimate business contacts on LinkedIn to establish trust before delivering malware.
A detailed case study from early 2026 highlights the full attack lifecycle. The intrusion began with a convincing LinkedIn outreach offering a virtual meeting.
Victims were directed to a malicious domain mimicking a conferencing platform such as Microsoft Teams. Once the victim downloaded and executed the fake client, a Python-based macOS malware known as AUDIOFIX was deployed via a bash script hosted on a spoofed Apple driver domain.
The malware, disguised as a system audio component named coreaudiod and executed through launchctl, established persistence and communicated with command-and-control servers over HTTPS.
Wiz researchers said in a report shared with GBhackers, JINX-0164 has been active since at least mid-2025 and appears financially motivated, with a strong focus on stealing cryptocurrency assets and high-value credentials.
It was capable of harvesting extensive sensitive data, including macOS Keychain credentials, browser data, SSH keys, cloud tokens, and cryptocurrency wallet information.
Evidence also shows password phishing activity, with XOR-encoded credentials stored locally on compromised systems.
JINX-0164 Targets Crypto Firms
JINX-0164 leveraged the stolen credentials to move laterally, not through traditional cloud exploitation, but by targeting internal development infrastructure.
The key indicators were the unverified badge on the malicious commits, alongside the historical affiliation of the GPG key with the compromised user, signaling a mismatch between the user who signed the commit and the listed commit author.

GitHub tokens enabled the attackers to extract secrets directly from CI/CD pipelines using tools such as nord-stream.
The threat actor then injected malicious code into repositories, often impersonating legitimate developers by modifying commit metadata or pushing directly to main branches in unprotected projects.
This approach effectively turned development environments into propagation vectors. When other developers pulled and built compromised code, additional systems were infected, expanding the attacker’s foothold.
In some cases, GitHub’s Vigilant Mode helped detect anomalies through unverified commits and mismatched signing identities.
Beyond endpoint compromise, JINX-0164 has demonstrated supply chain attack capabilities. On April 7, 2026, the group trojanized version 4.9.1 of the npm package @velora-dex/sdk.
The malicious modification injected a base64-encoded command into the package, which executed a remote script to deploy MINIRAT, a lightweight Go-based backdoor.
Unlike AUDIOFIX, MINIRAT focuses on persistence and remote command execution rather than large-scale data exfiltration.
Both malware families share overlapping infrastructure, including command-and-control domains such as datahub.ink, cloud-sync.online, and byte-io.us.
The attackers also used VPN services including Mullvad, Astrill, and ExpressVPN to obscure their activity across cloud and SaaS environments.
While JINX-0164 shares some tactical similarities with known North Korean threat clusters like UNC1069 and Sapphire Sleet, researchers found no direct infrastructure overlap, indicating a distinct and previously untracked actor.
The group’s consistent focus on macOS systems and developer-centric environments highlights a strategic shift toward exploiting software supply chains and cryptocurrency ecosystems.
Security teams are advised to closely monitor endpoint activity, audit logs, and CI/CD workflows for anomalies. Particular attention should be given to unusual VPN usage, unauthorized GitHub Actions activity, unverified commits, and suspicious package updates.
The campaign underscores the growing risk of developer-targeted attacks and the increasing convergence of social engineering, malware, and supply chain compromise in modern threat operations.
Indicators of Compromise (IOCs)
| Malware | Variant/Theme (Infrastructure) | Hash |
|---|---|---|
| MINIRAT | ARM64 | 0a8ab3d16b12d3a453ee5a3208fe04744ad54514ef8ea27bb8fe32679efad270 |
| MINIRAT | x86_64 | 0b028b781950641818800fee2b4bf68e4ef2bcee53fe71a21755275ba108783d |
| MINIRAT | ARM64 | a35d2b67fa478a7174e308b43ce30bf69b3bc6f44fa76197fdf95fc2fbc1cf5b |
| AUDIOFIX | HTTPS/ARM64 | 65cba741fe30fa4799fb9002ea8de6d96042a59159dd7c3419c766af24c835e6 |
| AUDIOFIX | HTTPS/x86_64 | 0b1a36a31b952341a534fe24890f1ed2921ee259773cff46e4f6273b8c4d5d21 |
| AUDIOFIX | Dropbox/ARM64 | e8ee6f5145c9d503c5130bfc6585567f6e19d409158c3c0ca0b259f1875b15f4 |
| AUDIOFIX | Dropbox/x86_64 | 3e3901519c2305fbe9d5483b7234c25c6d2b562512916481d96f26b849c39fdb |
| Dropper | Fake audio fix (apple.driver-store.com) | 9c2ce925133a3bf5a924063bbef8df49918d5b7258695c1894cd18c75970157a |
| Dropper | Fake audio fix (apple.driver-update.io) | 402625ec79e3573a80b6de9b33fc1e503e3c7803603cd958ddd515fb0549007c |
| Dropper | Fake audio fix (driver-updater.net) | b6cab0b3aa8e56e2427f486c74588d598ae58bb0cbc0eda6939fe171cb0aed17 |
| Dropper | Fake Chrome update (apple.driver-store.com) | d4e863f9818bfb2f1dd932df6441dff204e6142c3bdb55b298cb08dc7b6a0c62 |
| Dropper | Delivered via supply chain (89.36.224.5) | c6ef82d2864dfd26f117a1ef5602679153423f2742970a7949cec72722f0a01e |
| Dropper | Delivered via supply chain (89.36.224.5) | 2a10ffe0367bb1b26ba2c3bc600892c21074725c0b8c9dc9161e6ceb33915460 |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


