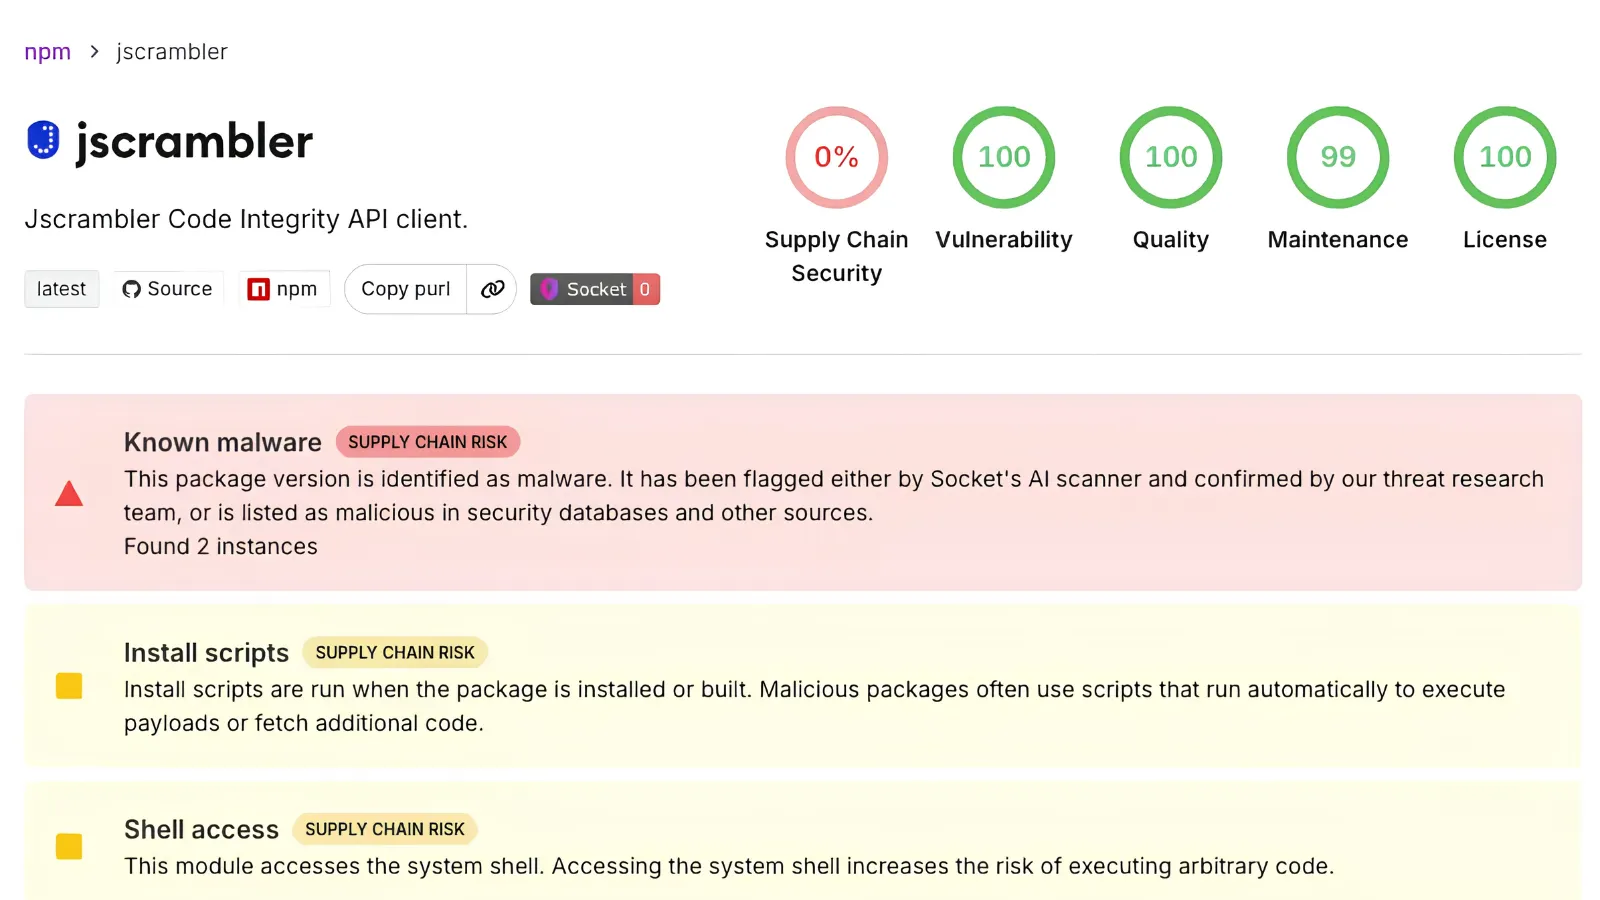

A malicious actor compromised the Jscrambler npm package and published several trojanized versions that included a hidden, cross-platform credential-stealing payload.
The attack targeted developers, build pipelines, and CI/CD systems, where npm installations could access source code, cloud credentials, deployment tokens, and sensitive environment variables.
Jscrambler npm Supply Chain Attack
Socket’s Research Team detected the initial malicious release, [email protected], within six minutes of its publication on July 11, 2026. This package receives approximately 15,800 downloads per week.
The initial version introduced an undocumented preinstall lifecycle hook that executed node dist/setup.js automatically during the npm install process. This meant that victims wouldn’t need to import the package or manually invoke the Jscrambler command-line tool for the payload to run.
The malicious loader read a disguised binary container named dist/intro.js, selected an embedded executable based on the victim’s operating system, and silently launched it from a hidden, randomly named file in the temporary directory. The container included native payloads for Linux x86-64, Windows x86-64, and Apple Silicon macOS systems.
The campaign later expanded to include Jscrambler versions 8.16.0, 8.17.0, 8.18.0, and 8.20.0. While versions 8.14.0, 8.16.0, and 8.17.0 relied on a malicious preinstall hook, later releases changed their delivery methods.
Starting with version 8.18.0, the attackers removed the install hook and injected a self-executing dropper into dist/index.js and dist/bin/jscrambler.js. The malware then executed when an application imported the dependency or ran its CLI. This method can bypass controls like npm install --ignore-scripts and scanners focused solely on lifecycle scripts.
Versions 8.18.0 and 8.20.0 also declared a self-dependency on a compromised Jscrambler release, potentially enabling transitive delivery.
The Rust-based payloads use individually encrypted ChaCha20-Poly1305 strings to conceal their configuration and detection targets. The socket recovered approximately 2,421 encrypted strings, revealing extensive data-theft functionality.
The malware targets cloud environments, including AWS, Google Cloud, and Microsoft Azure. It searches for cloud metadata-service tokens, local CLI credentials, service account files, AWS Secrets Manager data, SSM Parameter Store values, and Azure management tokens.
It also attempts to steal cryptocurrency wallet data from MetaMask, Trust Wallet, Coinbase Wallet, Phantom, and Exodus. Wallet seed phrases, recovery phrases, vault data, and key-derivation parameters are among the targeted artifacts.
Notably, the payload searches for AI coding assistant and MCP server configuration files in development tools such as Claude Desktop, Cursor, Windsurf, Factory, Zed, VS Code, and others. Such files can contain API keys, internal service URLs, and Model Context Protocol credentials.
The malware further targets browser data and applications such as Discord, Slack, Telegram, and Steam. It also examines Firefox and Chromium-based browser profiles, system keyrings, and developer secrets. Static analysis identified TLS-based exfiltration using a multipart POST /upload request.
Organizations should immediately identify installations of the affected versions, remove them, and rotate any secrets that may have been exposed to compromised developer endpoints or CI systems. This includes npm tokens, cloud keys, GitHub tokens, deployment credentials, API keys, and cryptocurrency wallet credentials.
Jscrambler confirmed the unauthorized publishing through an npm publishing credential. The company revoked and rotated the relevant credentials, deprecated the malicious versions, and released [email protected], which is considered clean. Users should upgrade to version 8.22.0 or pin to another verified safe release.
Indicators of Compromise
| IOC Type | Indicator |
|---|---|
| Malicious packages | [email protected], 8.16.0, 8.17.0, 8.18.0, 8.20.0 |
| Clean release | [email protected] |
| Malicious loader | dist/setup.js |
| Binary container | dist/intro.js |
dist/setup.js SHA-256 | a742de963f14a92d24ebcbc7b44ac867e23a20d31d1b0094a13a4f83287f4e60 |
dist/intro.js SHA-256 | a41a523ef9517aab37ed6eea0ec881821bdcb7aefcb5c5f603adc7907f868c86 |
| Linux ELF SHA-256 | fbbcf4d8f98168f78f5c0c47a9ae56d59ec8ac84a7c9ca6b797fedfb8d62d2bd |
| Windows PE SHA-256 | b7ca95d1b23c8e67416a25cedf741de0917c2096bbc9d24649eea7853d054903 |
| macOS Mach-O SHA-256 | c8fd47d36bdf7c825378593ab82ed8c24d1dc52e26b507812393e24e1d5201fd |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Interact with Cyber Threats in Windows, Linux, macOS VMs to Trigger Full Attack Chain - Analyse Malware & Phishing with ANY RUN


