

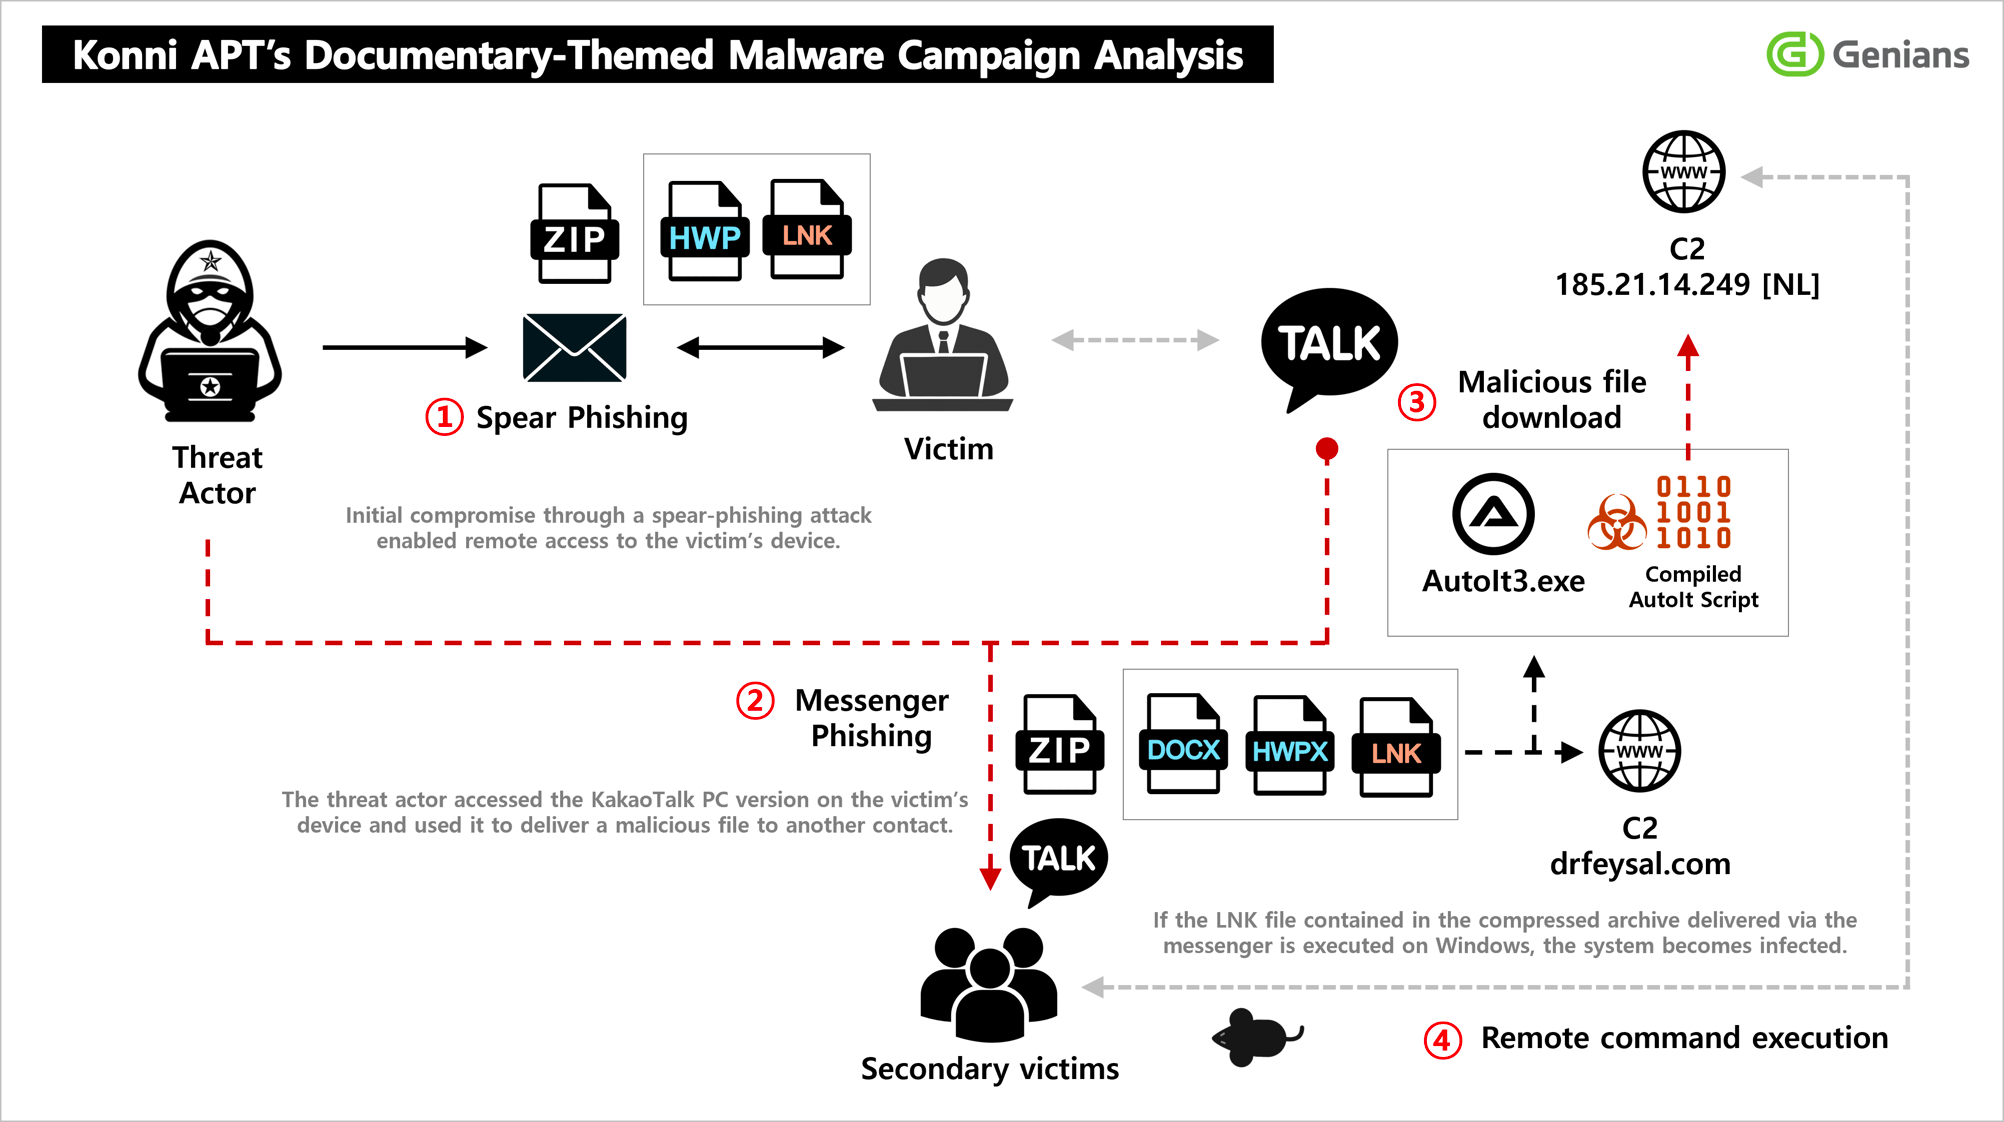
Konni APT recently ran a multi-stage malware operation that hijacked KakaoTalk accounts to spread remote access trojans (RATs) through highly targeted spear‑phishing.
The message used contextual content aligned with the victim’s role to build trust and trick them into opening an attached archive.
That archive contained a malicious LNK shortcut masquerading as a document; once executed, it launched a PowerShell-based dropper that installed remote access malware and opened a decoy PDF to avoid suspicion.
After the compromise, the Konni operator maintained long-term persistence on the endpoint, quietly exfiltrating internal documents, account details, and system information.
According to an analysis by Genians Security, the campaign began with emails purporting to be official notices appointing the recipient as a North Korean human rights lecturer.
Forensic analysis showed the attackers registering scheduled tasks and abusing common paths such as “C:\Users\Public\Videos” to drop components, helping the malware blend into normal system activity.
Over time, the infected host became a platform for both data theft and the staging of additional malware.
Hijacking KakaoTalk for Secondary Spread
A distinctive feature of this incident is Konni’s abuse of the victim’s KakaoTalk PC session to move laterally through trusted social graphs.
After gaining unauthorized access to the KakaoTalk desktop client, the threat actor selectively chose contacts from the victim’s friend list and sent them additional malicious archives containing the LNK-based loader.
Filenames and messages were crafted as North Korea–related video planning materials, leveraging topical interest and existing relationships to drive clicks.
Because these files appeared to come from known contacts over a familiar messenger, recipients were more likely to override security warnings and execute the payload.
This account‑based propagation let the campaign bypass traditional perimeter defenses that focus on email or web traffic, effectively turning each compromised user into a new distribution node.
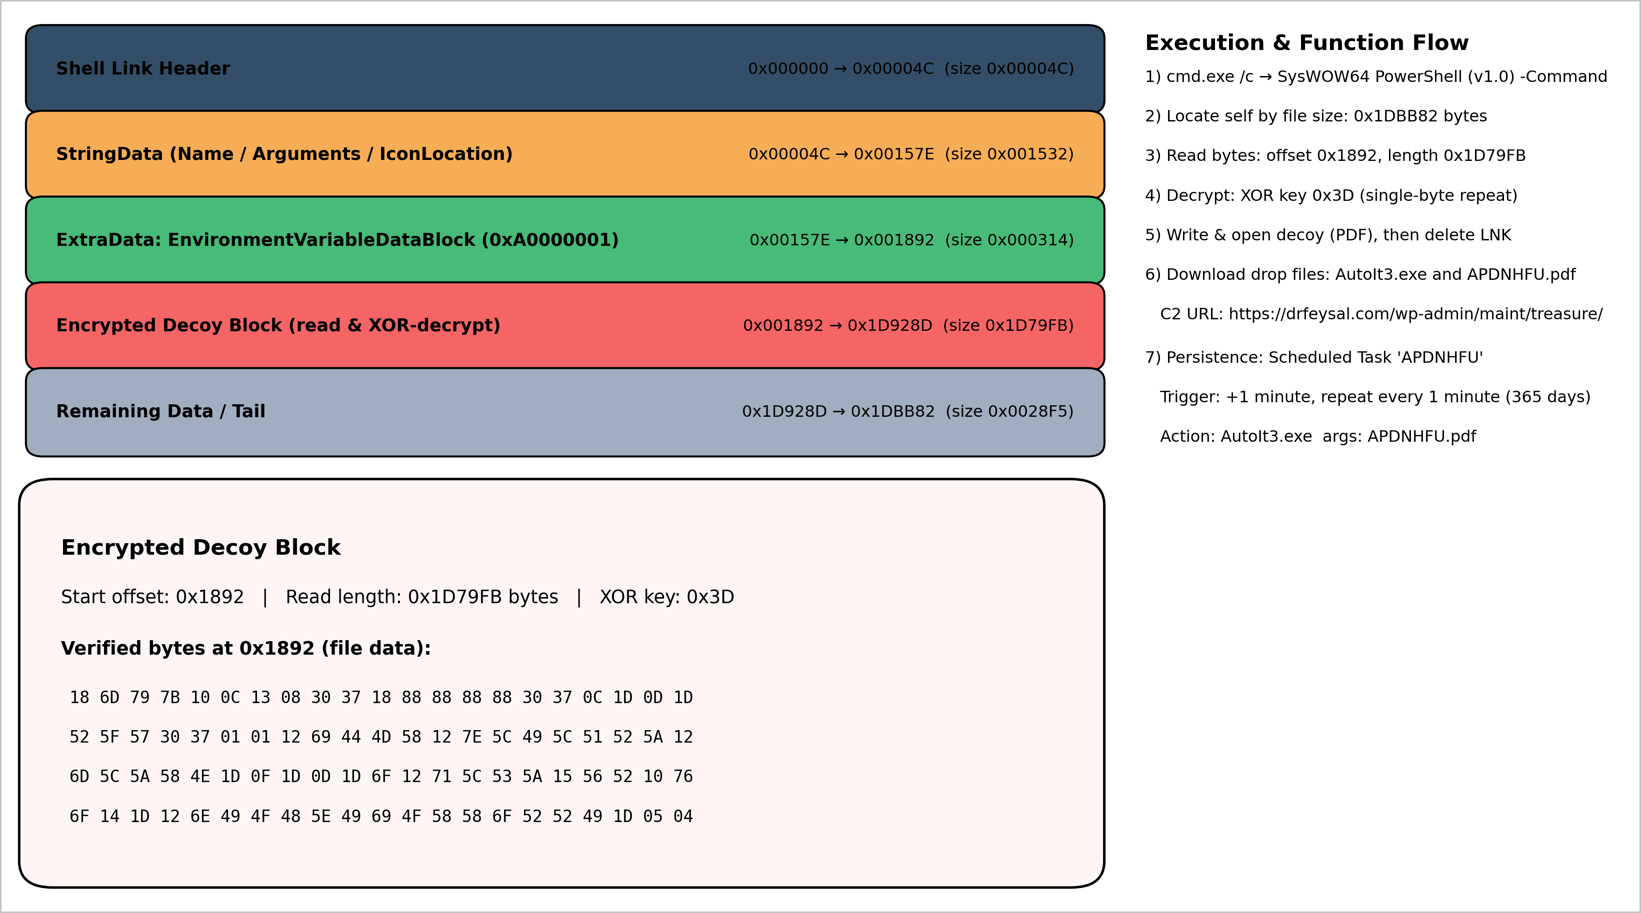
The PowerShell script first locates itself, namely the LNK file, and then identifies it by its file size. It collects a list of “*.lnk” files in the current folder and selects only the item whose “Length” value matches the specific constant “0x001DBB82”.
Genians assesses this as a multi-stage operation that goes beyond one-off spear-phishing and combines social engineering, long-term persistence, and account abuse at scale.
Under the hood, the campaign relied heavily on AutoIt-based tooling and multiple RAT families. The initial LNK dropper downloaded a legitimate AutoIt interpreter alongside a file disguised with a “.pdf” extension that actually contained an AutoIt compiled script, which then unpacked and ran the main payload.
Analysis linked the AutoIt components to several RATs, including EndRAT, RftRAT, and RemcosRAT, each contributing capabilities such as remote shell access, file management, keylogging, and additional payload delivery.
The C2 infrastructure used IP addresses distributed across several countries, including Finland, Japan, and the Netherlands, indicating a distributed backend designed for resilience and evasion.
Genians also noted overlaps with earlier Konni operations, such as Operation Poseidon and Android-focused remote‑wipe activity, reinforcing attribution to the same North Korea–linked threat cluster.
The core payload is then identified in the middle of the file. This file contains the string “AU3!EA06”, an identifier observed in AutoIt compiled scripts, which strongly indicates that the file contains AutoIt script container or bytecode data.

The modular deployment of different RATs over time suggests a managed, campaign-style framework rather than a simple commodity malware run.
Why EDR-Centric Defenses Are Critical
This incident underlines the limits of signature-only and IOC-focused defenses when facing adaptive APT campaigns.
A notable point is that the RftRAT-related infrastructure connects to the cluster of earlier Konni campaigns on the left through the Japan-based C2 server “96.62.214[.]5”.

Many of Konni’s techniques LNK abuse, AutoIt loaders, scheduled tasks, and KakaoTalk session hijacking blend into legitimate tools and user behavior, making them difficult to spot with static rules alone.
Instead, defenders need an EDR-centered approach that can correlate anomalous behaviors: suspicious LNK execution chains, PowerShell spawning from shortcuts, AutoIt processes in user-writable public paths, unusual KakaoTalk PC logins, and repeated task scheduler creation.
Organizations should also harden controls around messaging clients and social engineering: tightening macro and shortcut execution policies, monitoring messenger-originated file transfers, and training users to treat “trusted” chat attachments with the same caution as email.
As Konni continues to evolve from email-only phishing to account‑driven propagation and multi‑RAT stacks, sustained visibility into endpoint behavior and account usage will be essential to detecting and containing similar KakaoTalk-based APT activity.
IoC (Indicator of Compromise)
| Type | Value |
|---|---|
| MD5 | 148405ff05bf15a6a053e4e7c1795d40 |
| MD5 | 2e1b0ac49313873a0e0b982c591a5264 |
| MD5 | 7dc50e8af0070e544bff5299405cd3b9 |
| MD5 | 61f65bd593ea0e52ac0dfdc6bc9cd73a |
| MD5 | 461ade40b800ae80a40985594e1ac236 |
| MD5 | 01022facb38cf60b052e65a682f4a127 |
| MD5 | 3288c284561055044c489567fd630ac2 |
| C2 Domain | drfeysal[.]com |
| C2 IP | 185.21.14[.]249 |
| C2 IP | 157.180.88[.]26 |
| C2 IP | 96.62.214[.]5 |
| C2 IP | 178.16.54[.]208 |
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


 through highly targeted spear‑phishing.)