

U.S CISA recently noticed that hackers using Phishing Emails to deploy KONNNI malware with the help of weaponized Microsoft word documents.
The KONNI RAT was initially found in May 2017 by researchers at the Cisco Talos team after it was operated in attacks that are aimed at businesses linked to North Korea.
KONNI has been applied in highly targeted attacks only; these include the United Nations, UNICEF, and entities linked to North Korea. Moreover, the expert’s also classified a link between KONNI and DarkHotel.
The KONNI vulnerability is typically spread through phishing emails holding a Microsoft Word file with an ill-disposed Visual Basic Application (VBA) macro code to deploy the malware.
The CISA explains that the macro code was created to change the font color to fool the victim into allowing the content, check whether the system design is 32-bit or 64-bit.
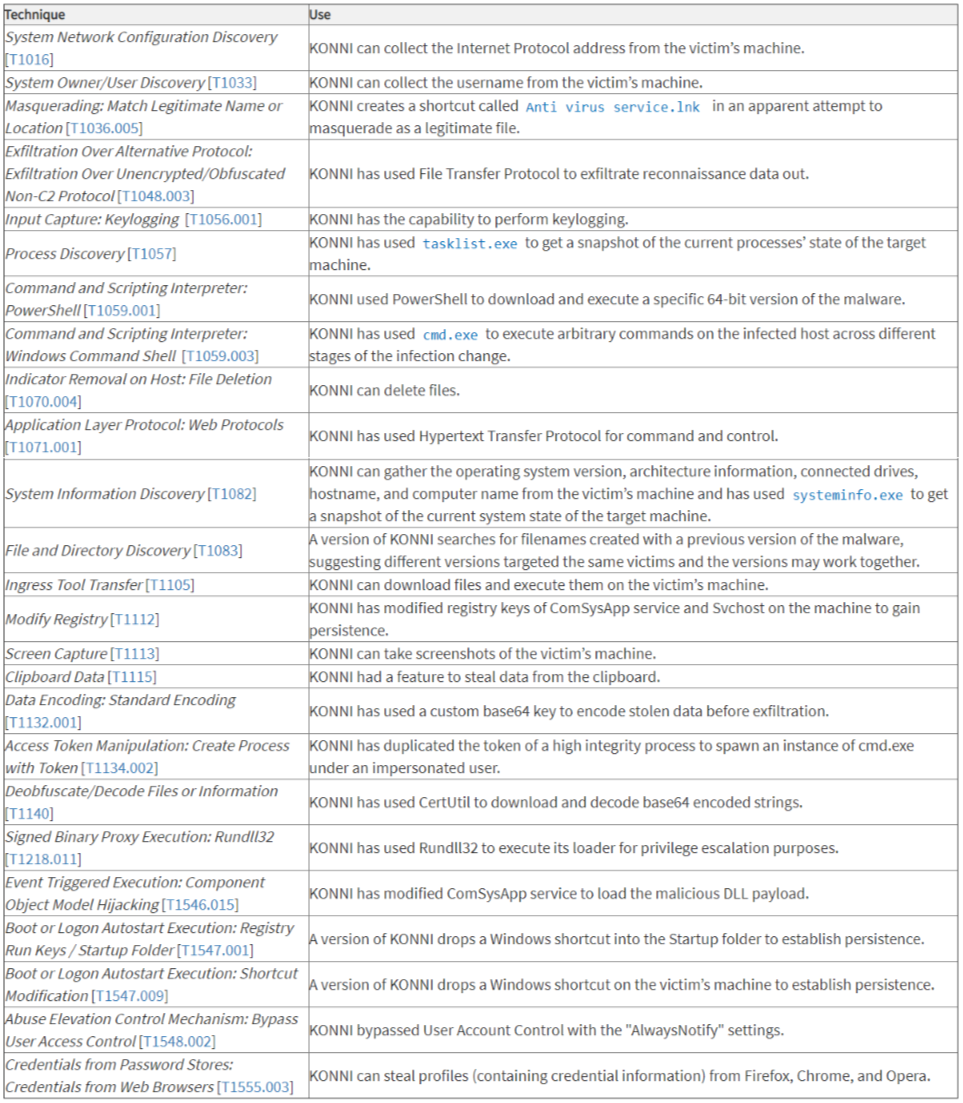
It also creates and runs a command line to download further additional files, while the certificate database tool CertUtil is applied for the download of remote files.
Techniques & Uses
Mitigations
The CISA suggested users and administrators apply the following points to increase the security aspect of their company’s network systems:-
- Remember to keep up-to-date antivirus signatures and engines.
- Always maintain your OS patches up to date.
- Impair the file and printer sharing services. In case if these services are needed, then must apply strong passwords or Active Directory authentication.
- Always restrict the users’ capability to install and run undesired software applications.
- Implement a strong password.
- Practice Caution while you are opening email attachments, even if the attachment is required, and the sender resembles to be known.
- Allow a private firewall on agency workstations, configured to reject undesirable connection requests.
- Allow additional services on agency workstations and servers.
- Always browse for and eliminate all suspicious email attachments; and assure that the scanned attachment is its “true file type.”
- Always observe the users’ web browsing habits, and restrict entrance to sites with inappropriate content.
- Practice Caution while using removable media.
- Always browse all software downloaded from the internet prior to completing it.
- Manage situational information of the latest threats and perform suitable access limitation lists.
Apart from this, the CISA suggested the users to follow the recommended mitigations carefully so that they can keep themselves protected from all unwanted malicious malware.
Moreover, the security researchers at CISA are still investigating the whole matter, and they asserted that all the users must follow every recommendation carefully.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.
Also Read;
Citrix Warns That Hackers May Exploit the New Patched Flaw Quickly
US GOV Exposes Chinese Espionage Malware “TAIDOOR” Secretly Used To For a Decade







