

A cache of leaked internal records has exposed what appears to be a structured Russian military cyber-operator pipeline embedded inside Bauman Moscow State Technical University.
The documents indicate that the university’s concealed Department No. 4 trained students for intelligence collection, offensive cyber operations, information warfare, and technical defense before moving selected graduates into GRU-linked units.
They include curricula, examination records, staffing documents, graduate lists, presentations, and placement data providing rare visibility into how Russia combines technical education with military recruitment.
Department No. 4, also called “Special Training,” operated within Bauman’s Military Training Center but was reportedly absent from the university’s public organizational structure. Its role was not limited to a conventional cybersecurity program.
The records describe a force-generation mechanism for several General Staff components, including the GRU, Main Operational Directorate, and 8th Directorate, which is associated with protected communications, cryptography, and information security.
The department trained students across three military specialties: VUS 093400, Special Intelligence Service; VUS 141600, the employment and protection of information-technical means; and VUS 751100, Information Technology Protection.
Together, the tracks covered espionage, cyber effects, defensive operations, electronic reconnaissance, secure systems, and information operations.
Reporting suggests Department No. 4 had a small but durable intake model, with roughly 10 to 15 students annually routed toward GRU assignments even before graduation.
The larger archive points to a wider ecosystem of reservists, prospective officers, military placements, and state-linked internships rather than an isolated hacking course.
Training material reviewed by journalists included password attacks, exploitation of software vulnerabilities, spearphishing, Trojan development, DDoS techniques, penetration testing, technical surveillance, and electronic reconnaissance.
The reported curriculum blended red-team and blue-team functions in a way that mirrors Russian military doctrine: operators were taught to understand, conduct, detect, and counter information-technical activity as parts of a single operational discipline.
DomainTools Researchers said that, the files, reviewed by an international consortium including The Insider, The Guardian, Le Monde, Der Spiegel, Delfi, and VSquare, span academic and administrative activity through 2025.
Leaked University Files
A 144-hour course titled “Defense Against Technical Reconnaissance” reportedly required students to conduct practical penetration-testing exercises, while a module on computer viruses culminated in programming bespoke malware.
Students also received instruction in propaganda and psychological manipulation.
One advanced practical assignment required the creation of a social-media video using “manipulation, pressure, and hidden propaganda,” demonstrating that the program treated cyber operations and influence operations as mutually reinforcing tools.
This model is operationally significant. It produces personnel capable of integrating intrusion activity, network defense, reconnaissance, disinformation, and technical intelligence into broader military planning.
The strongest concern is the documented personnel and placement overlap with GRU cyber formations.
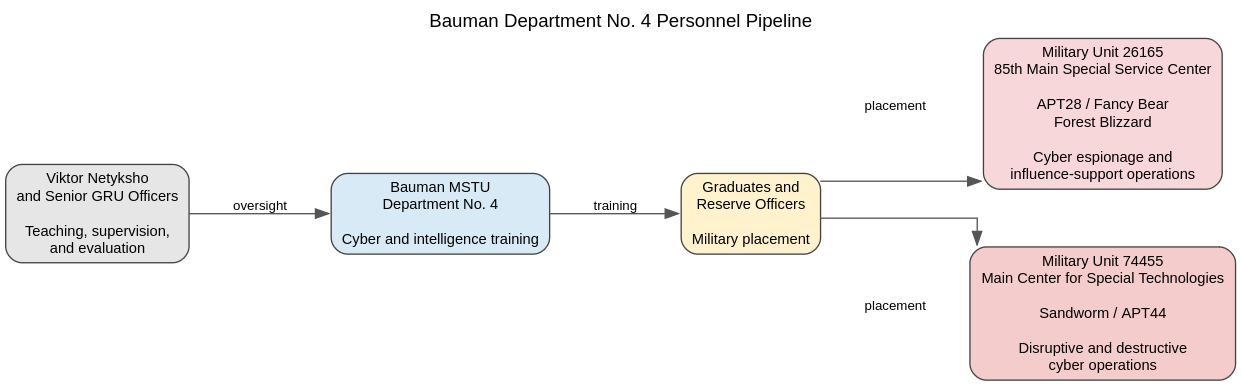
Military Unit 74455 is the GRU’s Main Center for Special Technologies, the organization associated with Sandworm, also tracked as APT44.
The leaked records reportedly identify senior officers involved in Department No. 4’s oversight, including Major General Viktor Netyksho, the former commander of Military Unit 26165.
Netyksho was among 12 GRU officers indicted by the United States in 2018 over interference in the 2016 U.S. presidential election.
Unit 26165 is publicly associated with APT28, also known as Fancy Bear, Sofacy, STRONTIUM, and Pawn Storm.
A joint CISA, NSA, FBI, and NCSC advisory assessed that APT28 is “almost certainly” the GRU’s 85th Main Special Service Center, or Military Unit 26165.
The group has been linked to espionage and reconnaissance operations, including exploitation of vulnerable Cisco routers and deployment of the Jaguar Tooth malware.
The reporting also linked a 2024 Department No. 4 graduate, Aleksei Kondrashov, to Military Unit 74455, widely known as Sandworm.
That unit has been associated with destructive cyber activity against Ukraine and other targets, including the 2017 NotPetya attack.
The reports do not establish that every listed graduate participated in a named operation; assignments should therefore be described as reported unit placements, not proof of individual operational involvement.
The Bauman material reframes Russia’s cyber capability as an institutional system, not merely a collection of well-known threat groups.
It suggests that Moscow has formalized a recurring pathway from university recruitment to military service, where students receive supervised technical and ideological preparation before entering intelligence, cyber, and security roles.
For defenders, the leak reinforces the need to track Russian operations as a combined threat: espionage, destructive activity, military reconnaissance, technical surveillance, and influence campaigns may draw on related personnel pipelines and overlapping doctrine.
The exposure of Department No. 4 also provides researchers with a clearer lens for understanding how the GRU sustains cyber capacity beyond the familiar APT28 and Sandworm brand names.
★ Which Security Tools Should You Cut? Score Them on One Page – Download the Inherited Security Stack Guide


