
A critical Local Privilege Escalation flaw has been uncovered within the Linux kernel, allowing unprivileged local users to seamlessly gain root access by manipulating the system’s page cache.
This vulnerability, designated as CVE-2026-43503, represents a severe gap in the XFRM/IPsec subsystem’s packet-processing path that bypasses earlier mitigations. By exploiting this flaw, attackers can execute a silent system compromise that leaves no kernel logs or audit traces.
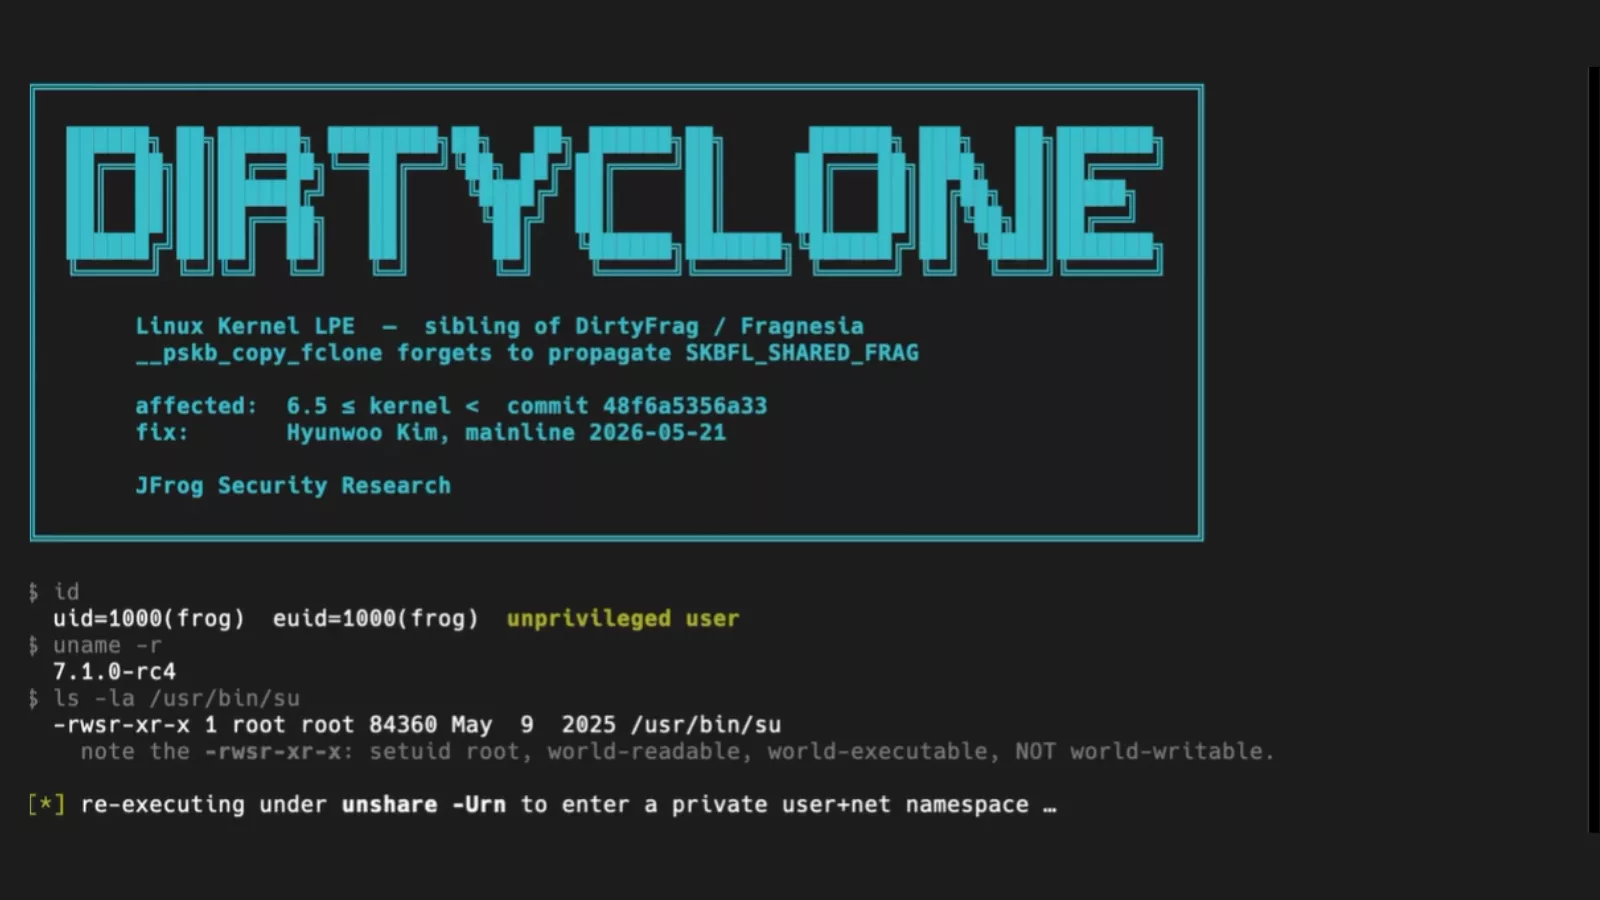
The JFrog Security Research team identified this residual issue during an extensive audit of recent kernel patches and dubbed the newly discovered variant “DirtyClone”. This vulnerability carries a high-severity CVSS score of 8.8 and requires immediate attention from system administrators.
Linux Kernel DirtyClone Vulnerability
The discovery demonstrates a broader exploitation pattern affecting multiple socket buffer processing paths, proving that the underlying attack primitive extends significantly beyond a single vulnerable code path.

The flaw stems from the broader DirtyFrag vulnerability family, which targets how socket buffers reference shared page-cache memory.
Variants such as DirtyFrag, Fragnesia, and DirtyClone all rely on a shared technique of tricking the kernel into treating read-only, file-backed page cache memory as writable network buffers.
| Vulnerability | CVE | Disclosed | Subsystem | Write Primitive | Root Required? |
|---|---|---|---|---|---|
| Copy Fail | CVE-2026-31431 | April 30, 2026 | algif_aead (AF_ALG crypto) | 4-byte page-cache write | No |
| DirtyFrag | CVE-2026-43284 / CVE-2026-43500 | May 8, 2026 | IPsec ESP (xfrm) + RxRPC | Full write primitive (chained) | No |
| Fragnesia | CVE-2026-46300 | May 14, 2026 | XFRM ESP-in-TCP | Arbitrary byte write | No |
| DirtyClone | CVE-2026-43503 | May 23, 2026 | XFRM/IPsec via netfilter TEE | Flag dropped in __pskb_copy_fclone(), triggered by TEE netfilter rule | No |
When these distinct memory contexts intersect, the kernel may inadvertently modify memory that is still semantically tied to a file, leading to the severe corruption of file-backed data directly in place.
This attack model poses the highest risk to multi-tenant cloud environments, Kubernetes clusters, and containerized workloads where user namespaces are enabled.
Any mainline, stable, or Long Term Support kernel branch that applied initial mitigations but lacks the subsequent follow-up patches remains highly vulnerable to these specific bypasses.
To execute the DirtyClone attack, a local user must hold or acquire the CAP_NET_ADMIN capability, which is frequently obtainable via unprivileged user namespaces.
The attacker begins by mapping a privileged binary, such as /usr/bin/su, causing it to be loaded directly into the host’s page cache.
Using system calls like vmsplice and splice, the kernel attaches this page-cache-backed memory into a socket buffer instead of performing a safe memory copy.
The attacker then configures a loopback-based IPsec tunnel and a netfilter rule using the TEE target to duplicate outgoing packets. This precise routing triggers nf_dup_ipv4, leading to socket buffer cloning via the __pskb_copy_fclone function.
During this cloning process, the cloned buffer fails to correctly preserve the SKBFL_SHARED_FRAG flag, which serves as the kernel’s safety marker indicating that the buffer references shared page memory.
When the cloned packet reaches the IPsec receive path for in-place decryption, the kernel writes the decrypted data directly into the file-backed page.
By controlling cryptographic parameters like the AES-CBC key, the attacker transforms this decryption routine into a controlled write primitive.
This allows the attacker to modify small instruction sequences inside the cached binary without altering the actual file on the physical disk. When the compromised binary is executed, the modified logic runs and instantly grants root privileges.
The disclosure and patching of this vulnerability unfolded rapidly over a few weeks in May 2026, avoiding a separate or prolonged exposure timeline. The initial DirtyFrag patch landed in the mainline kernel on May 4, followed by the disclosure of the Fragnesia variant on May 13.
A broader report from the original DirtyFrag researcher, Hyunwoo Kim, was submitted on May 16, detailing the remaining fragment-transfer helper gaps across the networking stack.
JFrog independently rediscovered the specific variant and reported it to Linux kernel maintainers on May 19. The comprehensive patch addressing these variants was successfully merged into the mainline kernel on May 21 under version v7.1-rc5.
Administrators are strongly advised to update their Linux kernels to this fixed version or apply backported patches immediately. If immediate patching is unfeasible, administrators should block capability acquisition by setting kernel.unprivileged_userns_clone=0 to effectively mitigate the threat.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.