

Researchers have found a new, malicious Linux agent that hides as a system process on e-commerce servers. This new malicious Linux agent name is linux_avp, and it’s been discovered to be hiding in operating systems.
This malware uses a multi-stage attack that employs a backdoored library to obtain a malicious file from a remote location. The malware was created to inject JavaScript into pages and obtain customer information, such as:-
- Login IDs
- Passwords
Malicious Golang-based malware agent
This kind of malicious agent had a very high success rate and enables the attacker to distinguish a specific vulnerability affecting these platforms. The attacker then took steps to exploit these vulnerabilities.
However, the most interesting part is that the threat actors have uploaded a Linux executable called linux_avp. Here, to remove itself from the disk and masquerade as a fake ps -ef process this Golang program starts.
The interpretation of linux_avp reveals that it has the potential to act as a backdoor, waiting for the commands from a Beijing (Alibaba) hosted server 47.113.202.35, and not only that even the function list of this malware also contains the spelling error “PostDecript.”
Malware spreading
The malware was uploaded to Virustotal, an online virus-scanning service, on October 8th by an individual who left the comment “test” in the file’s comments.
However, it is not unusual for anti-virus vendors to miss a ransomware variant or two, but due to the level of sophistication in the encryption, the anti-virus vendors have not recognized this malware.
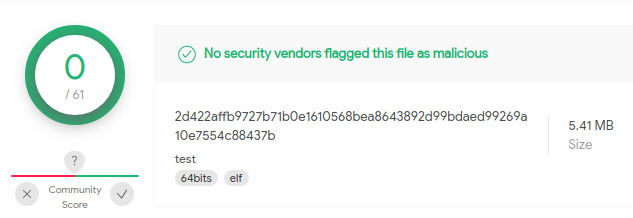
According to the report, “While it’s been assumed that the person who uploaded the malware to the customer’s store is surely the malware author, who thought that common anti-virus engines would not identify their creation.”
Here, the E-commerce sites seem to be particularly targeted during the holiday season, so it’s necessary on these sites to monitor and search out for potential attacks.
Moreover, the retailers need to defend their customers by having a plan in place to recognize and mitigate these kinds of potential risks.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity, and hacking news updates.







