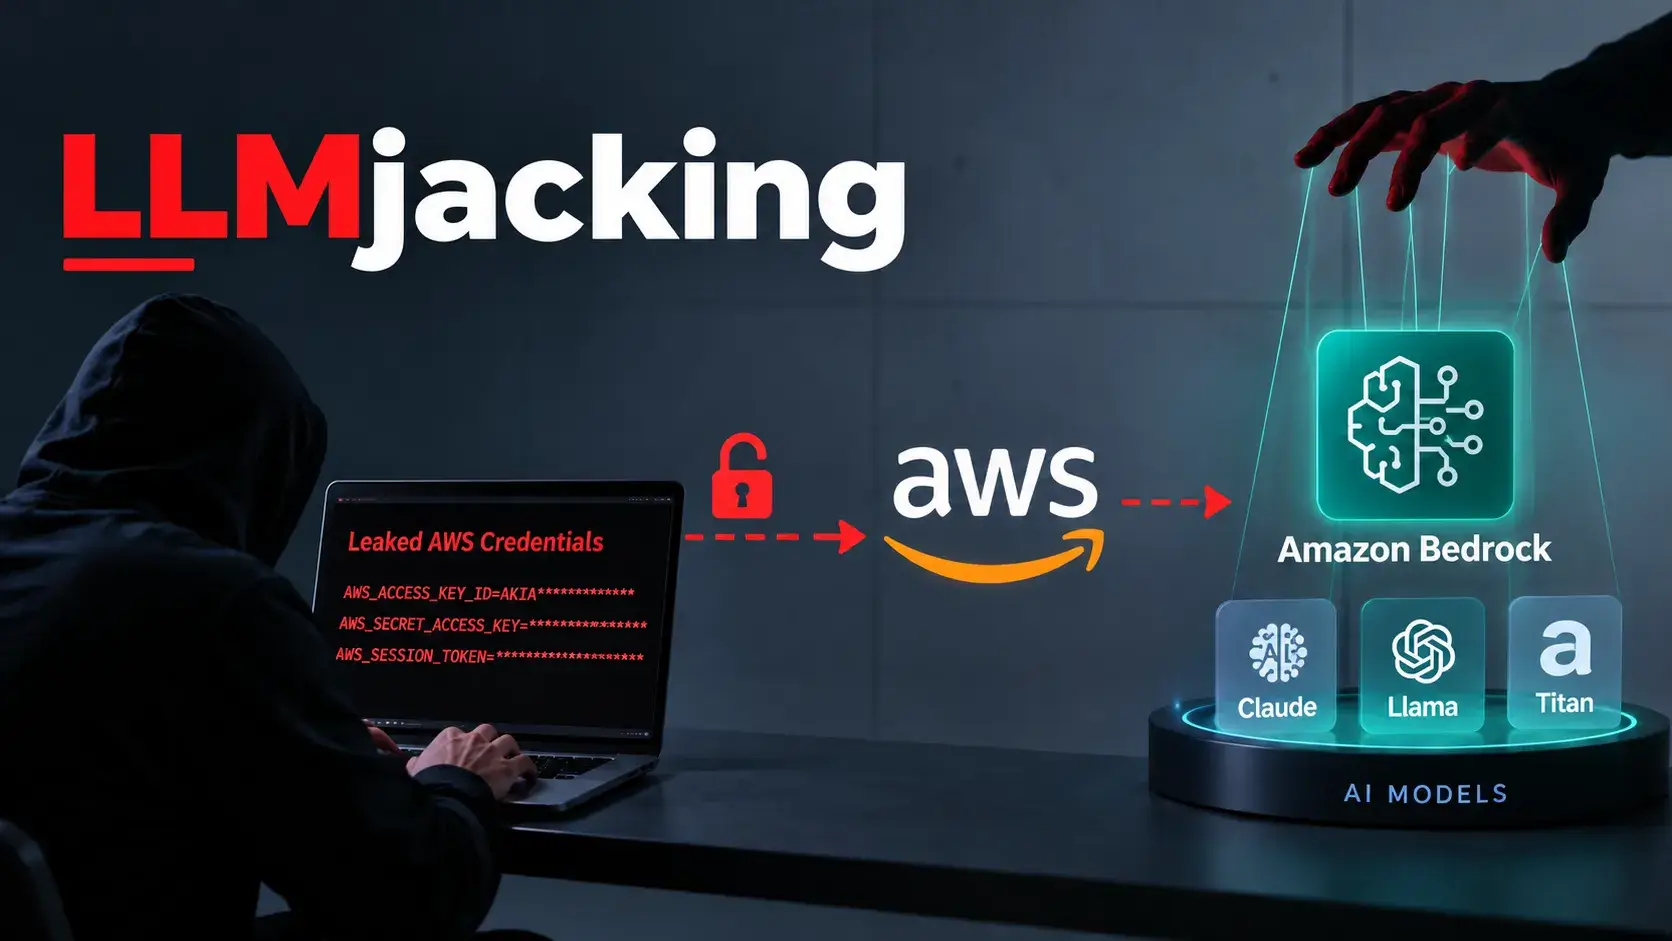

Threat actors are increasingly converting stolen cloud credentials into access to costly generative AI services, a technique known as LLMjacking.
FortiGuard Labs reported an incident involving Amazon Bedrock in which a leaked, long-lived AWS IAM access key with AdministratorAccess permissions was used to create a new identity, subscribe to foundation models, and run inference at the victim’s expense.
LLMjacking Attack
Unlike data theft or cryptomining, LLMjacking targets a cloud customer’s ability to invoke hosted models. The attacker does not need to steal model weights, training data, or a proprietary application.
Instead, they use valid credentials to make the victim’s account incur charges for premium inference, either for their own operations or for resale through illicit AI chatbot services.
Fortinet explained that the observed intrusion began with an administrator-level IAM key that had no expiry. The attacker created a new IAM user and then utilized AWS Marketplace agreement actions, including CreateAgreementRequest and AcceptAgreementRequest, to subscribe to one or more foundation models. The newly activated models were invoked, generating charges for the compromised AWS account.
Attackers may also create or reset service-specific credentials for Bedrock, which differ from conventional IAM access keys and can provide a long-term means of accessing the model APIs.
This makes the operation particularly difficult to detect: an Amazon Bedrock InvokeModel request generated by a compromised identity can appear legitimate since it relies on permitted APIs and authenticated credentials.
The financial consequences can escalate quickly. Fortinet cited prior LLM-jacking research estimating daily victim exposure at over $46,000 for Claude 2.x-class inference, rising to more than $100,000 per day for Claude 3 Opus-class usage at scale.

This appeal has turned exposed CI/CD secrets, local credentials, and IAM keys into a direct means of accessing monetizable cloud resources.
Defenders should treat long-lived, broadly privileged IAM keys as tier-0 risks and transition workloads to short-lived, role-assumed credentials whenever possible.
AWS CloudTrail should be enabled across all accounts to help reconstruct identity creation, credential issuance, Marketplace activity, and model access.
Additionally, Bedrock invocation logging, which is turned off by default, provides request-level visibility that CloudTrail alone may not capture.
Security teams should also avoid considering first-time Bedrock activity as conclusive evidence of compromise. Fortinet recommends correlating new model usage with secondary signals, such as unfamiliar source IP addresses, recently created IAM identities, access-denied events, or unusual credential creation behaviors.
The vendor highlighted several detections relevant to this attack path. These include alerts for IAM policy changes, newly created AWS users, changes to IAM access keys, creation or resets of service-specific credentials, Marketplace agreement creation or acceptance, deletion of Bedrock invocation logs, and Bedrock throttling exceptions.
Organizations utilizing Bedrock should also implement posture policies to identify disabled invocation logging and other risky configurations.
This incident illustrates a shift in the economics of cloud abuse. Valid credentials can now be exploited not only to access data or compute resources but also to consume and potentially resell AI capabilities.
Therefore, monitoring identity changes alongside billing-linked AI activity is essential for detecting LLMjacking before inference costs escalate and operational disruptions spread across the enterprise.
Keep your SOC up to date on active malware & phishing within 24h of their emergence. Try ANYRUN to prevent incidents with early detection.


