

LockBit 5.0 affiliate panel provide unprecedented visibility into the infrastructure of one of the world’s most notorious ransomware-as-a-service (RaaS) operations.
Following the high-profile Operation Cronos disruption, security researchers have confirmed that LockBit has largely maintained its core operational procedures.
However, cosmetic updates including holiday-themed interface elements suggest active development and continued operations.
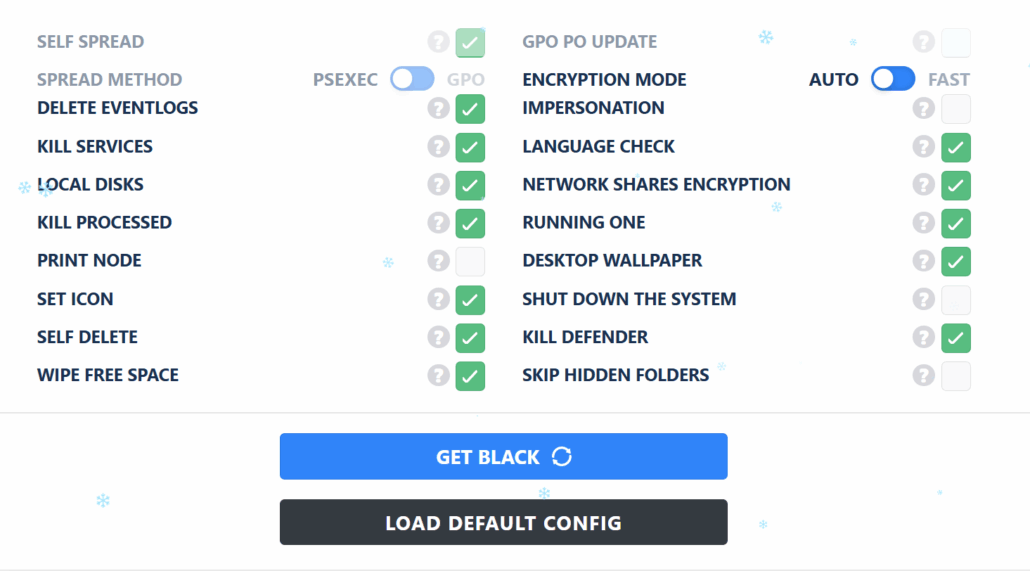
The leaked materials expose the backend infrastructure that LockBit affiliates use to coordinate ransomware attacks and manage victim negotiations.
Screenshots obtained by researchers show a sophisticated dashboard designed for managing multiple attack campaigns simultaneously.
The interface includes options for affiliate onboarding, payment structure negotiations, and attack coordination protocols.
Exclusive analysis from Senior CTI Analyst Arda Büyükkaya and IR Analyst Matthew Maynard reveals the group’s resilience despite significant law enforcement pressure.
Notably, the system displays minimal changes from previous versions, indicating that LockBit has adopted a “business as usual” approach following the Operation Cronos takedown.
The holiday-themed cosmetic updates suggest that the group’s developers are actively maintaining and incrementally updating the platform.
Multi-Platform Encryption Variants
Cybersecurity analysts have identified four new LockBit 5.0 variants released on January 14th, 2026, each targeting specific operating systems and virtualization environments:
- LB_Black_14_01_2026 – Traditional Windows-focused variant.
- LB_Linux_14_01_2026 – Linux encryption module.
- LB_ESXi_14_01_2026 – VMware ESXi hypervisor targeting.
- LB_ChuongDong_14_01_2026 – Specialized deployment variant.
This diversification strategy allows LockBit affiliates to compromise diverse infrastructure environments, from traditional enterprise networks to cloud-based and virtualized systems.
Despite maintaining operational capabilities, intelligence gathered from compromised communications indicates that LockBit’s reputation within the cybercriminal community has significantly deteriorated.
Many affiliates express reluctance to work with the group due to law enforcement actions and previous panel breaches.
However, LockBit leadership continues operating as though no disruption has occurred, aggressively recruiting new affiliates and maintaining payment infrastructure.
This disconnect between affiliate sentiment and operational posture suggests the group is prioritizing market share retention over rebuilding trust.
Implications for Security Teams
Continuous threat exposure management solutions that automatically scan dark web communities and threat actor forums provide valuable early warning capabilities for emerging variants and attack methodologies.
Organizations should treat these new variants as critical threats. Security teams should immediately implement detection signatures for the four new LockBit 5.0 samples and prioritize EDR (Endpoint Detection and Response) alerts for suspicious encryption behavior across all platforms.
The shift toward multi-platform targeting indicates that LockBit is expanding beyond traditional Windows environments to exploit organizations using Linux and hypervisor-based infrastructure.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


 operations.)