

Two critical vulnerabilities (CVE-2024-31204 and CVE-2024-30270) affecting Mailcow versions before 2024-04 allow attackers to execute arbitrary code on the server.
An attacker can exploit these vulnerabilities by sending a specially crafted email to an administrator.
When the administrator views the email while logged into the admin panel, the attacker can inject malicious scripts and gain complete control of the server.
Scan Your Business Email Inbox to Find Advanced Email Threats - Try AI-Powered Free Threat Scan
Mailcow’s admin panel in PHP uses a custom exception handler to store error messages in the user session, which are then retrieved and displayed in an alert box on the next page load.

The process involves parsing the session data, injecting the error messages into a JavaScript function call within a template, and finally rendering an alert box using a JavaScript library upon receiving the message in the browser.
It creates a vulnerability because the error messages are not sanitized before being displayed, potentially allowing attackers to inject malicious scripts.
CVE-2024-31204 is an XSS vulnerability in MailCow’s admin panel that exists because the jQuery-based notification library doesn’t escape HTML entities properly, allowing attackers to inject malicious scripts by controlling the content of an exception being raised.

The attacker can achieve this because the exception handler uses print_r() to include function call stack arguments in the error message, which bypasses Twig’s escaping mechanism.
By sending a malicious email with a background image that references the vulnerable API endpoint with a specially crafted URL, an attacker can exploit the explode() function in json_api.php by providing an array as input through a crafted query string.
The email client, bypassing restrictions due to the relative URL, executes the script embedded in the query string, injecting an XSS payload into the victim’s session for exploitation upon their next visit to the admin panel.
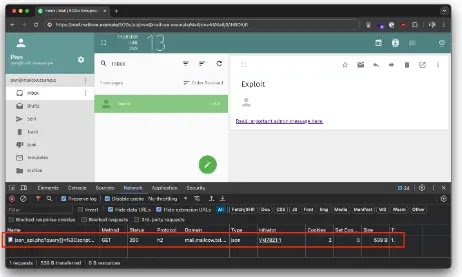
SonarCloud discovered a vulnerability (CVE-2024-30270) in MailCow’s rspamd_maps function that allows an attacker to overwrite arbitrary files, stems from insufficient validation of user-supplied input, which can lead to an attacker crafting a path traversal payload to overwrite system files.
While this vulnerability can’t be used for arbitrary file creation due to existence checks, an attacker could overwrite critical PHP files with malicious code to compromise the server.
An attacker can exploit a writable template cache directory in Mailcow’s Twig templating engine, and by overwriting a compiled template file with malicious code, the attacker can execute arbitrary commands when the corresponding page is accessed.

While Mailcow’s disabled PHP functions mitigate this, the mail() function remains enabled, allowing attackers to craft emails with multi-stage payloads to bypass these restrictions and execute commands on the server.
The mailcow maintainers addressed the XSS vulnerability (CVE-2024-31204) by encoding all HTML special characters in exception details before rendering them in the template.
For the file path vulnerability (CVE-2024-30270), they strengthened the validation logic to ensure only allowed map types are used.
Additionally, they implemented new security measures to prevent similar attacks in the future by adding checks to differentiate between API requests and normal web requests by looking for specific headers sent by browsers, such as the Referer header and the Sec-Fetch-Dest header.
Free Webinar! 3 Security Trends to Maximize MSP Growth -> Register For Free





 affecting Mailcow versions before 2024-04 allow attackers to execute)