

Several recently discovered malicious apps on Google Play have been found to display intrusive advertisements to users, with a total of over 2 million installations. These trojans attempt to hide themselves from users of Android smartphones after being installed.
According to detection statistics collected by Dr.Web for Android, the following trojans were detected, such as:
- FakeApp trojan app – Employed in various fraudulent schemes
- Joker Trojans – Force users to subscribe to paid services
- HiddenAds – Display annoying ads
New Malicious Apps On Google Play
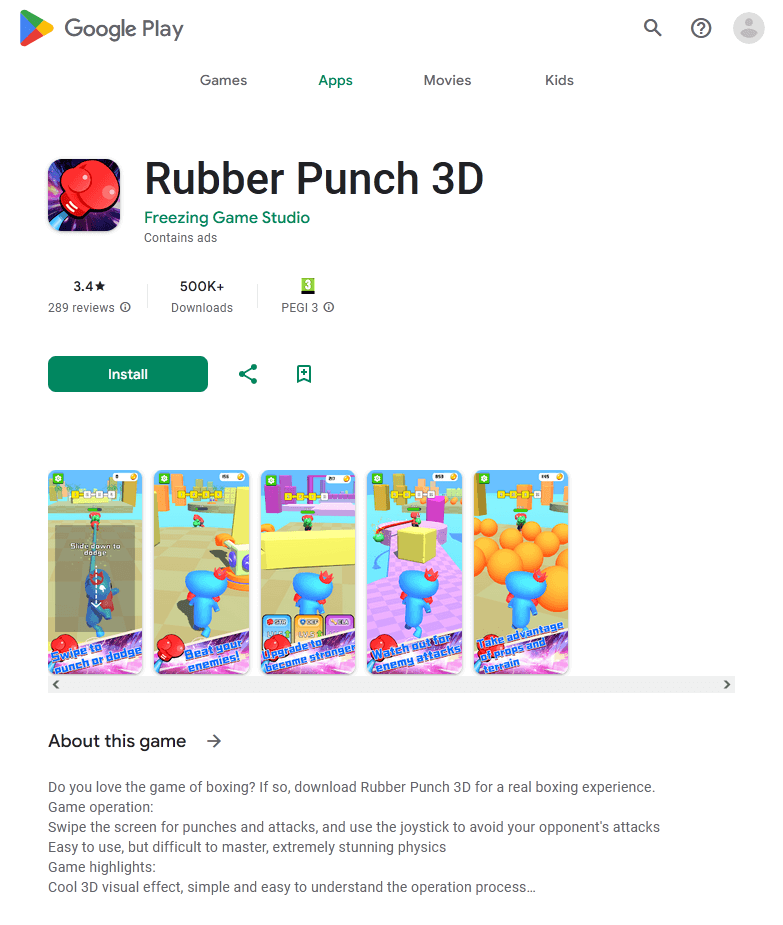
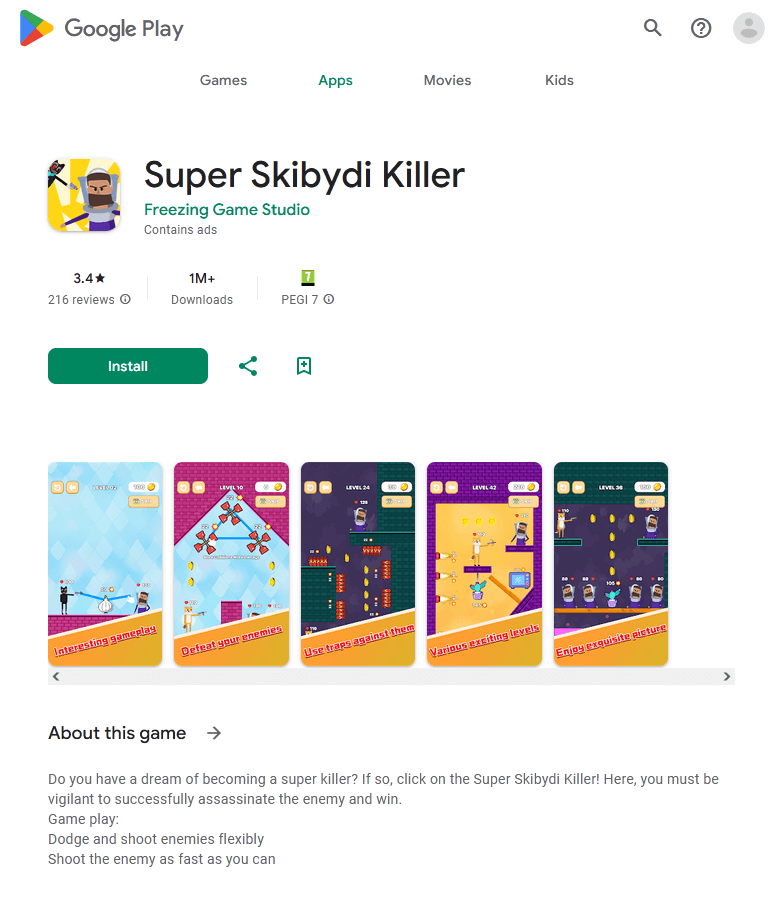
Threat actors are disseminated in the form of games like Agent Shooter, Rainbow Stretch, Rubber Punch 3D, and Super Skibydi Killer via HiddenAds Trojans. After being installed on Android smartphones, these trojans attempted to conceal themselves from users.
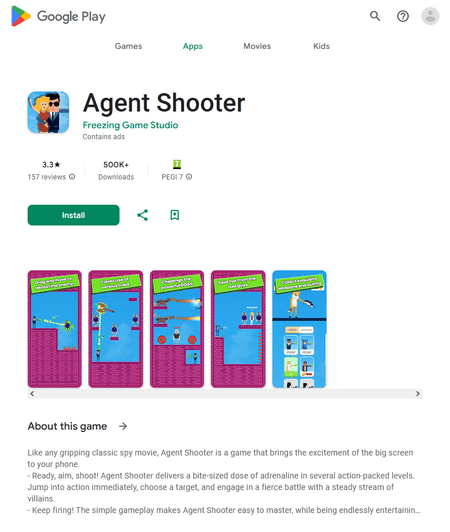
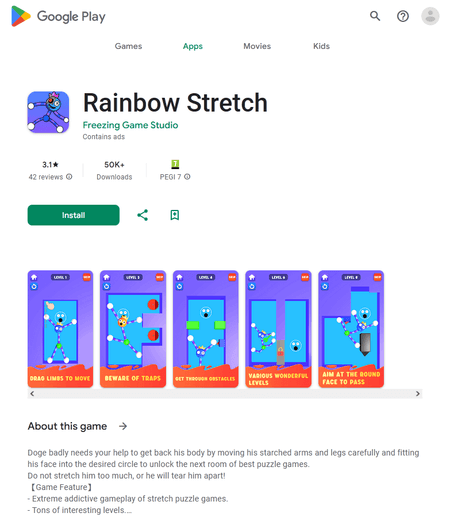
“They replaced their icons, located on the home screen menu, with transparent versions and also changed their names so they were left blank,” according to Dr. Web’s report.
They may even replace their icons with the matching replica to make it appear like they were using Google Chrome. When users tap on such an icon, these trojans start the browser and keep running in the background.
This reduces the chance that they may be removed too soon and makes them less noticeable. Furthermore, if these malicious applications fail to function, users will restart them, believing they are starting a browser.
Under the FakeApp family, other fake apps are distributed as financial software, such as apps for stock trading, guides and reference books, home accounting, etc.
“Their primary objective was to load fraudulent sites where potential victims were encouraged to become “investors,” reads the report.
Further, cybercriminals have used other fake applications to pose as various gaming apps. These may work as games in some situations, but their primary purpose was to load online casino websites.
Here are a few apps: Eternal Maze with 50k+ installs, Jungle Jewels with 10k+ installs, Steller Secrets with 10k+ installs, Fire Fruits with 10k+ installs, and much more.
One of the Joker family was disseminated as Love Emoji Messenger, an internet messenger, while another one was disguised as the image-collecting app called Beauty Wallpaper HD.
Please pay attention to reviews and ensure your Android phone has an antivirus installed to shield it against viruses and malicious apps.
Protect yourself from vulnerabilities using Patch Manager Plus to patch over 850 third-party applications quickly. Try a free trial to ensure 100% security.


-1.webp?fit=1600,900&ssl=1&description=On Google Play, several new malicious apps with over 2 million installations have been found to display intrusive advertisements to users.)