

In the past two years alone, more than 7 million users have endeavored to install malicious browser extensions on their systems. While the majority of these extensions are used by the threat actors as an adware to display advertisements to users.
As of 2022, malicious extensions for web browsers were most commonly used by adware families to execute the most common activities:-
- Surveillance of browsing activities
- Promotion of affiliate links
Kaspersky collected telemetry data, which was used to make this conclusion based on its analysis.
During H1 ’22, over 1,300,000 malicious extensions have been attempted to be installed by users, which is an increase in comparison to last year’s figures.
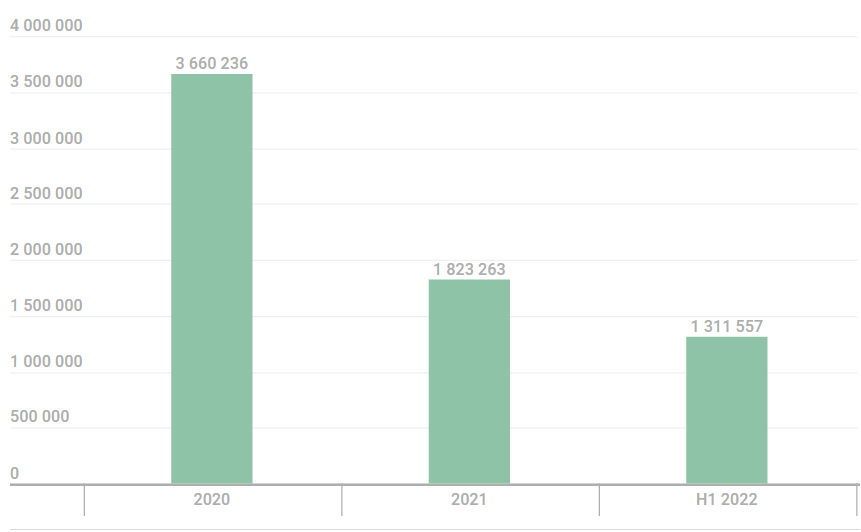
Kaspersky records that 4.3 million unique users have been targeted by adware extensions from January 2020 to June 2022. In comparison to any other delivery mechanism, the amount of adware that is delivered through malicious extensions is tremendously large.
Major Threats in 2022
Over 876,924 users were targeted by the malicious extension related to WebSearch this year. This type of software emulates productivity tools such as DOC to PDF converters and utility programs that merge documents.
In order to create a profile of the user based on their interests, WebSearch monitors the users’ browsing activities. It is then used in affiliate marketing programs in order to promote links that are used to monetize the infection so that it can be profitable.
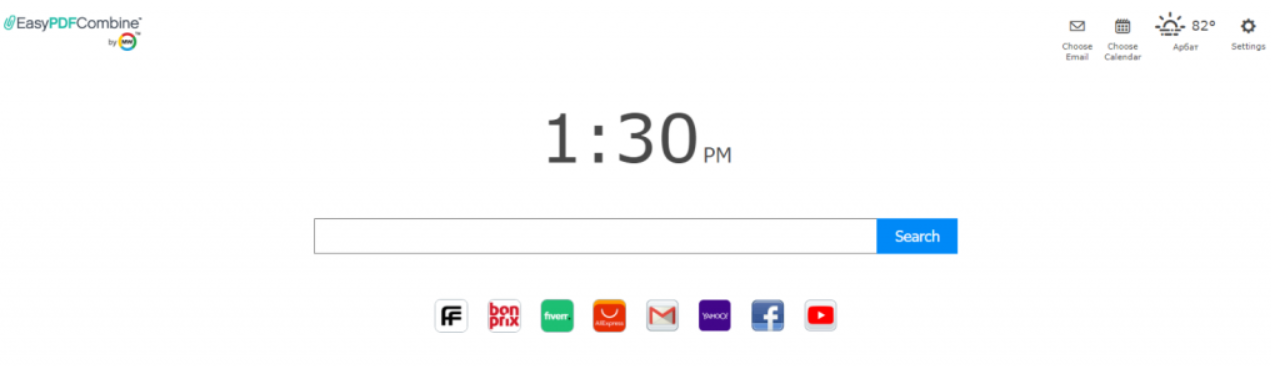
The WebSearch extension generates funds from AliExpress or Farfetch by replacing the browser’s home page.
Among the other adware hiding in scripts used by browser extensions, AddScript is the second most common one. A total of 156,698 unique users were targeted in the attacks from the AddScript extension.
In the background, AddScript runs covertly with a unique feature that you can execute without being noticed:-
- Downloading videos from the web
In order to increase ad revenue, the malware runs YouTube videos in the background using JavaScript fetched after installation and logs “views” on YouTube channels, thus making money off of ads that appear on YouTube.
Among all adware programs, DealPly ranks third in popularity. The first half of the year has seen 97,525 attempts to cause infection through this malware.
Typically, this adware has its origins in the execution of pirated software such as:
- KMS activators
- Game cheat trainers
Downloading these tools from shady websites or peer-to-peer networks is a common method of spreading malware.
There is also an option to have DealPly change the home page of the browser, promoting affiliate sites based on the search queries the user has entered.
Recommendation
In order to prevent your browser from becoming infected with adware, follow these things:-
- Visit the official web store of your browser to download extensions.
- Analyze the comments made by users.
- Analyze the reviews properly.
- Make sure the developer/publisher has a clean record.
- It is important to review their privacy policies and how they collect data.
- Keep the number of extensions to a minimum.
- Ensure that the installed extensions are reviewed on a periodic basis.
Sponsored: Secure Microsoft Office 365 with Perimeter 81 and Azure AD Conditional Access


