Malicious NuGet packages are quietly stealing browser credentials, SSH keys, and cryptocurrency wallet data from developer machines and CI/CD infrastructure, with a particular focus on Chinese .NET ecosystems.
The campaign blends legitimate-looking UI and infrastructure libraries with a heavily protected infostealer payload, making it hard for developers and traditional security tools to spot.
Packages IR.DantUI, IR.OscarUI, IR.Infrastructure.Core, IR.Infrastructure.DataService.Core, and IR.iplus32 wrap real functional code but embed a .NET Reactor–protected infostealer.
These libraries target environments where developers routinely consume Chinese WinForms components and internal-style infrastructure packages, making the names look plausible inside corporate dependency graphs.
Across 224 versions, of which 219 are deliberately hidden (listed: false), the packages have amassed roughly 65,000 downloads since late 2025.
Socket’s Threat Research Team has identified five NuGet packages, all published by the bmrxntfj account, that impersonate Chinese .NET UI and enterprise libraries.
The operator maintains just one visible version of each package at any time while rotating through unlisted builds, a strategy that inflates install counts while evading hash‑based detections.
Recently, version 2.1.55 for all five packages was pushed in a 12.78‑second scripted burst, then quickly superseded by newer versions once analysis started.
Malicious NuGet Packages
Execution begins as soon as any IR.* assembly is loaded, typically after a NuGet restore on a developer workstation or CI runner.
An MIT-licensed WinForms component library maintained on Gitee. The name “DantUI” is a one-character anagram of “AntdUI.”
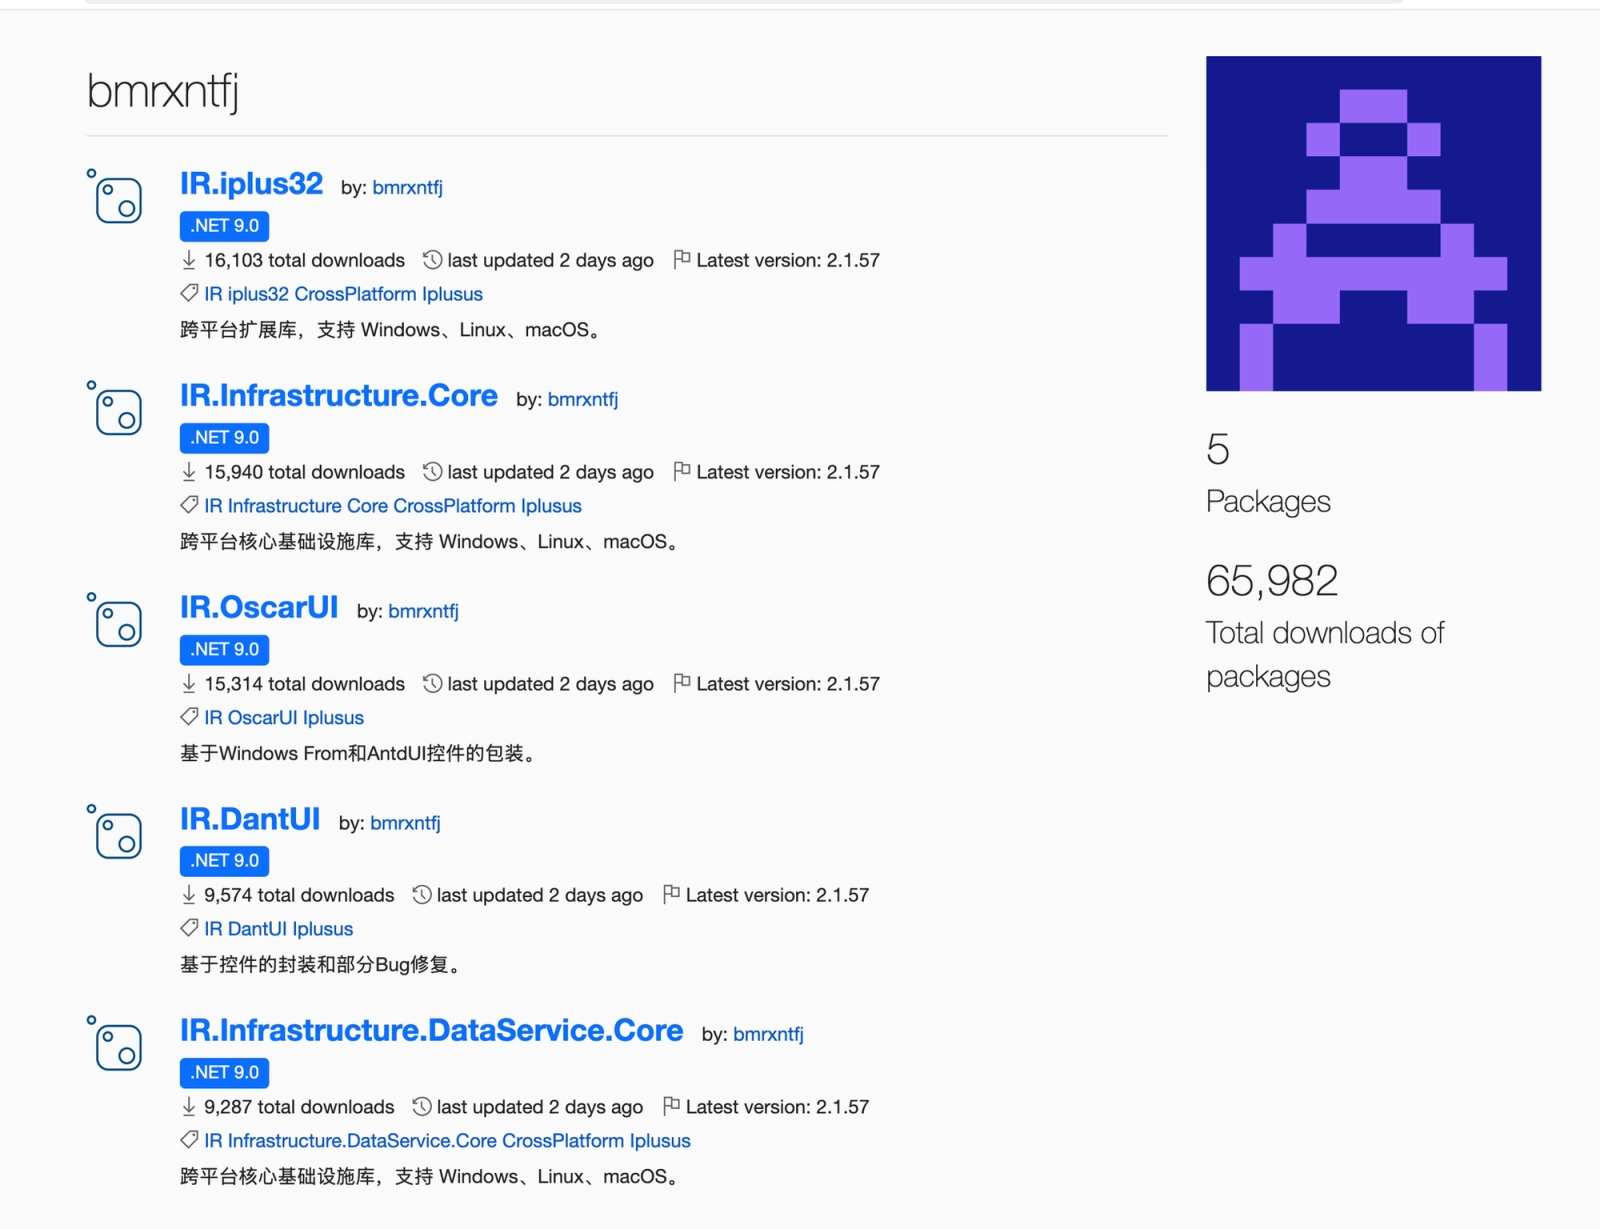
bmrxntfj NuGet profile showing all five IR.* packages (Source : Socket).The malicious module initializer invokes the .NET Reactor bootstrap, verifies an RSA‑1024 anti‑tamper signature, allocates read‑write‑execute memory, decrypts an encrypted stage‑2 blob, and hooks clrjit.dll!getJit so every method JIT‑compilation passes through attacker‑controlled code.
Cross‑platform support ensures that equivalent primitives are used on Linux via /proc/self/mem, mmap, and mprotect, and on macOS using libSystem and libclrjit symbols.
The Windows API P/Invoke stubs are obfuscated by dynamically reconstructing function names like OpenProcess at runtime to frustrate static scanners.
Once active, the decrypted infostealer (analyzed from we4ftg.exe) enumerates its capabilities via intact .NET metadata because Reactor’s Necrobit mode encrypts method bodies but not type names or strings.
This allows analysts to reconstruct its class graph and understand behavior even without fully unpacking the binary.
The core payload aggressively targets sensitive data across browsers, wallets, and local files. A BrowserKeyDecryptor component queries Chromium Login Data and Web Data databases, unsealing the master key via the IElevator COM interface, including support for Chrome’s newer v20 AppBound encryption introduced in mid‑2024.
At least 12 Chromium‑based browsers are supported, including Chrome, Edge, Brave, Opera, Vivaldi, Epic, Torch, Comodo, Slimjet, Iridium, 7Star, and AVG Secure Browser, with Firefox, Mozilla, and Thunderbird also within scope.
Payload analysis draws from we4ftg.exe, a 786 KB .NET MSIL assembly recovered from the memory dump described in the Attribution section.
Running ilspycmd --list assemblies against the rebuilt PE produces a complete class graph that names every capability without decrypting a single method body.
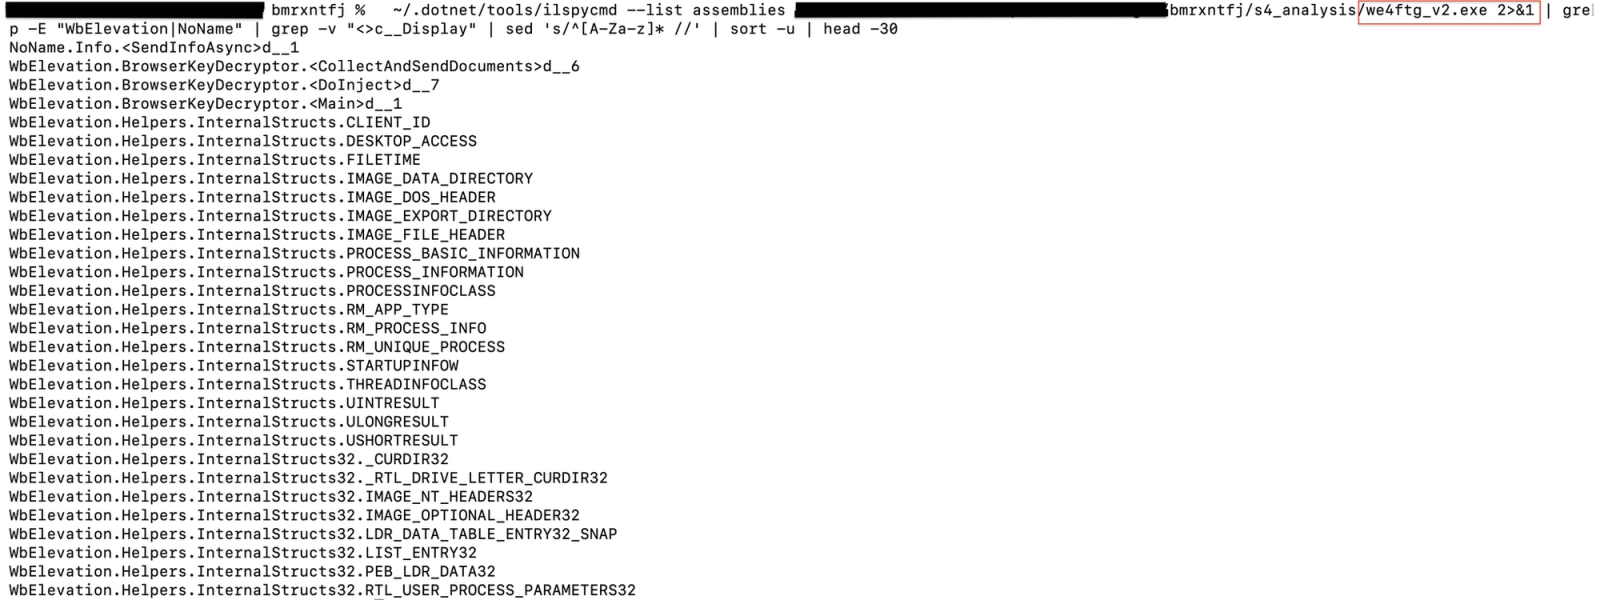
ilspycmd --list assemblies output for we4ftg.exe showing stealer class names recovered from unencrypted .NET metadata (Source : Socket).On the cryptocurrency side, the stealer hardcodes extension IDs for MetaMask, TronLink, Phantom, Trust Wallet, and Coinbase Wallet, walking their storage to extract wallet data.
It also searches desktop paths for Exodus, Electrum, Atomic, Guarda, Coinomi, Ledger, Jaxx, and Binance wallet files.
Beyond finance, it harvests SSH private keys (such as id_rsa), Outlook profiles, Steam session data, and recursively collects documents from the user’s Desktop, Documents, and Downloads directories.
Stolen content is staged under C:\ProgramData\Microsoft OneDrive\keys.dat a path chosen to blend into a legitimate OneDrive installation before being exfiltrated to https://dns-providersa2[.]com/upload using HTTP requests that carry randomized X-{3 lowercase letters} headers to avoid simple network signatures.
Attribution hinges on the .NET Reactor RSA public key embedded in all protected assemblies, which is unique per customer and therefore acts as a precise operator fingerprint.
Extracting the modulus from IR.iplus32 and pivoting on its base64 representation in VirusTotal links the NuGet packages to four additional artifacts, including a large s4.exe memory dump and fake CRYPT32.DLL.MUI and mscorrc.dll binaries, all sharing the same Reactor modulus.
Crowd‑sourced YARA rules label these samples with families such as Lumma, Quantum, AgentRacoon, and ArrowRAT, reflecting shared obfuscation rather than a definitive family match.
The primary command‑and‑control domain, dns-providersa2[.]com, was registered in March 2026 and resolves to a VDSINA VPS in Amsterdam, fronted through privacy‑focused registrar Njalla to resist WHOIS‑driven takedowns.
Analysts recovered both /check (beaconing and operator validation) and /upload (data exfiltration) endpoints from an in‑memory configuration dictionary extracted via regex from the s4.exe dump.
Two of the malicious nuspec files also reference git[.]justdotrip[.]com, a private Alibaba Cloud–hosted Git server believed to host the operator’s development environment.
Credentials, SSH Keys, and Crypto theft
Any environment that restored or loaded these five IR.* packages since September 2025 should be treated as compromised, regardless of whether the packages were ultimately used at runtime.
With around 65,000 total downloads, the blast radius spans tens of thousands of developer workstations and CI/CD build agents, exposing browser passwords, session cookies, payment data, SSH keys, email profiles, game accounts, and crypto assets to theft.
Defenders should immediately scan project files and packages.lock.json for the five package IDs, rotate all credentials reachable from affected systems, and block DNS resolutions and outbound traffic to dns-providersa2[.]com and 62[.]84[.]102[.]85.
Additional high‑value detections include monitoring for creation of C:\ProgramData\Microsoft OneDrive\keys.dat, CoCreateInstance calls for the Edge IElevator IID outside Edge processes, and suspicious HTTP requests from build infrastructure carrying short, random X-[a-z]{3} headers.
Longer‑term, organizations should harden their software supply chain with dependency‑aware scanners capable of spotting JIT‑hooking module initializers, typosquatted packages, and encrypted payloads before they land in development environments.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.