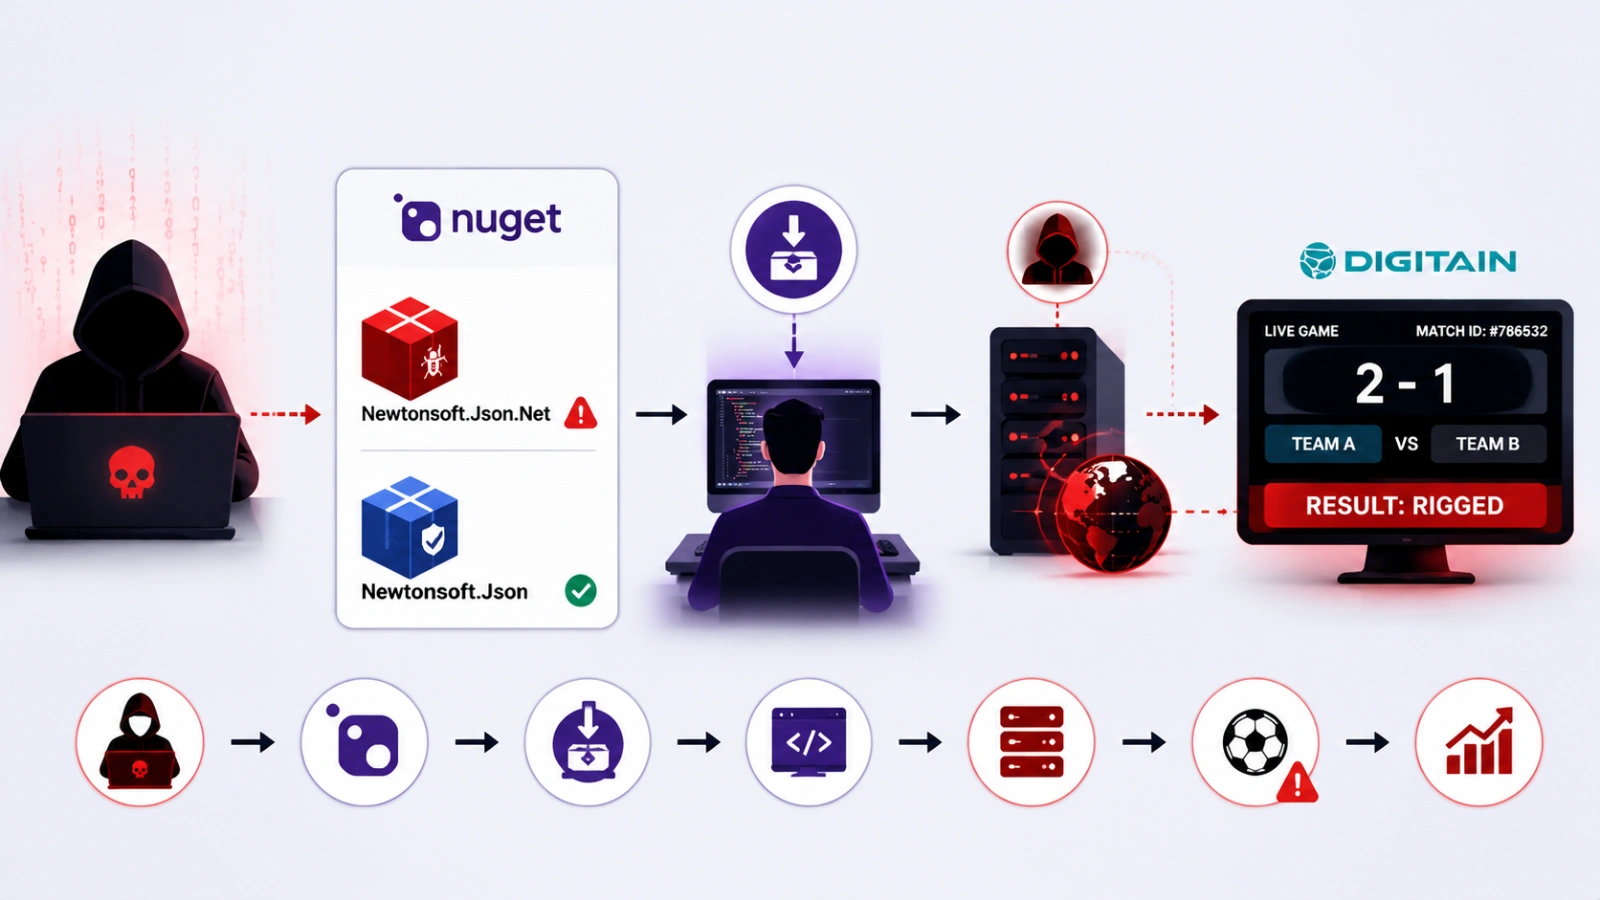

JFrog Security Research has disclosed a precision supply-chain attack in which a typosquatted NuGet package, Newtonsoftt.Json.Net, impersonated the ubiquitous Newtonsoft.Json library while secretly rigging game outcomes at online betting operator Digitain.
Unlike typical info-stealers that harvest credentials indiscriminately, this trojan functions as a fully operational JSON library for every host except its single intended target.
Malicious NuGet Typosquat Targets Digitain Betting Platform
The malicious package’s .nuspec metadata forged the identity of James Newton-King, pointed directly to the legitimate Json.NET project URL, and used a plausible-looking 11.0.x version scheme. It differed from the genuine library by only a doubled “t” and a .Net suffix.
Under lib/net8.0/, it shipped a trojanized fork of Newtonsoft.Json 13.0.3 alongside a payload DLL and the legitimate HarmonyLib runtime-patching library, all designed to auto-load into host processes.


Crucially, the package’s .nuspec file repeatedly leaked an internal TFS repository URL belonging to Digitain’s “BetOnGames / FG-Crash” project—effectively naming the target seven times across seven published versions.
This degree of specificity highlights how threat actors leverage supply chain attacks to execute surgical corporate fraud rather than opportunistic data theft.
The trojan activates only when a host application assigns JsonConvert.DefaultSettings, silently swapping the contract resolver while arming a Harmony patch on a delayed timer. In the latest generation, this delay is set to ten minutes, ensuring activation occurs long after application startup when diagnostic logs appear clean.

Once triggered, the payload patches Digitain.FG.SharedCrash.GameLogic.SharedCrashRules.GenerateGameResult, manipulating the crash-game coefficient using schedules keyed to date, time, and a special profile for the 22:00 UTC window. The rigging is bounded to a fixed number of rounds before the trojan unpatches itself to avoid ongoing detection.
The attacker iterated across seven package versions published between August and October 2025. The campaign progressed from a local-only proof of concept to an obfuscated exfiltration channel, and finally to an unobfuscated production build:
| Generation | Versions Published | Core Payload Capability | Applied Obfuscation |
| Gen-1 | 11.0.7, 11.0.8 | Console-only rigging, no networking calls | Dotfuscator |
| Gen-2 | 11.0.4, 11.0.5, 11.0.9 | Reflection-based exfiltration pipeline | ConfuserEx (heavy) |
| Gen-3 | 11.0.10, 11.0.11 | Direct HTTP postfix exfiltration to C2 | Light to none |
Gen-3 exfiltrated rigged results to a hardcoded command-and-control server disguised as a Seq structured-logging endpoint, using the header X-Seq-ApiKey: theperfectheist2025 to blend malicious traffic with normal application telemetry.

JFrog disclosed the malicious package to Digitain on July 7, 2026, and the company confirmed on July 9 that it was already aware of the issue and had resolved it.
Although the package was unlisted from NuGet search after October 2025, its artifacts remained downloadable. This persistence highlights the ongoing malicious package risks across open-source ecosystems.
Key Defensive Actions:
- Remove Dependencies: Delete
Newtonsoftt.Json.Netfrom all project manifests and global package caches (~/.nuget/packages). - Block C2 Infrastructure: Restrict outbound traffic to the C2 IP
185.126.237.64:5341. - Lock Dependencies: Pin
Newtonsoft.Jsonversions using lockfiles to prevent accidental typosquatting installations.
𝗔𝗜 𝗦𝗢𝗖 𝘃𝘀 𝗠𝗗𝗥 𝘃𝘀 𝗠𝗦𝗦𝗣 Which is Best in 2026? Compare costs, Automation, and response: Download Free Guide


