

A malicious fake RVTools installer is abusing a legitimately issued Sectigo code‑signing certificate to slip past Microsoft Defender SmartScreen and many endpoint controls, ultimately deploying a multi‑stage Python‑based RAT with deep AD reconnaissance and persistent C2 access.
For VMware‑heavy environments, compromise of an administrator via this vector can effectively hand over domain‑level control to the attacker.
The attacker distributes a trojanized RVTools MSI that is digitally signed with a Sectigo code‑signing certificate issued to “Xiamen Lunwei Huage Network Co., Ltd.,” a likely shell entity created solely to obtain a trusted publisher identity.
Because SmartScreen and many EDR products heavily rely on valid signatures and reputation for initial trust decisions, the signed installer runs without the usual “unrecognized app” warnings and appears indistinguishable from a legitimate enterprise tool.
Although the certificate has since been revoked, environments that do not enforce real‑time OCSP/CRL checks at execution time will still treat older signed binaries as valid, leaving a lingering exposure window.
Admins are accustomed to seeing signed installers and EULAs, so the presence of a standard license dialog, elevated privilege request, and reboot prompt all reinforce the illusion of legitimacy and encourage users to click through routine steps without suspicion.
The lure is a “normal‑looking” RVTools MSI installer that prompts for administrative rights to “manage virtualization infrastructure,” a request that appears entirely consistent with genuine RVTools behavior.
During installation, the MSI triggers a Custom Action that executes an embedded VBScript stored inside the package’s Binary table as Binary.MyScript.vbs, ensuring the malicious script never appears as a standalone file on disk before runtime.
The VBScript payload is heavily obfuscated using decimal‑to‑character encoding, where the true PowerShell command is represented as a long sequence of integers and rebuilt with Chr() at execution time.
K7 Security labs said in a report shared with GBhackers, RVTools is widely used by VMware administrators for inventory and visibility across vSphere environments, making it a high‑value impersonation target in enterprise networks.
This technique is designed to frustrate static scanners looking for suspicious tokens such as Invoke‑WebRequest or cloud‑storage URLs, significantly lowering initial detection rates on platforms like VirusTotal even while human analysts can spot behavioral red flags.
Malicious RVTools Installer Uses Sectigo
Once decoded, the script launches a hidden PowerShell instance that uses Invoke‑WebRequest to download a roughly 30–33 MB archive named winp.zip from a Dropbox URL into the %AppData% directory.
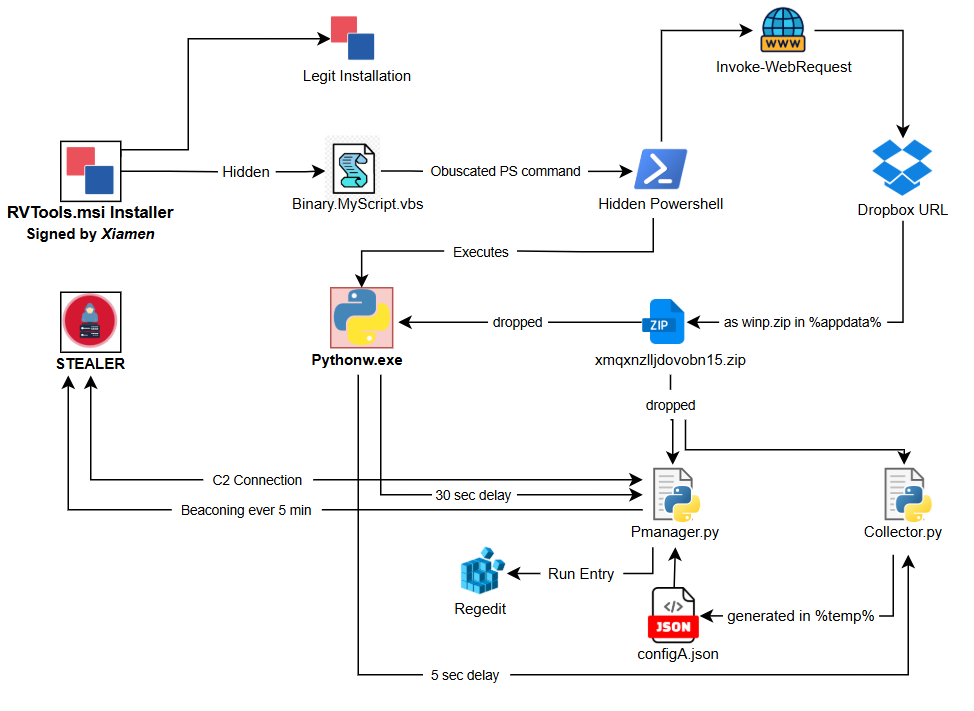
The archive is silently extracted, dropping a large collection of binaries and tools while the installer presents a seemingly benign reboot prompt framed as “cleaning installation artifacts,” which in reality finalizes persistence and prepares background agents for execution after restart.
The winp.zip payload doubles as a fully portable WinPython environment that bundles Python itself along with common developer IDEs and tools such as VS Code, Spyder, and Jupyter Lab.
To casual inspection or file‑system auditing, this looks like a legitimate developer stack being installed for an administrator, providing excellent cover for the embedded malicious scripts collector.py and Pmanager.py that drive the RAT’s behavior.
After a short five‑second delay, collector.py executes to fingerprint the compromised host and its domain context while remaining invisible to the user.
The script uses Windows startup flags such as STARTF_USESHOWWINDOW with wShowWindow set to 0 to run its PowerShell and subprocess calls entirely hidden, thwarting casual observation via the desktop or taskbar.
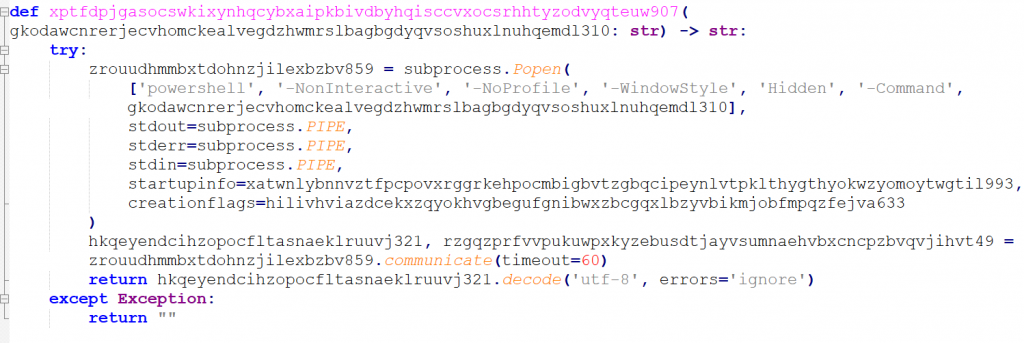
Collector.py is heavily obfuscated, using meaningless function and variable names to hinder reverse engineering and signature creation while it enumerates running processes, installed services, network connections, and Active Directory information.
A dedicated function calculates a unique 8‑character identifier by hashing the host’s MAC address and hostname, giving the operator a stable handle to track the victim across IP or network changes.
To assess domain value, the script leverages a PowerShell [adsisearcher] query, specifically ([adsisearcher]”(ObjectClass=computer)”).FindAll().Count, to count all computer objects in Active Directory and infer the size and complexity of the environment.
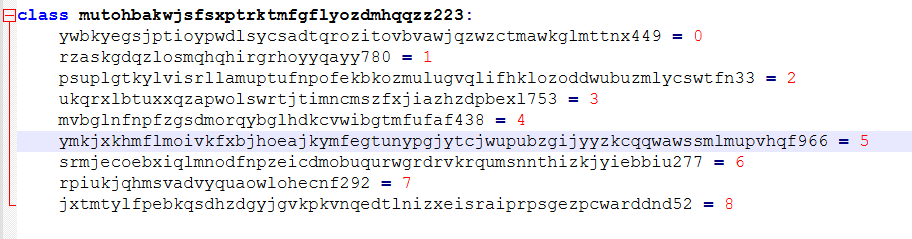
The wrapper method brrnhzl…772 then handles the actual data transformation by XORing the keystream against the target buffer, producing the encrypted or decrypted output.
Collected data, including local_id, privilege level (USER/ADMIN/SYSTEM), SIDs, group memberships (e.g., BUILTIN\Administrators), system details, and network topology, is stored locally in %TEMP%\configA.json for later staging and exfiltration.
After approximately 30 seconds, Pmanager.py takes over to establish persistence, exfiltrate staged data, and maintain hands‑on‑keyboard capability for the attacker.
The script first ensures long‑term access by creating an HKCU\…\Run registry entry and a scheduled task that runs daily with elevated privileges, providing redundant startup paths that survive reboots and some remediation attempts.
At its core, Pmanager.py implements a custom RC4‑based encryption class that performs key scheduling and a pseudo‑random generation algorithm (PRGA) to produce a keystream, then XORs it with the reconnaissance data to encrypt or decrypt buffers symmetrically.
Before exfiltration, data from configA.json is wrapped with a random 16‑byte salt, encrypted via RC4, and compressed with zlib, causing outbound C2 traffic to resemble random binary noise and complicate content‑based detection.
A separate “command enumerator” component maps numeric opcodes to actions such as executing EXE/DLL/MSI payloads, running Python or PowerShell scripts, adjusting beacon intervals, re‑asserting persistence, or self‑uninstalling when instructed.
The C2 engine cycles through five hardcoded IP addresses, choosing random URIs for HTTP POST requests and maintaining a 300‑second beacon interval under normal conditions, with faster 10‑second retries when connectivity fails to preserve access even under partial disruption.
This campaign underscores that a valid code‑signing certificate and familiar brand are no guarantee of safety; defenders must treat signed installers as starting points for scrutiny rather than automatic trust.
Behavioral controls should flag installers that spawn hidden PowerShell instances, reach out to cloud storage providers like Dropbox to download large archives, or drop full development environments into user profiles behaviors inconsistent with normal RVTools usage.
For organizations running VMware at scale, enforcing strong SmartScreen and reputation checks, validating download sources against official Dell/Robware RVTools distribution points, and monitoring for suspicious WinPython, VS Code, or Jupyter artifacts on infrastructure admin workstations are critical to preventing “game over” scenarios driven by a single compromised virtualization admin.
Indicators of Compromise (IoCs)
| File Name | Hash | Detection Name |
| d0f5e98fb840fb5656d3f50613b6f1ec60e57392643159841bc1fa95396087a4.msi | 64bda120cb447e0c03f451190022a57b | Trojan ( 0001140e1 ) |
| Binary.MyScript.vbs | 01A115C6F6BA3837234202A1E0D28BDC | Trojan ( 0001140e1 ) |
| Pmanager.py | 71085940124AD3C035A181ACADC10362 | Trojan ( 0001140e1 ) |
| collector.py | 9192D18A955A9D03E2C70B60AAC1784A | Trojan ( 0001140e1 ) |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


