

A destructive malware operation has been detected recently by the security experts at Microsoft Threat Intelligence Center (MSTIC) in which the threat actors are targeting several Ukrainian organizations and government agencies.
In this malicious campaign, the threat actors are targeting the MBR of affected or targeted systems in which they wipes the Master Boot Records (MBR).
While on January 13, 2022, in Ukraine this malware was first identified on the systems of its victim, and that’s why due to these ongoing malicious operations in Ukraine, Microsoft has urged organizations and agencies to stay alert to remain protected.
Are there any known associations behind these ongoing operations?
The straight answer to this question is, “NO,” since, till now Microsoft’s MSTIC has not detected any notable activity, but, they have tracked one as “DEV-0586.”
The most astonishing thing about this malware is that it’s designed to look like ransomware without a ransom recovery mechanism.
Why the operators have done this?
Instead of getting any ransom, the operators of this malware have specifically designed this malware to be destructive and induce the devices of their targets.
Orgs targeted
During the investigation, Microsoft has discovered multiple systems from multiple organizations were impacted due to this malware, and here we have mentioned the affected orgs below:-
- Multiple government organizations.
- Non-profit organizations.
- Information technology organizations.
Observed activity
The activity observed by the cybersecurity researchers are:-
- Overwrite Master Boot Record to display a faked ransom note.

- File corrupter malware
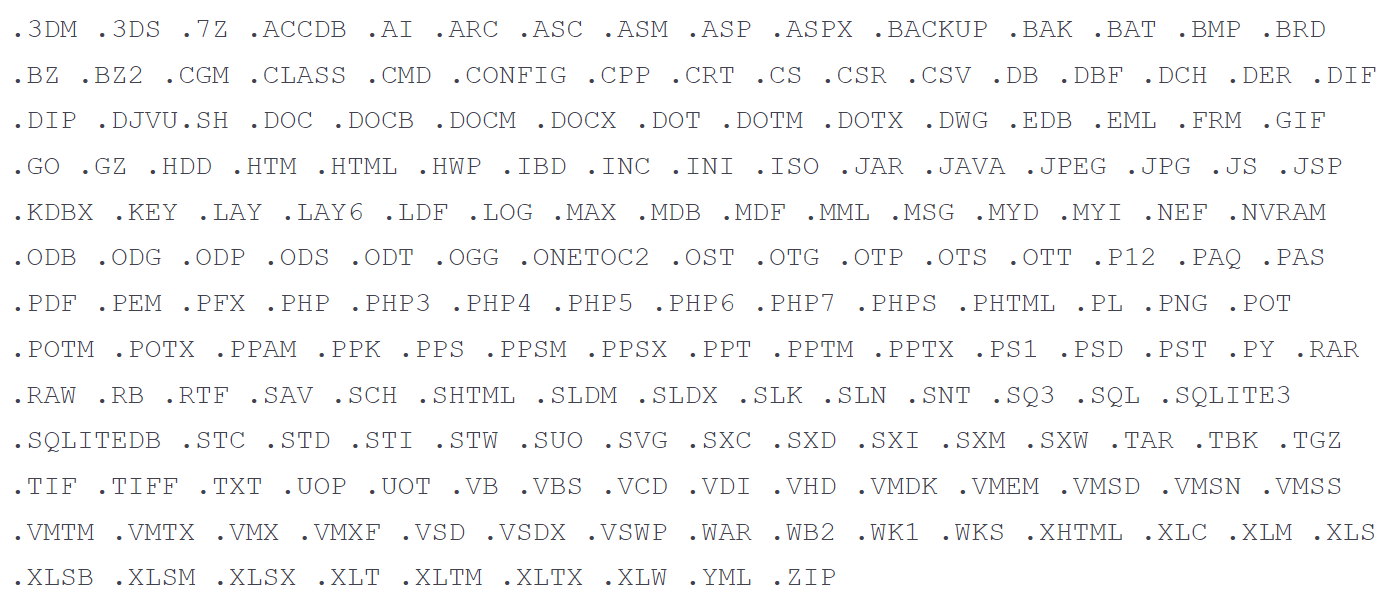
Apart from this, in the below image we have listed all the hardcoded file extensions used by the attackers.
Recommendations
To mitigate the techniques and procedures executed by the threat actors, the experts have recommended some security considerations that we have mentioned below:-
- Always investigate the IOCs provided.
- Always analyze your internal networks for potential intrusion.
- Always review all the authentication activity for remote access infrastructure.
- Make sure to configure the network configurations properly.
- Always enable two-factor authentication or MFA.
- Frequently change the passwords, and make sure to use strong passwords.
- To prevent MBR/VBR modification, always enable Controlled folder Access (CFA) in Microsoft Defender.
Moreover, this malware family has been denoted as WhisperGate, and Microsoft has also implemented several protections to detect this malware. While the users and organizations can utilize these security mechanisms through Microsoft Defender Antivirus and Microsoft Defender.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity updates






