
Internet-wide reconnaissance is expanding beyond conventional application targets to include Model Context Protocol (MCP) services, AI assistant configuration files, and locally exposed LLM endpoints.
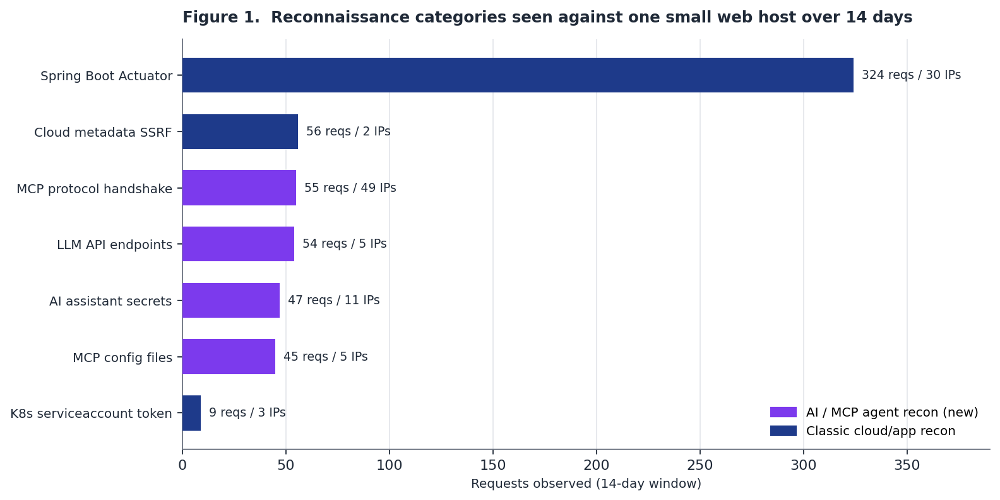
A 14-day review of Apache and ModSecurity logs from a small, low-traffic shared host found roughly 200 requests tied to AI-agent reconnaissance, alongside routine WordPress, .env, Git, and Spring Boot Actuator probing.
The activity did not appear to be accidental scanning. Attackers sent valid JSON-RPC MCP initialization requests to /mcp, attempted to locate configuration files from Claude, Cursor, and VS Code, and probed OpenAI-compatible and Ollama API endpoints.
Crucially, this AI-focused discovery traffic was accompanied by server-side request forgery (SSRF) attempts targeting Google Cloud’s metadata service, creating a potential path from exposed agent tooling to service account token theft.
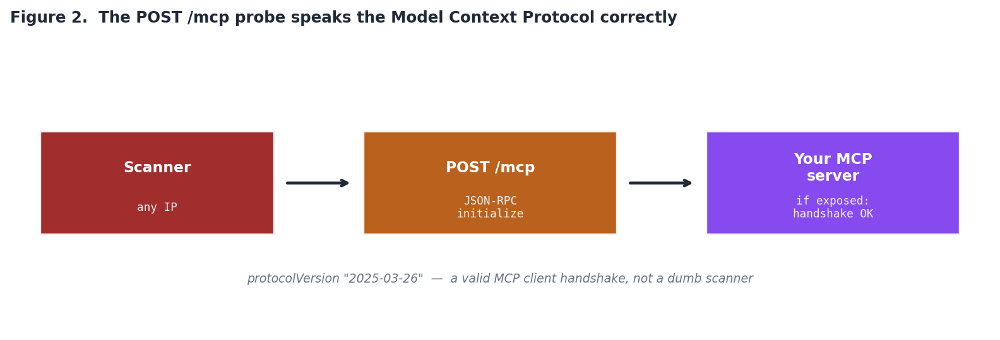
The most notable requests were POST /mcp probes carrying a correctly structured MCP initialize call using JSON-RPC 2.0 and the 2025-03-26 protocol version.
MCP uses an initialization lifecycle in which clients and servers negotiate protocol capabilities before tool discovery and interaction begin.
This is materially different from a simple path-existence check. A successful response can reveal that a host runs an MCP server and may enable an attacker to enumerate the tools, resources, prompts, or back-end services available to an AI client.
Since MCP is designed to connect LLM applications to external tools and data sources, an internet-exposed server can become a machine-readable entry point into databases, file systems, internal APIs, ticketing platforms, and cloud services.
The observed /mcp probes came from 49 distinct source IPs, suggesting broad distributed reconnaissance rather than isolated research.
Defenders should treat unsolicited MCP initialization traffic as a high-confidence discovery signal where no public MCP service is intentionally operated.
The same campaign requested AI-assistant artifacts including /.claude/mcp.json, /.cursor/mcp.json, /.cursor/mcp_config.json, /.vscode/mcp.json, /.mcp/config.json, and Claude credential paths.
These requests indicate that attackers are now treating developer-side AI configuration as a potential source of connection details, API keys, and credentials.
Use of HEAD requests against credential filenames is especially telling. It lets a scanner test whether a sensitive object exists without retrieving its contents, conserving bandwidth across a large target set.
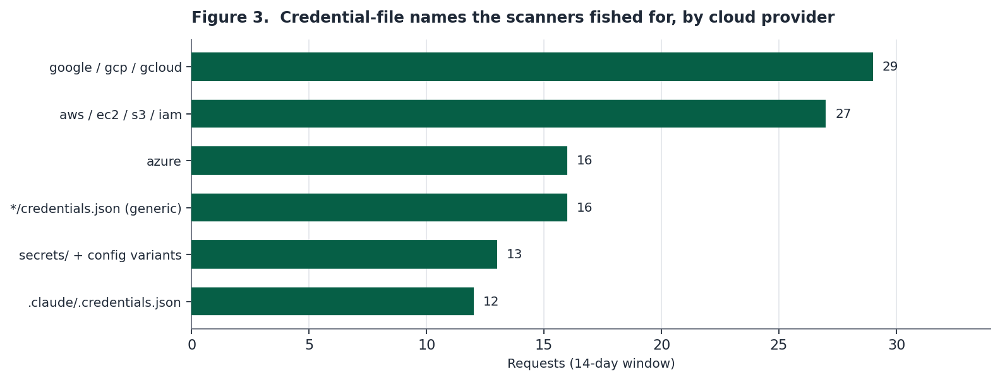
ISC Researchers said that, AI-specific paths appeared alongside conventional cloud credential filenames, Kubernetes secrets, and application configuration files evidence that AI tooling has become part of standard secret-harvesting wordlists.
Organizations should ensure .claude, .cursor, .vscode, .mcp, and home-directory configuration paths are never copied into production artifacts or mapped beneath a web-accessible document root.
Web servers should explicitly deny hidden configuration directories and sensitive JSON files, rather than relying only on deployment hygiene.
MCP Recon With Cloud Metadata SSRF
Attackers also repeatedly requested /v1/models, the common OpenAI-compatible model listing endpoint, and /api/tags, used by Ollama to enumerate installed models.
An unauthenticated response can expose inference infrastructure to abuse, model discovery, and follow-on exploitation.
More concerning were SSRF payloads directed at metadata.google.internal through parameters such as url, uri, path, and dest.
Generic credentials.json, then GCP, AWS, and Azure specific variants, then Kubernetes and application-specific names.
Google Compute Engine workloads can retrieve OAuth access tokens for their attached service accounts from the metadata server; requests require the Metadata-Flavor: Google header.
A vulnerable fetch, proxy, webhook, image-import, or agent tool that can reach the metadata service may therefore become a credential-exfiltration primitive.
The risk is amplified in MCP deployments because URL-retrieval tools are common. An exposed MCP server with an unrestricted “fetch URL” capability could provide an attacker both discovery and an SSRF path in one interface.
Search access logs for POST /mcp, /sse, AI configuration filenames, /v1/models, /api/tags, metadata.google.internal, and 169.254.169.254.
Block unauthenticated public MCP access, apply strict authorization to each tool, and restrict tool egress through allowlists.
Any URL-fetching feature should reject link-local, loopback, private, and cloud-metadata destinations after DNS resolution and on every redirect.
Cloud workloads should also use least-privilege service accounts, limiting the value of a stolen token. On AWS, enforcing IMDSv2 adds a session-token requirement that reduces exposure to many SSRF patterns.
Stop Accepting SLAs Written for 2019 SOCs – Here’s the 2026 AI SLA Vendor Checklist – Download Free AI SOC SLA Guide


 services, AI assistant configuration files.)