

Microsoft has addressed a critical use-after-free vulnerability in its Brokering File System (BFS) driver that could allow attackers to escalate privileges on Windows systems.
Tracked as CVE-2025-29970, the security flaw affects the bfs.sys component and was discovered by security researchers at HT3Labs.
Vulnerability Overview
The Brokering File System, introduced alongside Windows’ Win32 App Isolation feature approximately two years ago, is a mini-filter driver that manages I/O operations for isolated applications.
BFS specifically handles file access from sandboxed applications, making it a critical security boundary.
The vulnerability stems from improper memory management during the cleanup of policy entries within the driver.
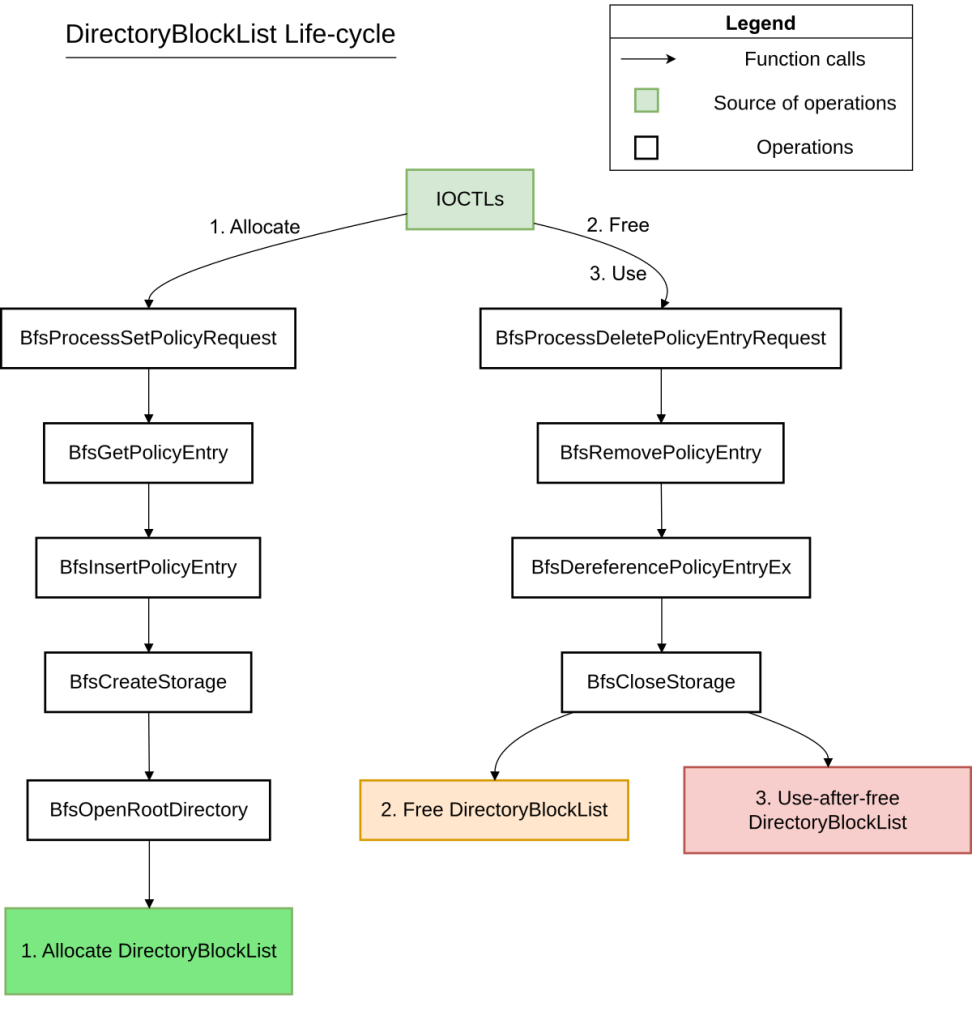
The flaw lies in the BfsCloseStorage function, where the DirectoryBlockList linked list is deallocated incorrectly.
During cleanup, the head of the linked list is freed at the end of the first iteration. However, the function continues to dereference this freed memory in subsequent iterations when processing additional entries.
This creates a classic use-after-free condition that can lead to system crashes or potentially privilege escalation.
When policies are removed through the BfsProcessDeletePolicyRequest IOCTL call, the system deallocates associated PolicyEntry objects and their members.
The vulnerability occurs during the StorageObject cleanup phase, where the deallocation loop in BfsCloseStorage improperly handles the DirectoryBlockList structure.
The function retrieves the first entry of the linked list, performs integrity checks, unlinks the node, deallocates the accompanying DirectoryBlockBuffer and the node itself, and then frees the list head all within a single iteration.
This flawed logic means that when a linked list contains multiple entries, the head is deallocated prematurely, leading to subsequent iterations accessing freed memory.
The tight window between memory deallocation and reuse makes exploitation challenging. However, attackers with local access and appropriate tokens could trigger the vulnerability.
To exploit CVE-2025-29970, attackers must satisfy several conditions. First, they need a handle containing a specific token that enables BFS IOCTL calls, typically obtained by impersonating a suitable process with an AppSilo token, as reported by PixieSecurity.
PolicyEntry objects must exist in the PolicyTable at the time of the removal request, and these entries must have an attached StorageObject with a DirectoryBlockList containing multiple entries.
While CVE-2025-29970 poses challenges for exploitation due to limited pointer usage and a narrow window of opportunity, it highlights ongoing security concerns with Windows sandboxing mechanisms.
As Microsoft expands application isolation features through AppContainer and AppSilo technologies, drivers like BFS represent increasingly attractive targets for privilege escalation attacks.
Security researchers recommend that organizations apply the latest Windows security updates promptly to protect against this and similar vulnerabilities in the Brokering File System.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


 driver that could allow attackers to escalate privileges on Windows systems.)